
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

1 GB of data belonging to Puma available on Marketo

The name of the sportswear manufacturer Puma appeared on the dark web marketplace of stolen data Marketo, threat actors claim to have stolen 1 GB of data from the company. The emerging underground marketplace of stolen data ‘Marketo’ available in TOR network announced the publication of data presumably stolen from sportswear manufacturer Puma.  The ad […]

Marketo Puma

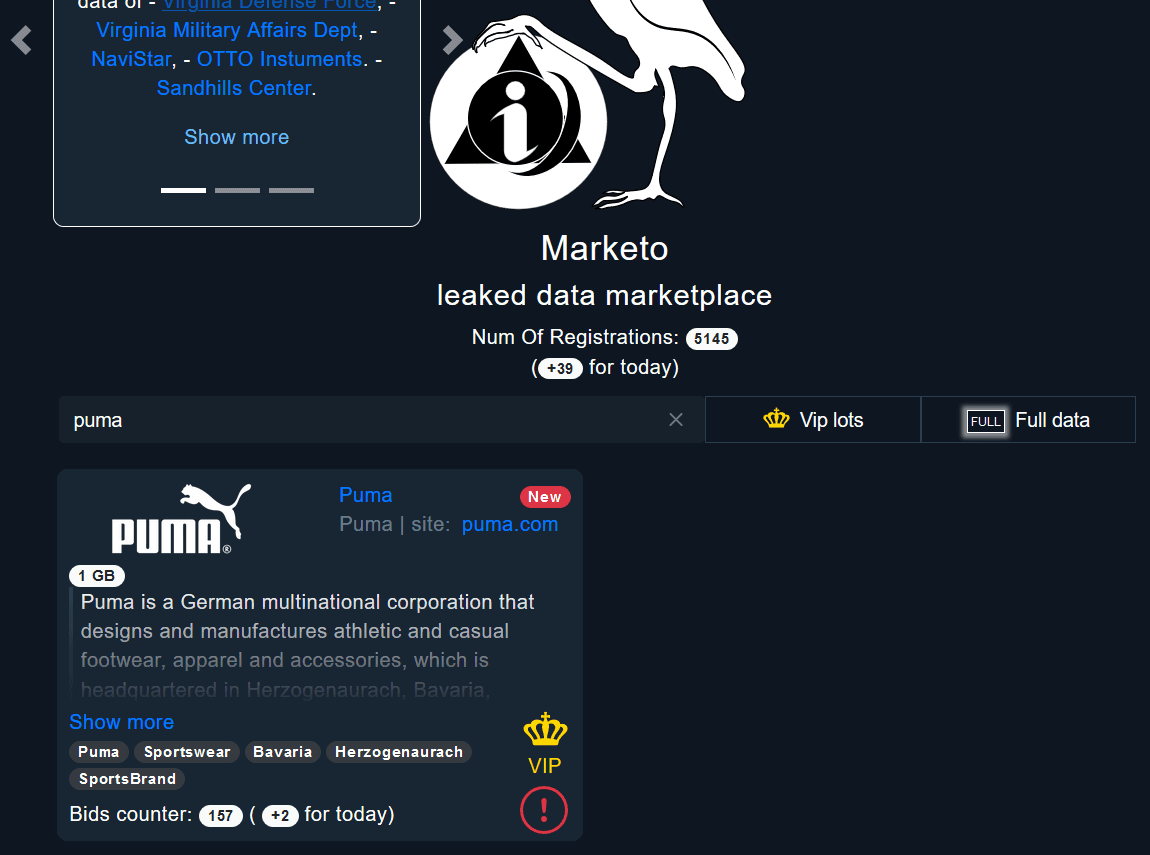
The name of the sportswear manufacturer Puma appeared on the dark web marketplace of stolen data Marketo, threat actors claim to have stolen 1 GB of data from the company.

The emerging underground marketplace of stolen data ‘Marketo’ available in TOR network announced the publication of data presumably stolen from sportswear manufacturer Puma. 

Marketo Puma

The ad on Marketo claims to have about 1GB of data stolen from the company that are now auctioned to the highest bidder. 

Cybercriminals behind ‘Marketo’ claim to be operators of an organized ‘marketplace of stolen data’ and not as a typical ransomware group distributing malicious code to disrupt IT operations by blocking the network of the victim and by encrypting available files on various data storage. 

One of the unique features provided by ‘Marketo’ – the ability to ‘bid’ on stolen data, which obviously creates competition between parties interested in data acquisition including the end victim.

At the time of this writing, 157 threat actors have made their bid to buy the sensitive data.

Some of the files stolen form Puma were published on Marketo, most of them contains source codes of internal management applications potentially linked to the company’s Product Management Portal. 

This data could be used by threat actors to orchestrate a more sophisticated attack against the company.

Experts that have analyzed the code have found evidence that the files of the organizations might have been stolen as result of a data breach of a third-party software provider.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, FIN8)

[adrotate banner=”5″]

[adrotate banner=”13″]


