
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Pwn2Own 2019 Day 2 – Hackers earned $270,000 for Firefox, Edge hacks

On the second day of the Pwn2Own 2019 hacking competition, white hat hackers earned a total of $270,000 for exploits against the Mozilla Firefox and Microsoft Edge web browsers. Day 2 at Pwn2Own 2019 hacking competition – White hat hackers earned $270,000 for exploits against the Mozilla Firefox and Microsoft Edge browsers. The security duo […]

VMware Pwn2Own 2019

On the second day of the Pwn2Own 2019 hacking competition, white hat hackers earned a total of $270,000 for exploits against the Mozilla Firefox and Microsoft Edge web browsers.

Day 2 at Pwn2Own 2019 hacking competition – White hat hackers earned $270,000 for exploits against the Mozilla Firefox and Microsoft Edge browsers.

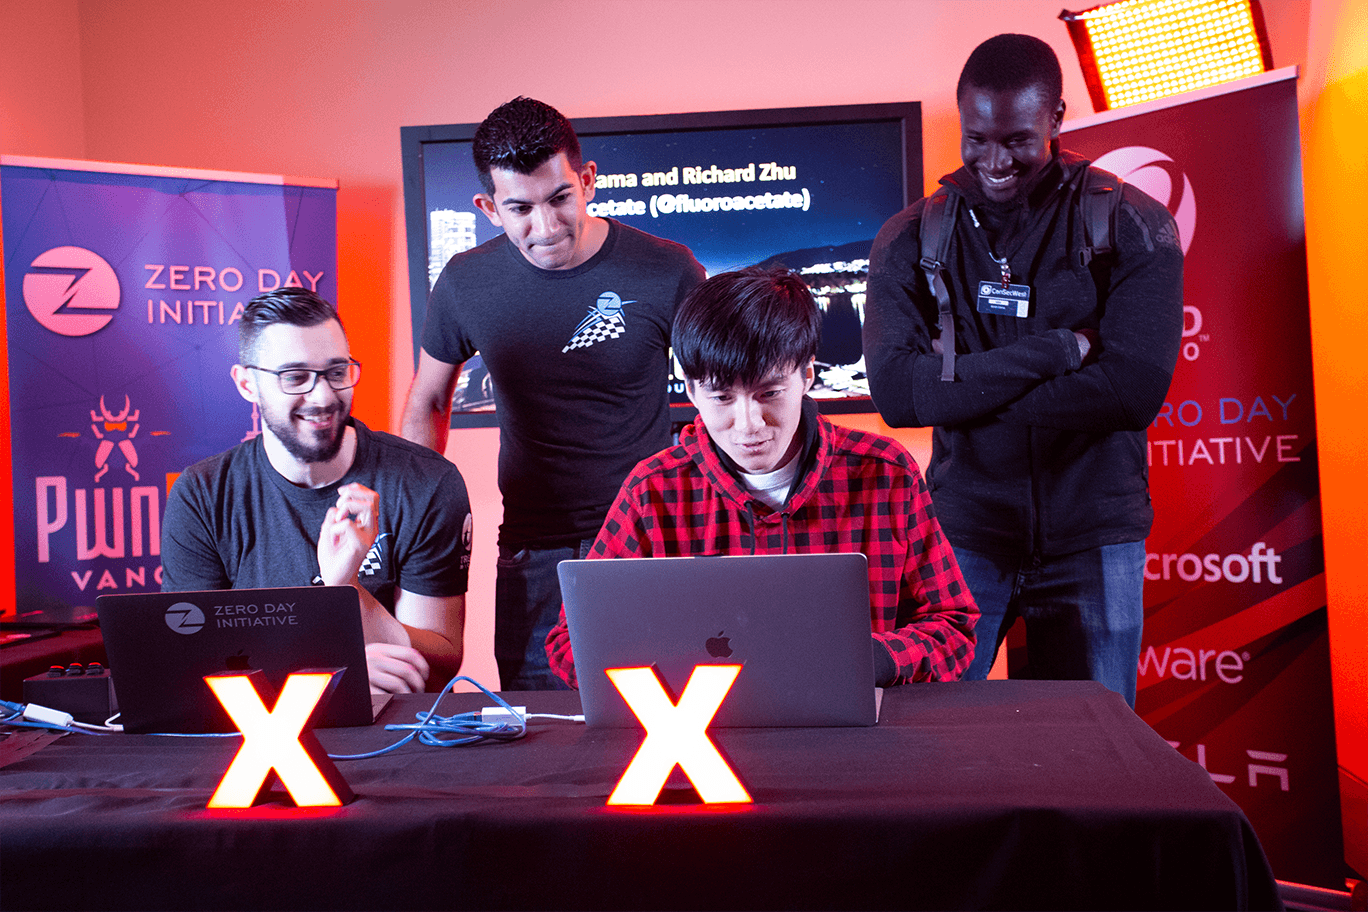
The security duo Amat Cama and Richard Zhu of team Fluoroacetate earned $50,000 for a Firefox exploit with kernel escalation. The experts chained a just-in-time (JIT) bug and an out-of-bounds write flaw in the Windows kernel.

“They were able to execute code at SYSTEM level just by using Firefox to visit their specially crafted website,” reads the post published by the Zero Day Initiative (ZDI). “The effort earned them another $50,000 and five more points towards Master of Pwn.”

Pwn2Own 2019

Amat Cama and Richard Zhu also earned $130,000 and 13 Master of Pwn points for a complex Edge hack that chained a race condition in the kernel to escalate privilege and an out-of-bounds write issue in VMware Workstation to escape the sandbox. The duo demonstrated that an attacker can exploit the bug in the web browser running in a virtual machine to execute arbitrary code on the host operating system.

The two experts already have racked up a total of $340,000 in the first teo days.

The second day of Pwn2Own 2019 sees Niklas Baumstark (@_niklasb) earning $40,000 and 4 Master of Pwn points for a JIT bug in Firefox and a logic flaw that allowed a sandbox escape.

“In a real-world scenario, an attacker could use this to run their code on a target system at the level of the logged-on user. The successful demonstration earned him $40,000 and 4 Master of Pwn points.” continues the post.

The last hack of the day was demonstrated by Arthur Gerkis of Exodus Intelligence that earned $50,000 for a Microsoft Edge exploit with a sandbox escape. The exploit leverages a double-free bug in the render component and a logic bug for bypassing the sandbox.

If you are interested in exploits demonstrated in the first day of the
Pwn2Own 2019 read here.

During the first day, participants hacked Apple Safari browser, Oracle VirtualBox and VMware Workstation.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Pwn2Own 2019 , hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


