Security Affairs
U.S. CISA adds IBM, SignalWire FreeSwitch, OpenSSH, and GPUStack flaws to its Known Exploited Vulnerabilities catalog|Russia-Linked APT Turla Turned Exchange Servers Into Their Own Control Room|iOS Sandbox Escape Is Public, and Apple Hasn’t Confirmed a Fix|Google fixes the eighth actively exploited Chrome zero-day of 2026|Iris Ohyama data breach may expose personal information of 7.7 million people|France Blames Iran for the Supermarket Fridge Attacks|QNAP Warns Users as Plex2Shell Flaws Are Used to Hack NAS Devices|CISA and the FBI Warn Of Attacks against Industrial Refrigeration Controllers|Fake GitHub Security Tools Infect Over 2,000 PCs With Malware|The BBC has a plan for a Black Sky event, and it runs on FM radio|Don’t Hand Propaganda a Gift: Reading the Brenner Base Tunnel SE Breach Calmly|SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 7|U.S. CISA adds IBM, SignalWire FreeSwitch, OpenSSH, and GPUStack flaws to its Known Exploited Vulnerabilities catalog|Russia-Linked APT Turla Turned Exchange Servers Into Their Own Control Room|iOS Sandbox Escape Is Public, and Apple Hasn’t Confirmed a Fix|Google fixes the eighth actively exploited Chrome zero-day of 2026|Iris Ohyama data breach may expose personal information of 7.7 million people|France Blames Iran for the Supermarket Fridge Attacks|QNAP Warns Users as Plex2Shell Flaws Are Used to Hack NAS Devices|CISA and the FBI Warn Of Attacks against Industrial Refrigeration Controllers|Fake GitHub Security Tools Infect Over 2,000 PCs With Malware|The BBC has a plan for a Black Sky event, and it runs on FM radio|Don’t Hand Propaganda a Gift: Reading the Brenner Base Tunnel SE Breach Calmly|SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 7|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Participants earned more than $1.3M at the Pwn2Own Automotive competition

Bug bounty hunters earned more than $1.3 million for hacking Teslas, infotainment systems, and electric vehicle chargers at the Pwn2Own Automotive competition. The Zero Day Initiative’s Pwn2Own Automotive competition has ended, participants demonstrated 49 zero-day vulnerabilities affecting automotive products earning a total of $1,323,750. The amazing Synacktiv team won the competition and earned a total […]

Pwn2Own Automotive

Bug bounty hunters earned more than $1.3 million for hacking Teslas, infotainment systems, and electric vehicle chargers at the Pwn2Own Automotive competition.

The Zero Day Initiative’s Pwn2Own Automotive competition has ended, participants demonstrated 49 zero-day vulnerabilities affecting automotive products earning a total of $1,323,750.

Pwn2Own Automotive

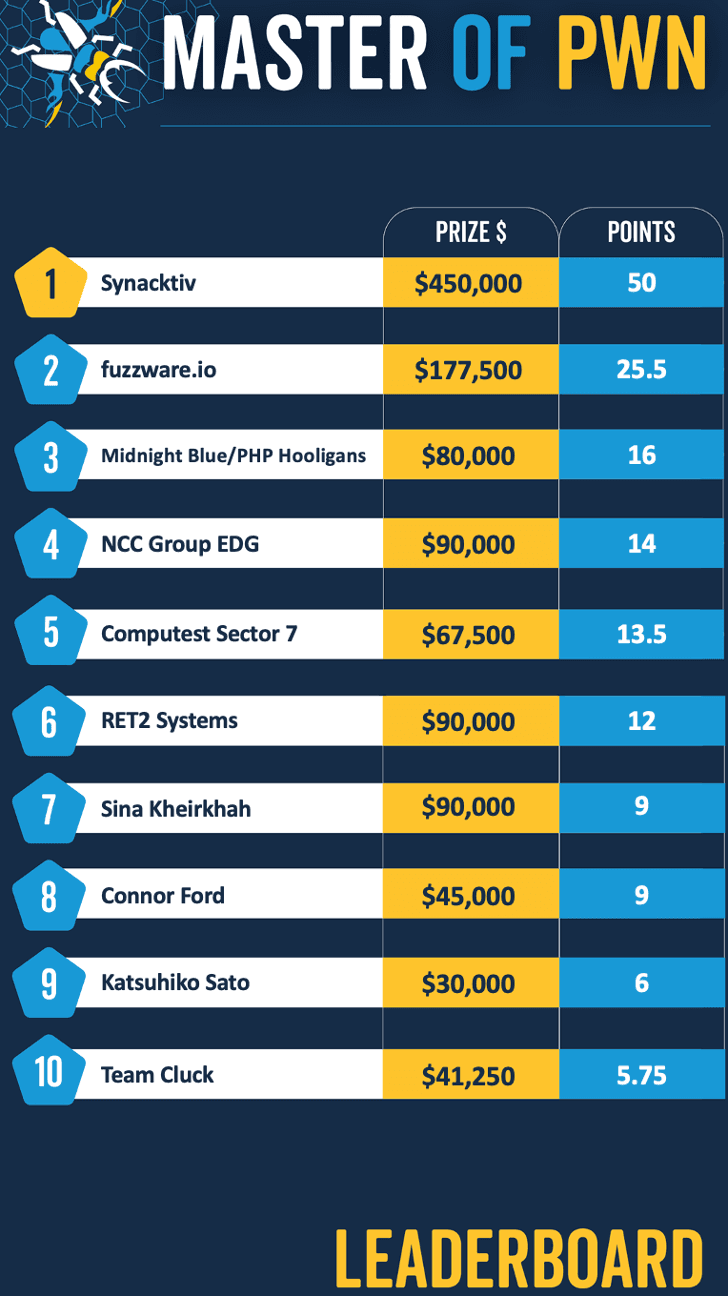
The amazing Synacktiv team won the competition and earned a total of $450,000. The team demonstrated successful attacks against Tesla’s modem and the infotainment system.

In second place is the team fuzzware.io with $177,500, followed by the team Midnight Blue/PHP Hooligans with $80,000.

The biggest payout was awarded to the team fuzzware.io that exploited a buffer overflow to hack the EMPORIA EV Charger Level 2. They earned $60,000 and 6 Master of Pwn Points.

The team fuzzware.io also chained to flaws to hack the Phoenix Contact CHARX SEC-3100. However, one of the bugs was previously known, for this reason, the attempt was classified as a a bug collision. They earned $22,500 and 4.5 Master of Pwn Points.

The researcher Connor Ford of Nettitude demonstrated a stack-based buffer overflow to hack the JuiceBox 40 Smart EV Charging Station. He earned $30,000 and 6 Master of Pwn Points.

The full list of the exploits demonstrated on day three of PWN2OWN AUTOMOTIVE 2024 is available here.

https://www.zerodayinitiative.com/blog/2024/1/25/pwn2own-automotive-2024-day-three-results

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Pwn2Own)