
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

French authorities released the PyLocky decryptor for versions 1 and 2

Good news for the victims of the pyLocky Ransomware versions 1 and 2, French authorities have released the pyLocky decryptor to decrypt the files for free. French authorities have released a decryptor for pyLocky Ransomware versions 1 and 2. The decryptor allows victims to decrypt their files for free. It was developed in collaboration between […]

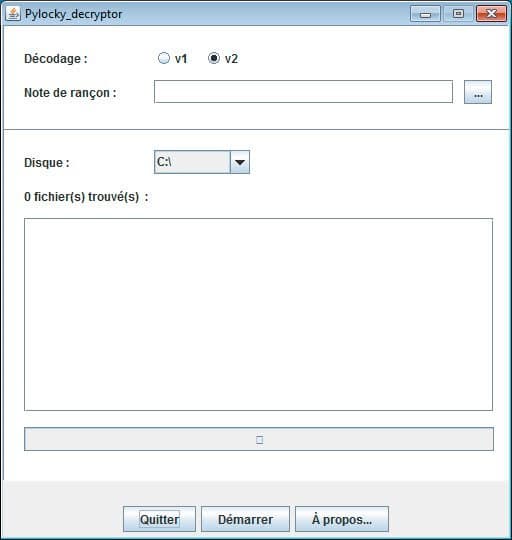
pyLocky Decryptor

Good news for the victims of the pyLocky Ransomware versions 1 and 2, French authorities have released the pyLocky decryptor to decrypt the files for free.

French authorities have released a decryptor for pyLocky Ransomware versions 1 and 2. The decryptor allows victims to decrypt their files for free. It was developed in collaboration between French law enforcement, the French Homeland Security Information Technology, and Systems Service, along with independent and volunteer researchers.

“PyLocky is very active in France, both within the professional environment (SMEs, large businesses, associations, etc.) as well as at home. This tool is a result of a collaborative Among the agencies of the french Ministry of Interior, Including the first Brigade of fraud investigations in information technology  (BEFTI) of the Regional Directorate of the Judicial Police of Paris , on the of technical elements gathered during its investigations and collaboration with volunteer researchers.” reads the post published by the French Ministry of Interior states it is more active in Europe.

“Those elements allowed the Homeland Security Information Technology and Systems Service ST (SI) ², part of the National Gendarmerie , to create that software.”

French Ministry of Interior pointed out that the ransomware hit many people in Europe, especially SMBs, large businesses, associations.

The pyLocky decryptor allows to decrypt file for version 1 (filenames having the .lockedfile or .lockymap extensions) and version 2 ( extensions .locky).

pyLocky Decryptor

The pyLocky Decryptor could be downloaded from the following link:

https://www.cybermalveillance.gouv.fr/wp-content/uploads/2019/02/PyLocky_Decryptor_V1_V2.zip

The decryptor has as pre-requisite the installation of the Java Runtime.

“This software decrypts the encryption of files with the extension .lockedfile or .lockymap and version 2 (encrypted files with the .locky extension) of PyLocky.” continues the report. “It requires a computer running the operating system Microsoft Windows 7 or higher and the execution environment Java JRE (Java Runtime Environment) version 8.”

The malware researcher Michael Gillespie analyzed the decryptor and noticed the presence of 2 hardcoded private RSA keys that were likely obtained by French police from the access to the C2 server hosted on the Tor network.

Let me remind you that the decryptor doesn’t clean the infected systems.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – pyLocky Decryptor, malware)

[adrotate banner=”5″]

[adrotate banner=”13″]


