
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

QAKBOT Trojan returns using Squirrelwaffle as a dropper

Experts warn of a surge in infections of the QBot (aka Quakbot) banking trojan which seems to be associated with the rise of Squirrelwaffle. Researchers warn of a new wave of QBot (aka Qakbot) banking trojan infections that appears to be associated with the rise of Squirrelwaffle. “Toward the end of September 2021, we noted […]

qakbot

Experts warn of a surge in infections of the QBot (aka Quakbot) banking trojan which seems to be associated with the rise of Squirrelwaffle.

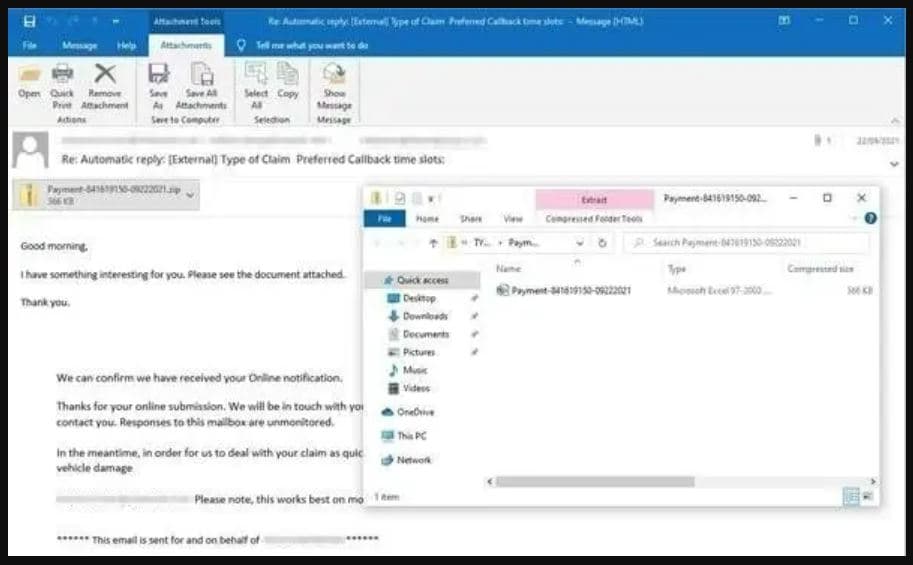
Researchers warn of a new wave of QBot (aka Qakbot) banking trojan infections that appears to be associated with the rise of Squirrelwaffle.

“Toward the end of September 2021, we noted that QAKBOT operators resumed email spam operations after an almost three-month hiatus. Specifically, we saw that the malware distributor “TR” was sending malicious spam leading victims to SquirrelWaffle (another malware loader) and QAKBOT.” states the report published by Trend Micro.

Squirrelwaffle was first spotted in October by Cisco Talos researchers, it was spreading via malspam campaigns to deliver malware onto compromised systems and networks.

The malware was observed dropping Qakbot and Cobalt Strike in recent campaigns.

Unlike previous QAKBOT campaigns, the most recent wave of attacks uses Visual Basic for Applications (VBA) macros alongside Excel 4.0 macros.

qakbot

Upon opening the attachment and enabling the macro (“Enable Content”) the attack chain will start leading to the installation of the QBot payload on the system.

“When a victim opens the malicious file in their spam email, an auto_open macro will try to create a new sheet and set the font color to white.” continues the analysis published by Trend Micro. “The macro then assigns the values to cells in “Sheet 5” and evaluates and concatenates the command to download the QAKBOT DLL from a remote host. The process chain has also altered slightly with regsvr32.exe using -silent instead of -s parameter. The DLL download URL still uses now() to form the DLL name. The macro then deletes the “Sheet5” when the document is closed.”

QAKBOT continues to use the same scheduled task to gain persistence.

QAKBOT is a key “malware installation-as-a-service” botnet that enables many campaigns, in was used by multiple ransomware operations including REvil, Egregor, ProLock, and MegaCortex.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, malware)

[adrotate banner=”5″]

[adrotate banner=”13″]


