
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Over 30k Internet-Exposed QNAP NAS hosts impacted by CVE-2022-27596 flaw

Censys found 30,000 internet-facing QNAP appliances potentially impacted by a recently disclosed critical code injection flaw. On January 30, Taiwanese vendor QNAP released QTS and QuTS firmware updates to address a critical vulnerability, tracked as CVE-2022-27596 (CVSS v3 score: 9.8), that affects QNAP NAS devices. A remote attacker can exploit the vulnerability to inject malicious code […]

QNAP

Censys found 30,000 internet-facing QNAP appliances potentially impacted by a recently disclosed critical code injection flaw.

On January 30, Taiwanese vendor QNAP released QTS and QuTS firmware updates to address a critical vulnerability, tracked as CVE-2022-27596 (CVSS v3 score: 9.8), that affects QNAP NAS devices.

A remote attacker can exploit the vulnerability to inject malicious code on QNAP NAS devices. The flaw is easy to exploit without user interaction or privileges on the vulnerable device.

The flaw impacts QTS 5.0.1 and QuTS hero h5.0.1 versions.

“A vulnerability has been reported to affect QNAP devices running QTS 5.0.1 and QuTS hero h5.0.1. If exploited, this vulnerability allows remote attackers to inject malicious code.” reads the advisory published by the Taiwanese vendor.

The company fixed the vulnerability in the following operating system versions:

  • QTS 5.0.1.2234 build 20221201 and later
  • QuTS hero h5.0.1.2248 build 20221215 and later”

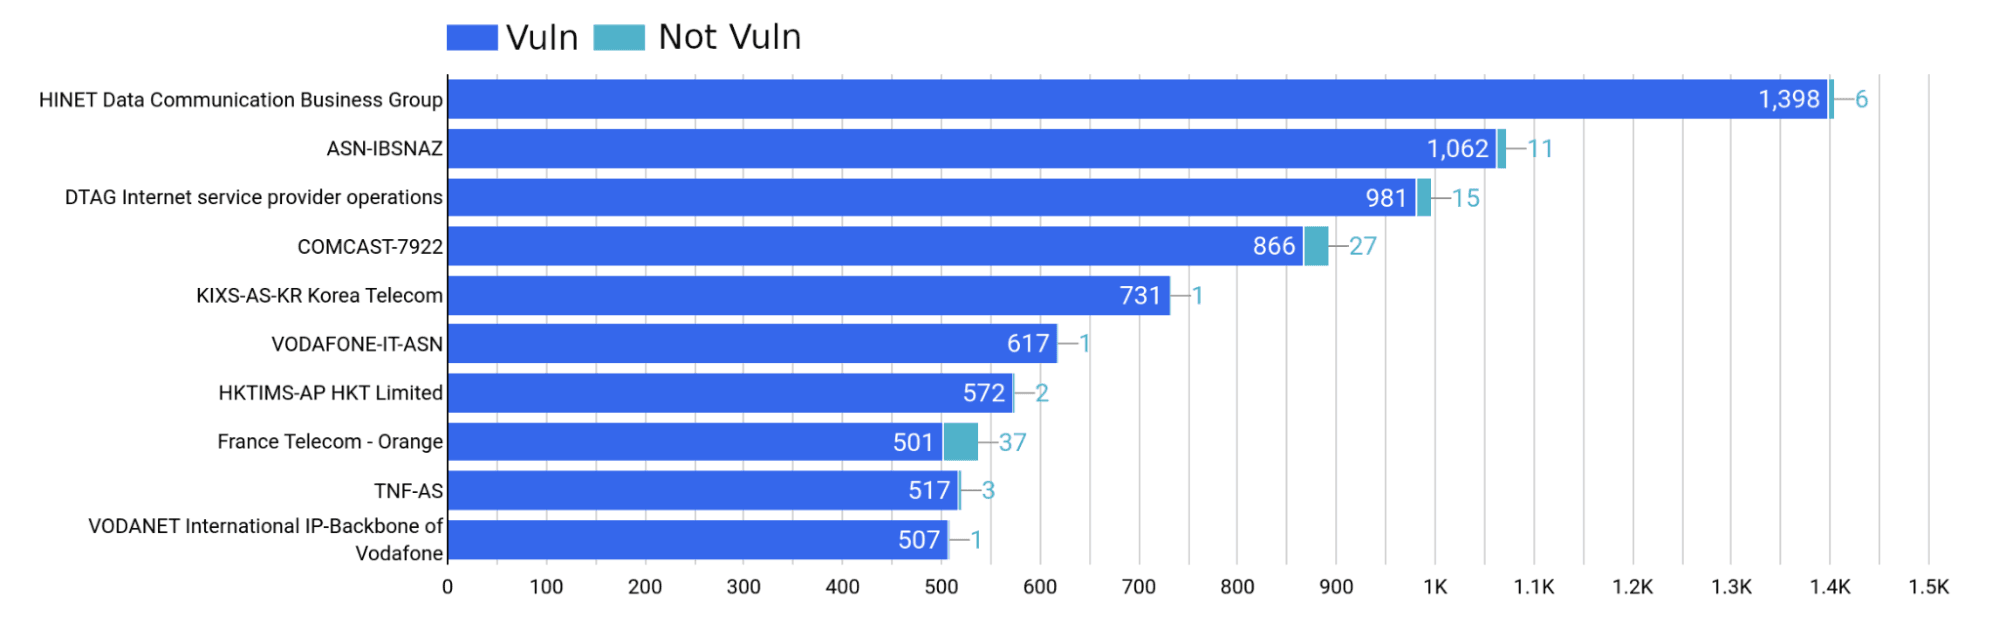
Cyber security firm Censys scanned the Internet for internet-exposed QNAP appliances and discovered 30,000 devices that are likely affected by the CVE-2022-27596 flaw because are running QTS 5.0.1 and QuTS hero h5.0.1 vulnerable versions.

Censys discovered 67,415 hosts allegedly running a QNAP-based system, but they were able to obtain the version number only from 30,520 hosts.

“But, if the advisory is correct, over 98% of identified QNAP devices would be vulnerable to this attack. We found that of the 30,520 hosts with a version, only 557 were running QuTS Hero greater than or equal to “h5.0.1.2248” or QTS greater than or equal to “5.0.1.2234”, meaning 29,968 hosts could be affected by this vulnerability.” reads the report published by Censys. “If the exploit is published and weaponized, it could spell trouble to thousands of QNAP users. Everyone must upgrade their QNAP devices immediately to be safe from future ransomware campaigns.””

Most of the vulnerable hosts discovered by Censys are in Italy (3,200), followed by the US (3,149) and Taiwan (1,942).

QNAP

Experts used the advisory (QSA-23-01) to determine vulnerable versions, and discovered that the Top Vulnerable versions are:

VersionHost Count
5.0.07.383
4.3.36,993
4.3.64,777

“while there are no indications that bad actors are using this new exploit, the threat is definitely on the horizon.” Censys concludes.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, IoT)


