
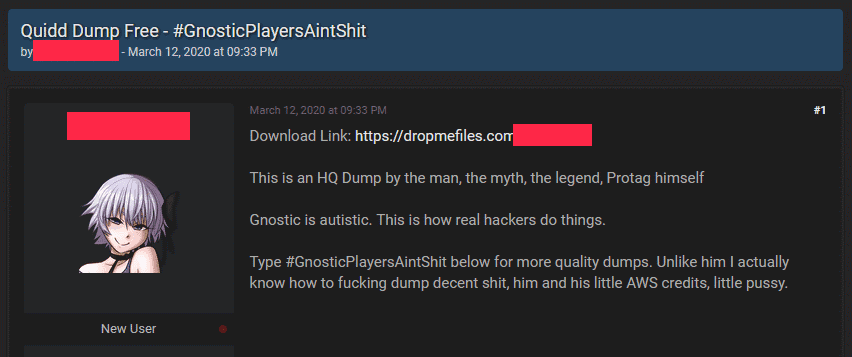
Quidd , an online marketplace for trading stickers, cards, toys, and other collectibles, discloses a data breach in has suffered in 2019.
The details of around four million users are now being shared for free on underground hacking forums, according to ZDNet that has obtained samples from different sources, exposed records include usernames, email addresses, and hashed account passwords (bcrypt hashing algorithm).
The data breach was first reported by Risk Based Security last week, since then, Quidd has never disclosed any data breach recent security incident.
“The credentials of nearly 4 million Quidd users have recently been discovered by our Data Breach Research team on a prominent deep web hacking forum. At this time, the leaked data has not been offered for sale but is available in a non-restricted manner.” reads the post published Risk Based Security.
“The compromised data sets were originally posted on March 12th, 2020 and self-attributed to a threat actor named “Protag”. However, the files were quickly removed. The data resurfaced on March 29th, 2020 when it was reuploaded by a different user and has since remained available. One threat actor responded to the post stating that he has already cracked, or decrypted, nearly a million password hashes.”
ZDNet investigated the data leak and discovered that a hacker that goes online with the moniker ProTag was the one who took credit for the data, the media outlet also confirmed that data are authentic after contacting some Quidd users.
Experts believe that Quidd dump is available in private high-level groups for months, it was advertised on hacking forums and Pastebin since at least October.
“But while the data has traded privately in exclusive rings for months, the Quidd user info has now leaked into the public domain.” reported ZDNet.
“This happened last month after a data trader posted a copy of the Quidd data on a publicly accessible hacker forum.”
Data is now available on multiple hacking forums and several sellers are sharing download links for the huge trove of data.

Even if the bcrypt hashing algorithm is very hard to crack, it could quite easy to calculate the hash for weak passwords, and this is the work that some hackers are already doing on the Quidd dump.
Risk-Based Security is aware of a hacker that is claiming to provide access to more than one million cracked Quidd accounts, while ZDnet reported that a hacker is currently selling access to more than 135,000 cracked Quidd passwords,
If you are a Quidd user don’t waste time and change the account password now.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – Quidd, data breach)
[adrotate banner=”5″]
[adrotate banner=”13″]


