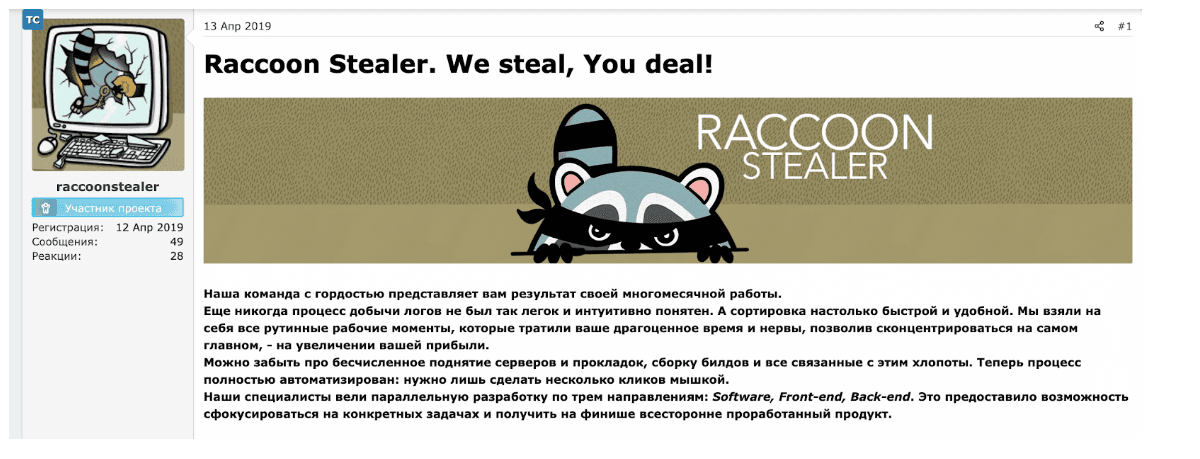
A new information stealer, dubbed Raccoon, made the headlines infecting hundreds of millions of victims worldwide.
Security experts at Cybereason have spotted a new information stealer, dubbed Raccoon, that is infecting hundreds of millions of victims worldwide.
The malware was designed to steal victims’ credit card data, email credentials, cryptocurrency wallets, and other sensitive data.
The malware is offered with a malware-as-a-service (MaaS) model that allowed the threat to rapidly gain popularity in the cybercriminal ecosystem.
“The Raccoon stealer is one of the 2019 top 10 most-mentioned malware in the underground economy and is widely known to have infected hundreds of thousands of devices around the world, despite it not being overly sophisticated or innovative.” reads the analysis published by Cybereason.
“Its popularity, even with a limited feature set, signals the continuation of a growing trend of the of malware as they follow a (Malware-as-a-Service) model and evolve their efforts.”
Raccoon is offered for sale as a MaaS that implements an easy-to-use automated backend panel, operators also offer bulletproof hosting and 24/7 customer support in both Russian and English. The price for the Raccoon service is $200 per month to use.
The experts explained that the Raccoon malware is not sophisticated but leverages several potential attack vectors and is able to steal a large quantity of sensitive data.
Raccoon is written in C++ by Russian-speaking developers that initially promoted it exclusively on Russian-speaking hacking forums. The malware is now promoted on English-speeaking hacking forums, it works on both 32-bit and 64-bit operating systems.
The analysis of the logs for sale in the underground community allowed the experts to estimate that Raccoon has already infected over 100,000 users worldwide. The key to its success is the simplicity to arrange malware campaigns through the MaaS model that allows both technical and nontechnical individuals alike to monetize their efforts.
The malware was first spotted in April 2019, it is actively distributed via multiple exploit kits, including Fallout and RIG, and phishing campaigns.
“Many in the community praise and endorse Raccoon’s malware capabilities and the services the team provides,” researchers said. “Some voices in the community even endorse it as a worthy replacement for the famous Azorult stealer.” conclude the expert. “Though the Raccoon stealer may not be the most innovative infostealer on the market, it is still gaining significant traction in the underground community. Based on testimonials from the underground community, The Raccoon team provides reliable customer service to give cybercriminals a quick-and-easy way to commit cybercrime without a huge personal investment.”
|
[adrotate
banner=”9″]
|
[adrotate
banner=”12″]
|
Pierluigi Paganini
(SecurityAffairs – Raccoon info stealer, MaaS)
[adrotate
banner=”5″]
[adrotate
banner=”13″]