
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

A database containing 478,000 RaidForums members leaked online

The database of the popular RaidForums hacking forum has been leaked on a new hacking forum, 478,000 members exposed. A database belonging to the now-defunct RaidForums cybercrime platform has been leaked on a new hacking forum called Exposed. The database contains data belonging to 478,000 RaidForums members. In April 2022, the illegal dark web marketplace […]

Raidforums

The database of the popular RaidForums hacking forum has been leaked on a new hacking forum, 478,000 members exposed.

A database belonging to the now-defunct RaidForums cybercrime platform has been leaked on a new hacking forum called Exposed. The database contains data belonging to 478,000 RaidForums members.

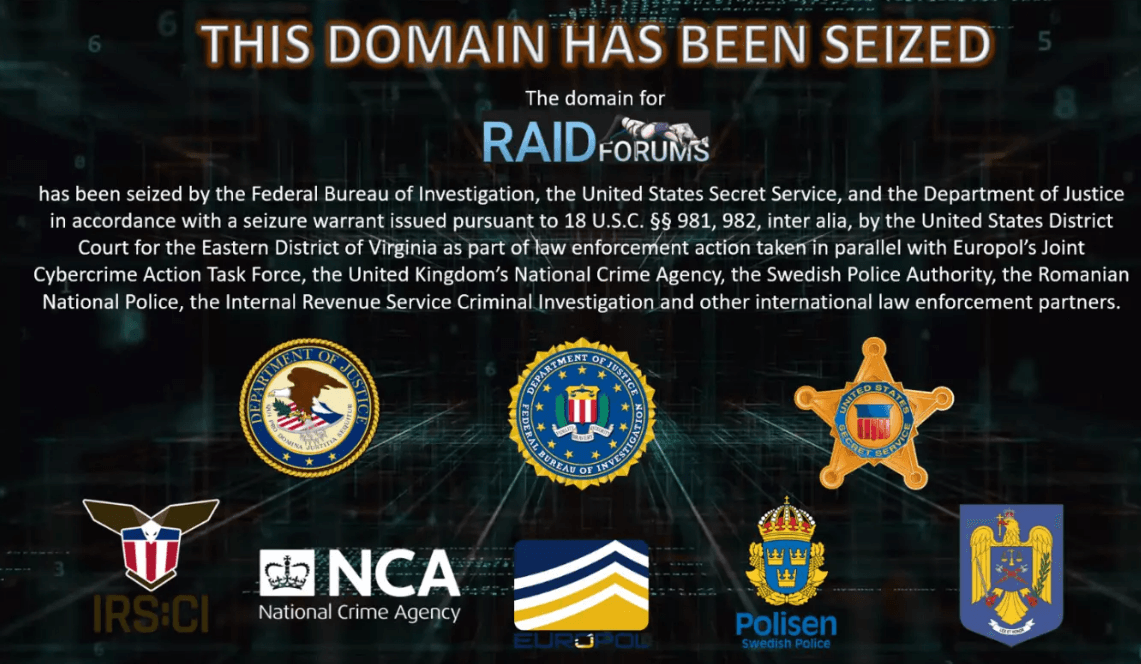
In April 2022, the illegal dark web marketplace RaidForums has been shut down and its infrastructure was seized as a result of the international law enforcement Operation TOURNIQUET coordinated by Europol’s European Cybercrime Centre.

RaidForums was launched in 2015, its community reached over half a million users. The marketplace gained popularity for the sale of high-profile database leaks belonging to a number of US corporations across different industries.

After Raidforums was seized, the Breached hacking forums become the most prominent darkweb marketplace for the trading of stolen data. The good news is that in March 2023, U.S. law enforcement arrested the notorious owner of the BreachForums cybercrime forum known as Pompompurin and seized the Breached platform.

Bleeping Computer first reported that the RaidForums member database was leaked on the Exposed forum by one of its administrators, known as ‘Impotent.’

The leaked database contains precious data for cybersecurity experts and investigators to analyze the operations of the hacking forums and their members.

The leaked database is a single SQL file containing the table ‘mybb_users.’ Each record in the table includes usernames, email addresses, hashed passwords, registration dates, and a variety of other information.

The data are related to members registered between March 20th, 2015, and September 24th, 2020.

BleepingComputer and some members of the Exposed forum have already confirmed that the data in the database are legitimate.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, phishing)


