
Security Affairs
U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Human resource consulting giant Randstad hit by Egregor ransomware

Multinational human resource consulting firm Randstad NV announced that they were a victim of the Egregor ransomware. Egregor ransomware operators have breached the network of the multinational human resource consulting firm Randstad NV and have stolen unencrypted files during the attack. Randstad operates in 39 countries and employs over 38,000 people and generated €23.7 billion in revenue for […]

randstad Egregor ransomware

Multinational human resource consulting firm Randstad NV announced that they were a victim of the Egregor ransomware.

Egregor ransomware operators have breached the network of the multinational human resource consulting firm Randstad NV and have stolen unencrypted files during the attack.

Randstad operates in 39 countries and employs over 38,000 people and generated €23.7 billion in revenue for 2019.

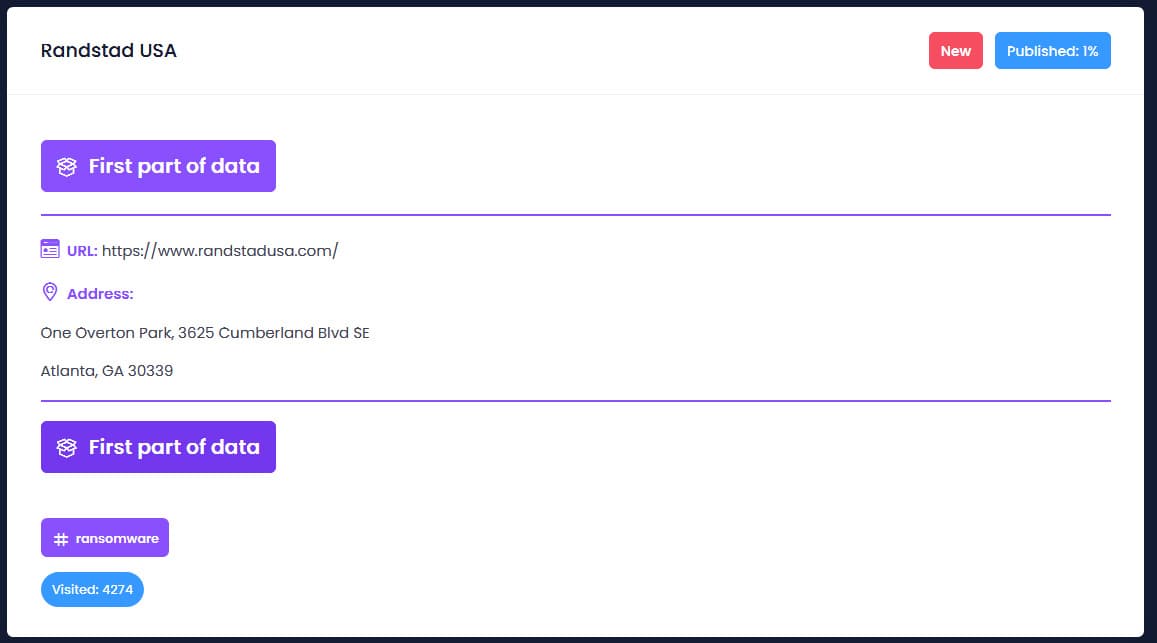
The Egregor ransomware operators published 1% of the alleged stolen data as proof of the attack. The archive is 32.7MB in size and contains 184 files.

The leaked files include financial reports, legal documents, and accounting spreadsheets.

Source Bleeping Computer

Randstad published a data breach notification to disclose the incident and confirmed that the Egregor ransomware infected its systems.

“Randstad NV (“Randstad”) recently became aware of malicious activity in its IT environment and an internal investigation into this incident was launched immediately with our 24/7 incident response team. Third party cyber security and forensic experts were engaged to assist with the investigation and remediation of the incident.” reads the statement published by the company.

The human resource consulting firm revealed that the malware only infected a limited number of servers and that the operations were not impacted.

The company added that attackers accessed data related to their operations in the US, Poland, Italy, and France, but the investigation is still ongoing.

“To date, our investigation has revealed that the Egregor group obtained unauthorized and unlawful access to our global IT environment and to certain data, in particular related to our operations in the US, Poland, Italy and France. They have now published what is claimed to be a subset of that data.” continues the notification. “The investigation is ongoing to identify what data has been accessed, including personal data, so that we can take appropriate action with regard to identifying and notifying relevant parties.” 

Egregor ransomware operators are very active in this period, this week they hit Metro Vancouver’s transportation agency TransLink causing the disruption of its services and payment systems.

The ransomware gang recently targeted several other major companies worldwide, including Barnes and Noble, Cencosud, Crytek, Kmart, and Ubisoft.

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Randstad)

[adrotate banner=”5″]

[adrotate banner=”13″]


