
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Ransomware gangs are exploiting CVE-2022-26134 RCE in Atlassian Confluence servers

Ransomware gangs are actively exploiting CVE-2022-26134 remote code execution (RCE) flaw in Atlassian Confluence Server and Data Center. Multiple ransomware groups are actively exploiting the recently disclosed remote code execution (RCE) vulnerability, tracked as CVE-2022-26134, affecting Atlassian Confluence Server and Data Center. Proof-of-concept exploits for the CVE-2022-26134 vulnerability have been released online, Bleeping Computer reported that starting from […]

Atlassian confluence Cerber

Ransomware gangs are actively exploiting CVE-2022-26134 remote code execution (RCE) flaw in Atlassian Confluence Server and Data Center.

Multiple ransomware groups are actively exploiting the recently disclosed remote code execution (RCE) vulnerability, tracked as CVE-2022-26134, affecting Atlassian Confluence Server and Data Center.

Proof-of-concept exploits for the CVE-2022-26134 vulnerability have been released online, Bleeping Computer reported that starting from Friday afternoon, a proof-of-concept exploit for this issue was publicly shared. Researchers from cybersecurity firm GreyNoise reported that 23 unique IP addresses were observed exploiting the Atlassian vulnerabilities.

A remote attacker could exploit this OGNL injection vulnerability to take over vulnerable servers, then exploit the remote code execution to implant malware, including ransomware.

Researchers from security firm Prodaft first reported that AvosLocker ransomware operators have already started exploiting the Atlassian Confluence bug, BleepingComputer reported.

The researchers noticed the creation of a “confluence campaign” in the control panel of the AvosLocker operation.

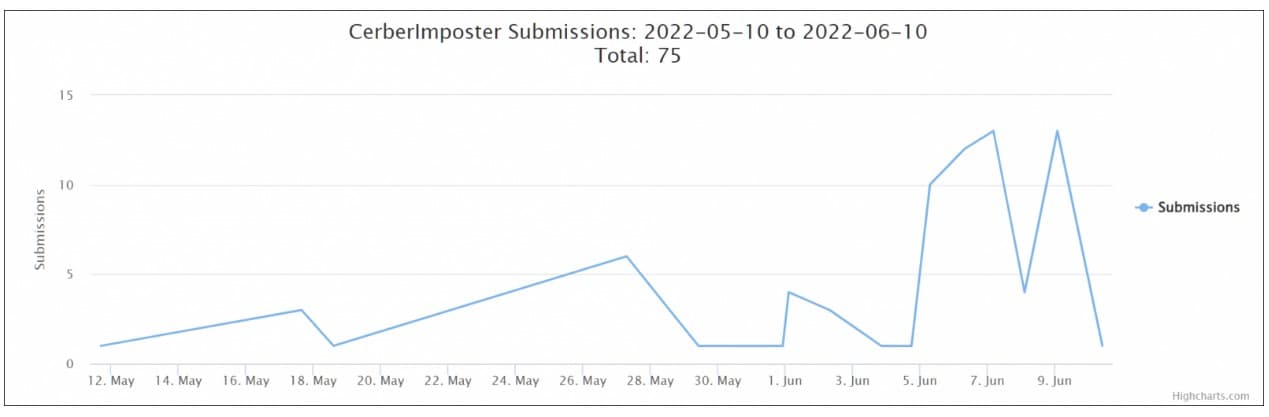
BleepingComputer also reported that operators behind Cerber2021 ransomware (aka CerberImposter) are actively exploiting the Confluence flaw in recent attacks.

Below is data shared by ID-Ransomware creator Michael Gillespie (@demonslay335) with BleepingComputert that shows submissions of CerberImposter including encrypted Confluence configuration files.

Atlassian confluence Cerber

Security Affairs is one of the finalists for the best European Cybersecurity Blogger Awards 2022 – VOTE FOR YOUR WINNERS. I ask you to vote for me again (even if you have already done it), because this vote is for the final.

Please vote for Security Affairs and Pierluigi Paganini in every category that includes them (e.g. sections “The Underdogs – Best Personal (non-commercial) Security Blog” and “The Tech Whizz – Best Technical Blog”)

To nominate, please visit: 

https://docs.google.com/forms/d/e/1FAIpQLSdNDzjvToMSq36YkIHQWwhma90SR0E9rLndflZ3Cu_gVI2Axw/viewform

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Atilassian Confluence)

[adrotate banner=”5″]

[adrotate banner=”13″]


