
According to the security experts at Imperva firm, three open Redis servers out of four are infected with malware.
The discovery is the result of analysis conducted by running Redis-based honeypot servers for some months.
Since their initial report on the RedisWannaMine attack that propagates through open Redis and Windows servers, the experts from Imperva have discovered a new wave of attacks against Redis servers exposed online without authentication.
One of the most common attacks against Redis servers consists of adding SSH keys, so the attacker can remotely access the machine and take it over.
“Having let our honeypot collect data for some time, we noticed that different attackers use the same keys and/ or values to carry out attacks.” states the report published by the experts.
“As such, a shared key or value between multiple servers is a clear sign of a malicious botnet activity.”
The experts used the SSH keys they’ve collected through their honeypot to scan Redis servers that were left exposed online for the presence of these keys.
The experts obtained a list of over 72,000 Redis servers available online by using the shodan query ‘port:6379,’ over 10,000 of these responded to its scan request without an error, allowing researchers to determine locally installed SSH keys.

The discovery was disconcerting, over 75% of these Redis servers were using an SSH key associated with a botnet.
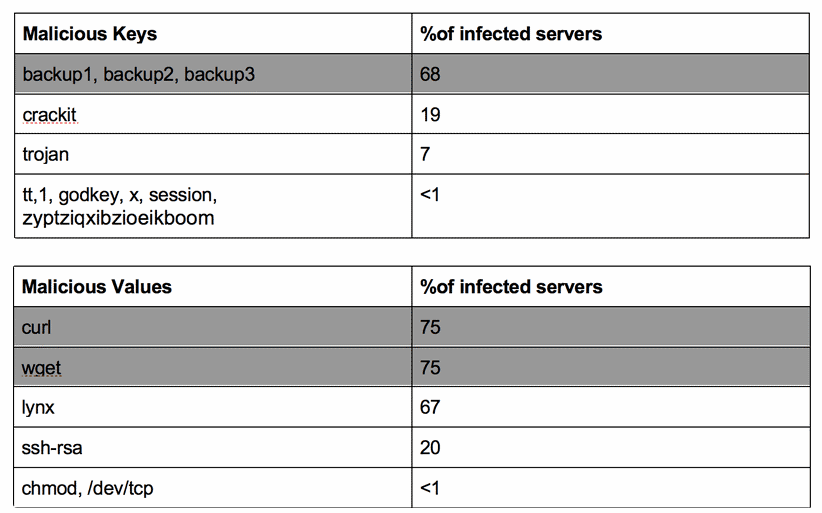
“Unsurprisingly, more than two-thirds of the open Redis servers contain malicious keys and three-quarters of the servers contain malicious values, suggesting that the server is infected.” continues the report.
“Also according to our honeypot data, the infected servers with “backup” keys were attacked from a medium-sized botnet ( ) located at China (86% of IPs).”
Imperva revealed that its customers were attacked more than 75k times, by 295 IPs that run publicly available Redis servers, this means that threat actors are exploiting vulnerable installs to compose their botnet and power a broad range of attacks (SQL injection, cross-site scripting, malicious file uploads, remote code executions, etc).
The “crackit” SSH key in the above table is known to be used at least since 2016 by a known threat actor to spread ransomware and to blackmail the owners of the compromised servers.
The main problem with Redis servers is that owners ignore that Redis doesn’t use a secure configuration by default because they are designed to operate in closed IT networks.
Before some recommendation to the admins operating Redis servers:
- Make sure you follow Redis Security notes, i.e.
- Don’t expose your Redis to the internet
- If possible, apply authentication
- Don’t store sensitive data in clear text
- Monitor your Redis server to make sure it is not infected.
You can monitor processes or CPU consumption to check if a crypto mining malware is running. You can also use the keys and values mentioned in the tables above to monitor the data stored in your Redis server. - Make sure you run Redis with the minimal privileges necessary. Running it with root user, for example, is a bad practice, since it greatly increases the potential damage that an attacker can cause.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – Redis servers, hacking)
[adrotate banner=”5″]
[adrotate banner=”13″]


