
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Hacking

Remote code injection in Microsoft, Yahoo and Orange subdomains

Security researcher Ebrahim Hegazy has identified a remote code injection vulnerability affecting several subdomains of Microsoft, Yahoo, Orange and others. Fortunately, the security Vulnerability has been fixed. While participating in the Yahoo Bug Bounty program, Hegazy has found a “Unauthorized Admin Access” Vulnerability in one of Yahoo domains “mx.horoscopo.yahoo.net.”, that vulnerability led him to find […]

Remote code injection in Microsoft, Yahoo and Orange subdomains

Security researcher Ebrahim Hegazy has identified a remote code injection vulnerability affecting several subdomains of Microsoft, Yahoo, Orange and others. Fortunately, the security Vulnerability has been fixed.

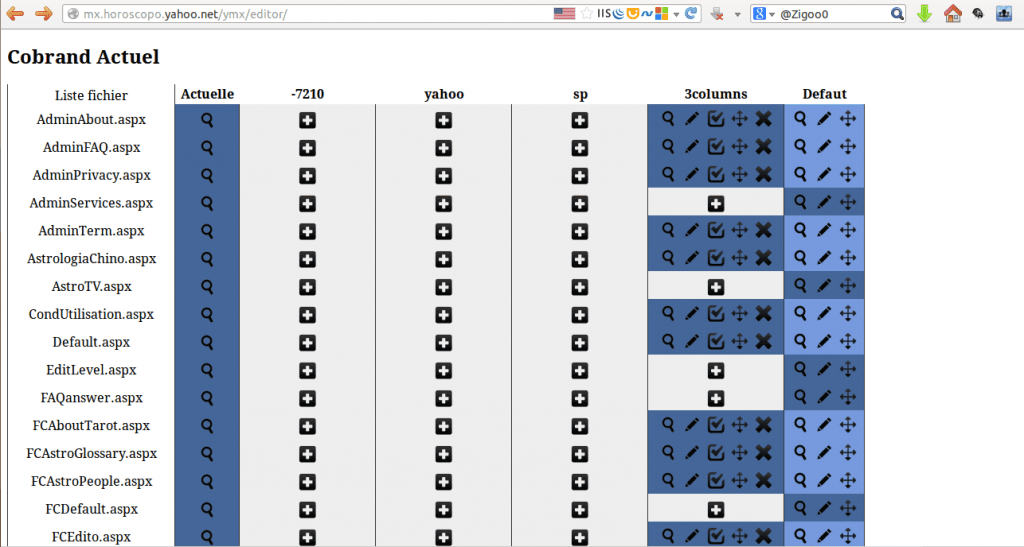
While participating in the Yahoo Bug Bounty program, Hegazy has found a “Unauthorized Admin Access” Vulnerability in one of Yahoo domains “mx.horoscopo.yahoo.net.”, that vulnerability led him to find “Remote Code Injection” Vulnerability where he can create ASPX files on the server, Remote Code Injection Vulnerabilities allow attackers to create files with the ability to run system commands on the vulnerable servers, also to edit the files and read data from Databases hosted on the vulnerable server.

Once he identified the remote code injection vulnerability, he attempted to determine if other Yahoo subdomains were affected. Much to his surprise, he found that also subdomains of Microsoft’s MSN and French telecoms company Orange is Vulnerable to the same Vulnerability.

The affected subdomains were for horoscopes and astrology service and below is the list of the vulnerable domains:
#Yahoo:
http://pe.horoscopo.yahoo.net
http://mx.horoscopo.yahoo.net
http://ar.horoscopo.yahoo.net
http://co.horoscopo.yahoo.net
http://cl.horoscopo.yahoo.net
http://espanol.horoscopo.yahoo.net
#Microsoft MSN:
http://astrocentro.latino.msn.com/
http://astrologia.latino.msn.com/
http://horoscopo.es.msn.com/
http://horoscopos.prodigy.msn.com
#Orange:
http://astrocentro.mujer.orange.es

“The shocking thing here is that I don’t have to upload/create my page on every domain to make a good POC! Because once I created that page on one of the Yahoo domains mentioned above, I found that my page has been created on ALL SITES hosted on the same server, Yahoo, MSN, Orange and others,” Researcher noted.

“Imagine a Black-Hat with this vulnerability, creating his ‘Iframed’ aspx page with its malicious content on such highly ranked/trusted domains of Yahoo.net MSN.com Orange.es and more!!” he adds.

Hegazy posted below video as a Proof Of Concept for the Vulnerability:
He reported the found vulnerability to Microsoft and they fixed the vulnerability without appropriate reward to his report, same thing with Orange, But Yahoo has rewarded the researcher for his report despite that vulnerabilities in Yahoo.net is out of the scope for Yahoo bug bounty Program.

Yahoo remote code injection

For additional technical details on these vulnerabilities, visit Hegazy’s blog post.

Pierluigi Paganini

(Security Affairs –  hacking, remote code injection)


