
The rensenWare ransomware rather than demanding money, it requires the victims to score “over 0.2 billion” playing “TH12 game.
Security experts at MalwareHunterTeam have spotted a new ransomware dubbed ‘rensenWare’. The ransomware is very strange, rather than demanding money, it requires the victims to score “over 0.2 billion” playing “TH12 — Undefined Fantastic Object”.
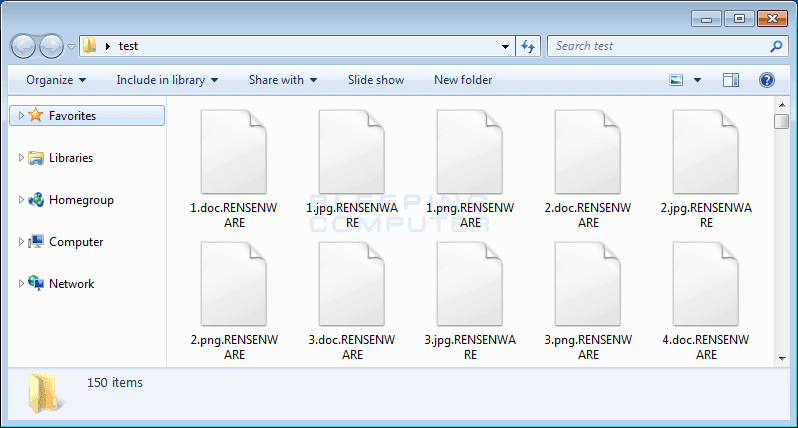
The RensenWare ransomware would scan a machine for certain file types and used the AES-256 to encrypt the files. When the malware encrypts a file it would append the .RENSENWARE extension to it.

When RensenWare ransomware completes the file encrytion, it displays a ransom note featuring Captain Minamitsu Murasa from the Touhou Project series of shooting games made by Team Shanghai Alice.
The ransomware note tells the victims that they must score over .2 billion in the Lunatic level of a Touhou Project game called TH12 ~ Undefined Fantastic Object. If the victim does not reach that score or close the ransomware, he will not able to rescue the files forever.
“That’s easy. You just play TH12 ~ Undefined Fantastic Object and score over 0.2 billion in LUNATIC level. this application will detect TH12 process and score automatically. DO NOT TRY CHEATING OR TEMRMINATE THIS APPLICATION IF YOU DON’T WANT TO BLOW UP THE ENCRYPTION KEY!” reads the ransom note.
Found a surprising ransomware today: "rensenWare".
Not asks for any money, but to play a game until you reach a score – and it's not a joke. pic.twitter.com/Pu53WZFALA— MalwareHunterTeam (@malwrhunterteam) April 6, 2017
“A new ransomware called RensenWare was discovered today by MalwareHunterTeam that makes a unique ransom demand; score over 0.2 billion in the LUNATIC level of TH12 ~ Undefined Fantastic Object or kiss your files goodbye!” wrote Lawrence Abrams from BleepingComputers. “While I do not think this ransomware was ever meant to be distributed, it shows what a creative developer can do to torment their victims.”
The RensenWare ransomware will monitor the gaming progress of the victim by looking for a process called “th12.” The malware reads the processes memory to determine the current score and level of the game. When the victim reaches the Lunatic level and has scored over .2 billion points, the ransomware will save the key to the Desktop and initiate the decryption process.
Lawrence Abrams excludes that the rensenWare ransomware was developed for criminal purposes, “this program was most likely created as a joke. Regardless of the reasons, it illustrates another new and innovative way that a ransomware can be developed.”
During the encryption operation, the malware doesn’t try to delete shadow volumes or make any other action to prevent a victim from restoring their files. This suggests the ransomware was created as a joke or to only disturb a specific group of people.
The author of the ransomware Tvple Eraser explained its intent with a message shared on Twitter:
https://twitter.com/0x00000Ff/status/850332408847024128
The rensenWare ransomware demonstrates the great creativity of the community of malware coders, the experts have no doubt, we will see many other ‘creative’ themes the future.
This malware doesn’t represent a threat, but it has the potential to become it.
[adrotate banner=”9″]
(Security Affairs – RensenWare, ransomware)


