
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

REvil ransomware operators are recruiting new affiliates

REvil Ransomware (Sodinokibi) operators deposited $1 million in Bitcoins on a Russian-speaking hacker forum to demonstrate their willingness to involve new affiliates. The REvil Ransomware (Sodinokibi) operators have deposited $1 million in bitcoins on a Russian-speaking hacker forum to prove to potential affiliates that they mean business. Some hacker forum allows members to deposit funds that can […]

Revil ransomware

REvil Ransomware (Sodinokibi) operators deposited $1 million in Bitcoins on a Russian-speaking hacker forum to demonstrate their willingness to involve new affiliates.

The REvil Ransomware (Sodinokibi) operators have deposited $1 million in bitcoins on a Russian-speaking hacker forum to prove to potential affiliates that they mean business.

Some hacker forum allows members to deposit funds that can be used to buy any kind of illicit services or product offered by other members.

Affiliates are essential to spread malicious code through hacking operations against businesses.

Usually, an affiliate gets 70-80% of the ransom payments they generate.

The REvil RaaS is a private operation, which means that potential affiliates are vetted and interviewed before they are allowed to join the program.

The selection of affiliates is a crucial process in the success of the cybercrime scheme, for this reason, REvil operators personally select each people they want to include in their program.

Now REvil ransomware operators have published a post on a cybercrime forum to recruiting new affiliates, preferably hackers with penetration testing capabilities.

As part of this recruitment process, REvil is looking for teams of skilled hackers at penetration testing or experienced individuals.

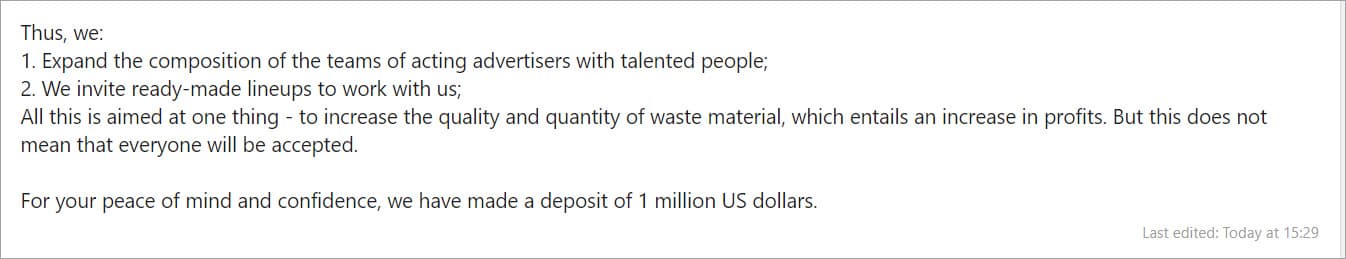
To attract the attention of the potential hackers to recruit as affiliates, the gang has deposited approximately $1 million (99 Bitcoins), on the hacker forum. Below an excerpt from the post published by REVil ransomware operators and shared by BleepingComputer:

Revil ransomware
Source BleepingComputer

The deposit demonstrates that the ransomware operators have a profitable business and trust the hacker forum and don’t fear an exit scam of its administrators

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, REvil ransomware)

[adrotate banner=”5″]

[adrotate banner=”13″]


