
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Revil ransomware operators are targeting new victims

Recently we observed that part of the REvil ransomware infrastructure was up and running again, now we can confirm that they hit new victims. On September 7, the servers of the REvil ransomware gang were back online after around two months since their shutdown. The circumstance was immediately noted by many researchers, me too. The […]

Revil ransomware leak site

Recently we observed that part of the REvil ransomware infrastructure was up and running again, now we can confirm that they hit new victims.

On September 7, the servers of the REvil ransomware gang were back online after around two months since their shutdown. The circumstance was immediately noted by many researchers, me too. The dark web leak site of the ransomware gang, also known as the Happy Blog, is back online, while the site decoder[.]re is still offline at the time of this writing.

It was not clear if the REvil gang resumed its operations or if the servers were turned on by law enforcement.

Now we can confirm that the REvil ransomware gang has fully resumed its operations, the group is targeting news victims and leaking stolen files.

On July 2, the REvil ransomware gang hit the Kaseya cloud-based MSP platform impacting MSPs and their customers.

The REvil ransomware operators initially compromised the Kaseya VSA’s infrastructure, then pushed out malicious updates for VSA on-premise servers to deploy ransomware on enterprise networks.

The group asked $70 million worth of Bitcoin for decrypting all systems impacted in the Kaseya supply-chain ransomware attack.

The attack caught the attention of the media and the police authorities that increased pressure on the group.

Starting from July 13, the infrastructure and the websites used by the REvil ransomware gang were mysteriously unreachable. The Tor leak site, the payment website “decoder[.]re”, and their backend infrastructure went offline simultaneously.

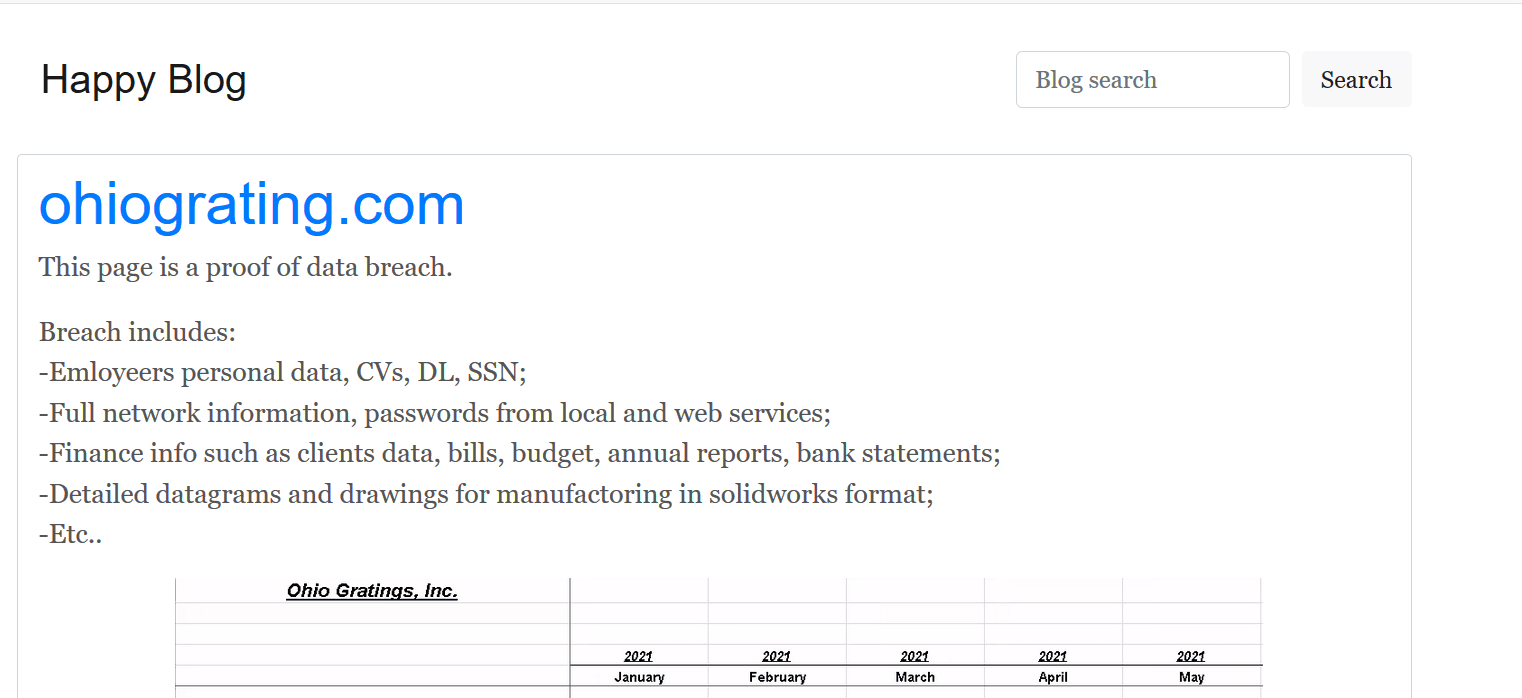
According to Bleeping Computer, on September 9th, someone uploaded a new REvil ransomware sample compiled on September 4th to VirusTotal. This is clearly a proof that the gang resumed their operations, the group also added Ohio Gratings inc to the list of the victims on their leak site.

Revil leak site

BleepingComputer also noticed that after the return of the group, a new public representative named ‘REvil’ had begun posting at cybercrime forums. REvil representative said that the gang temporarily shut down its operations after they previors representative of the gang, Unknown, was likely arrested and servers were compromised.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, ransomware)

[adrotate banner=”5″]

[adrotate banner=”13″]


