
The REvil ransomware gang made the headlines again, the group hit the US nuclear weapons contractor Sol Oriens and stole the victim’s data.
US nuclear weapons contractor Sol Oriens was hit by a cyberattack carried out by the REvil ransomware operators, which claims to have stolen data.
Sol Orien provides consultant services to the National Nuclear Security Administration (NNSA), it confirmed to have suffered a cyber attack via Twitter.
Last week, the REvil ransomware operation added the company to its leak site claiming to have stolen business data and employees’ data, including social security numbers. The ransomware gang threatened to leak relevant documentation and data belonging to military agencies.
“Sol Oriens, LLC did not take all necessary action to protect personal data of their employees and software developments for partner companies. We hereby keep a right to forward all of the relevant documentation and data to military angencies of our choise, includig all personal data of employees.” reads the statement published by REvil on its leak site.
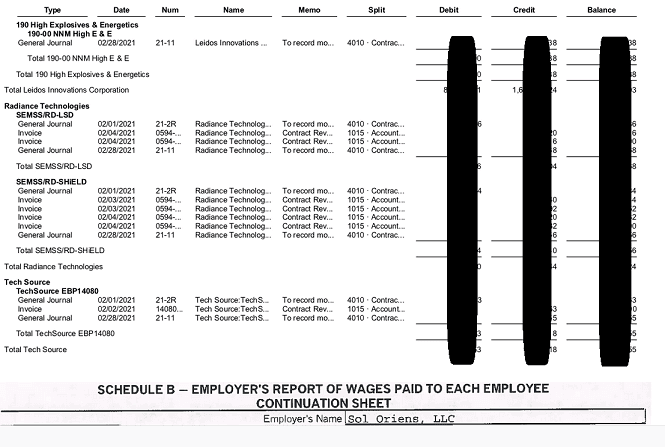
REvil also shared images of the employer’s report and payroll documents.

The company is investigating the incident and determined that threat actors have stolen certain documents from its systems.
“The investigation is ongoing, but we recently determined that an unauthorized individual acquired certain documents from our systems.” states the company. “Those documents are currently under review, and we are working with a third-party technological forensic firm to determine the scope of potential data that may have been involved.”
The company added that it is not aware that threat actors have stolen classified or critical security-related information belonging to its clients.
“We have no current indication that this incident involves client classified or critical security-related information. Once the investigation concludes, we are committed to notifying individuals and entities whose information is involved.” continues the company.
Recently the beef producer JBS has admitted to have paid an $11 million ransom to the REvil ransomware gang after the group initially demanded $22.5 million.
REvil is a group operating out of Russia, the activity of the ransomware gangs was also discussed during the last G7 meeting.
G7 member states have called on Russia and other states to dismantle operations of ransomware gangs operating within their countries.
The call to action follows the large number of ransomware attacks that targeted organizations in the US and Europe, such as the Colonial Pipeline and JBS attacks.
The G7 statement defines the practice of extortion through ransomware attacks as an “escalating shared threat”.
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Sol Oriens)
[adrotate banner=”5″]
[adrotate banner=”13″]


