
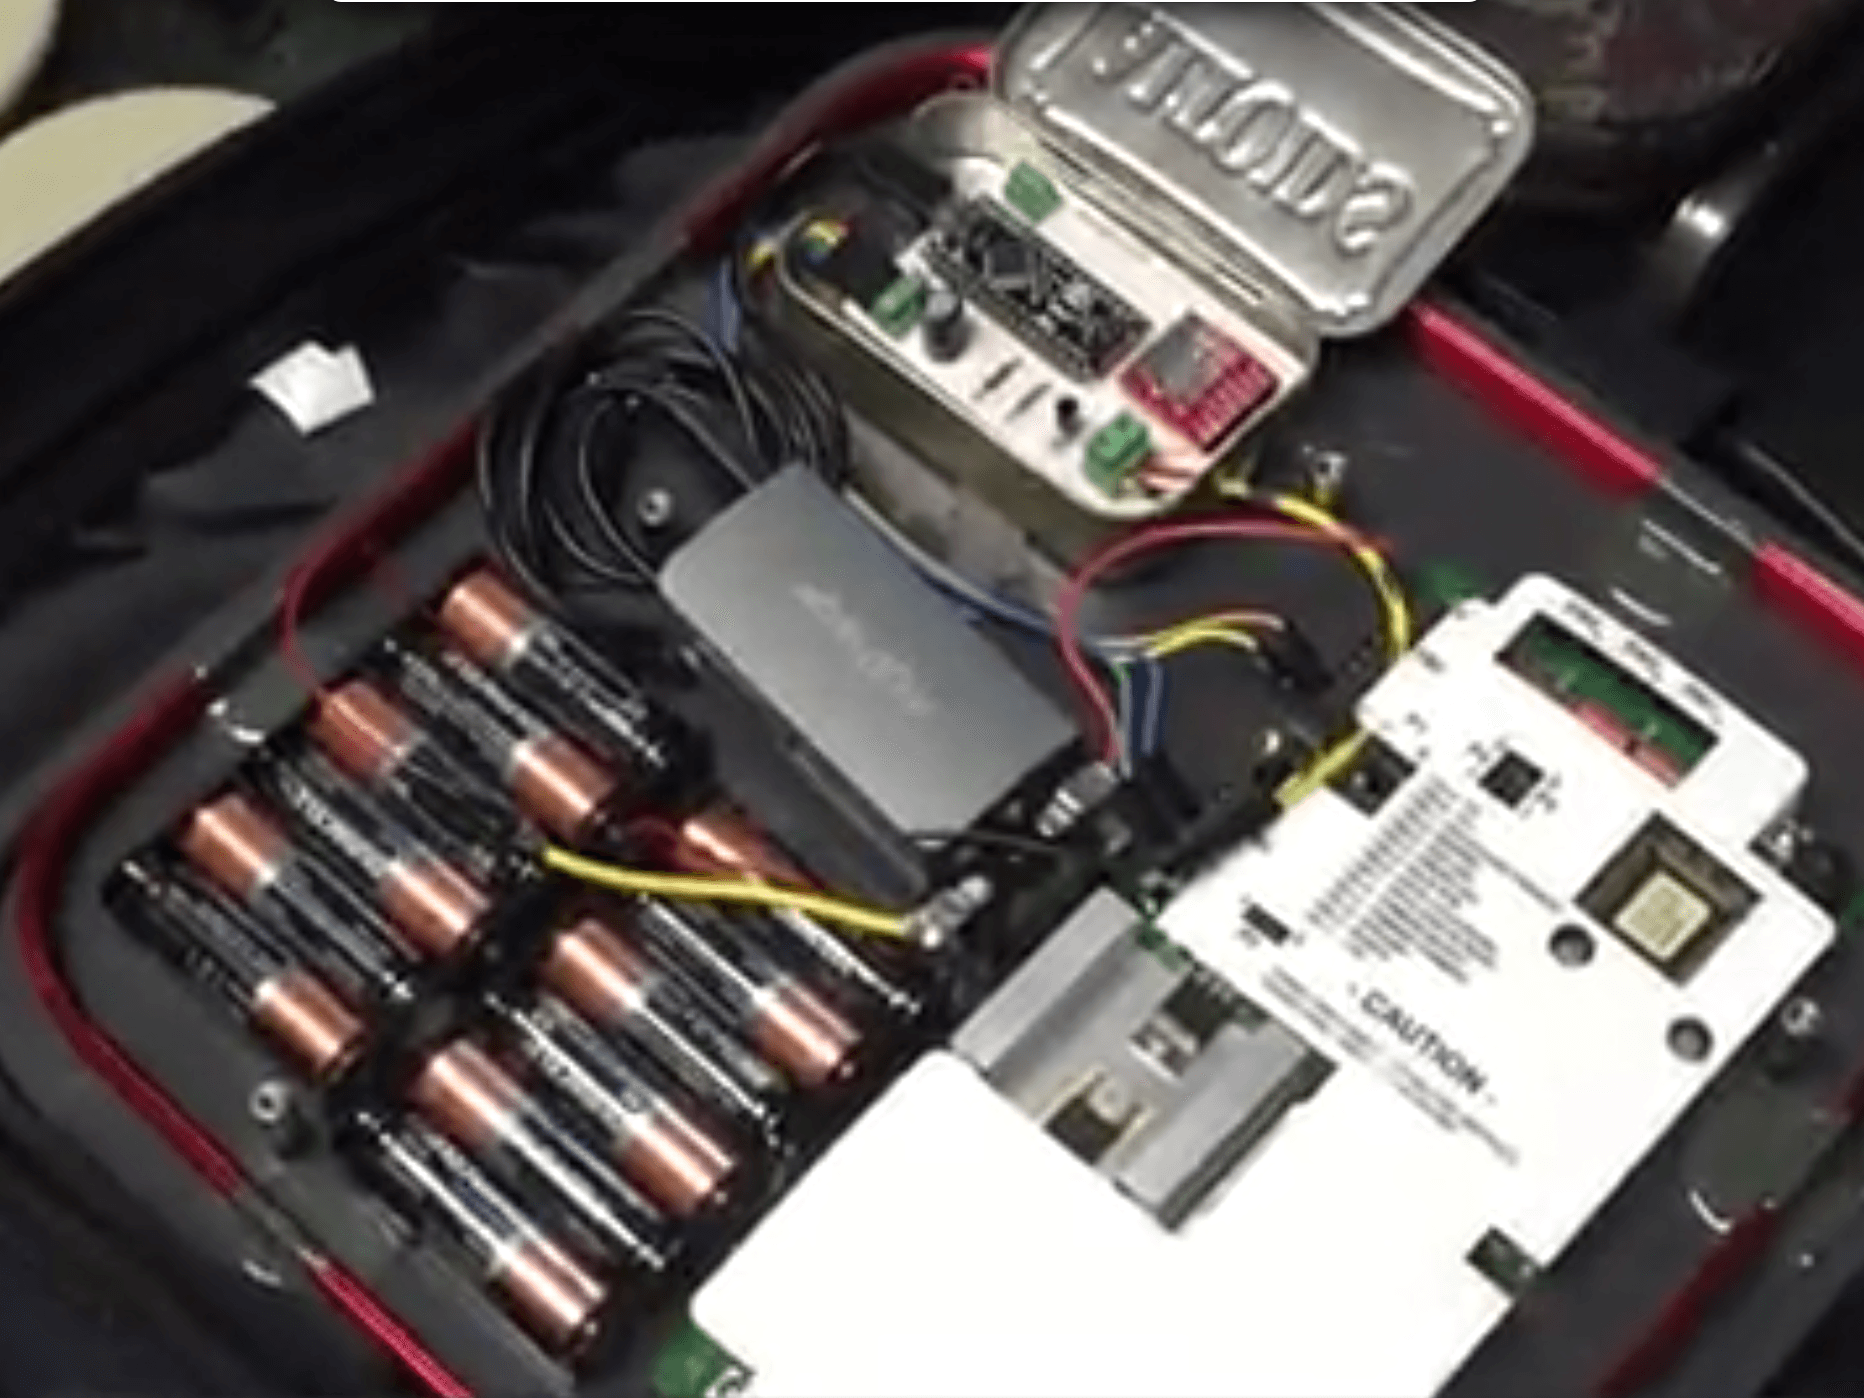
Hackers demonstrated to the Tech Insider how to break into any office by purchasing from Amazon and eBay $700 worth of electronic parts to clone access cards.
Breaking into a company could be very easy and cheap for hackers, it could be sufficient to buy from Amazon and eBay $700 worth of parts.
“We watched a team of hackers ‘fully compromise’ a power company in less than 24 hours” reads the Tech Insider.
“Standing outside the main office of a power company in the Midwest, a hacker known as metrofader pulls an employee’s electronic badge out of his pocket and waves it at an outside sensor. The door unlocks, even though it’s a fake card made with data stolen earlier that day.“
According to the researchers from RedTeam Security, hackers could purchase a $350 device available on both from Amazon or eBay to bypass access control systems based on employee ID badges by manufacturing counterfeit access cards.
The experts explained to journalists at Tech Insider that it is very easy to clone an access card belonging to any employee without stealing employee personal information.

Tastic RFID Thief – Source Tech Insider ()
Matt Grandy from the RedTeam firm explained that they used a particular device that costs just $350 while visiting a target company.
“[We] got the big, long range reader from Amazon,” RedTeam Security consultant Matt Grandy said. “They’re also all over on eBay.” “They’re also all over on eBay.”
A hacker from the firm pretended to visit a company by posing as a student who requested a tour, he carried the device in a laptop bag that. The device is able to intercept the unencrypted communication between an employee access card and the access control systems used to open/close the doors.
The RFID badge reader offered for sale on Amazon and eBay is able to capture access card data up to three feet away and writes it on a microSD card.
The attacker just needs to be in the proximity of a known employee while he is using his RFID badge.
The attacker can then write the access data captured by the device on a fake employee badge, the operation is very simple by using a second device dubbed Proxmark that cost $300.
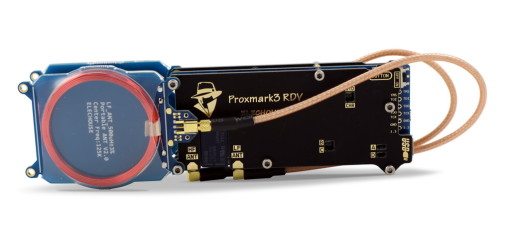
The fake badge could be used to access the target company.
“RedTeam exploited a well-known issue with RFID, or radio-frequency identification, which is a common method many organizations use to give employees access to facilities. Employees typically hold up their RFID-coded badges to an electronic reader outside a door, which then tells the door, “Hey, let this person in.“” states the Tech Insider. “The problem is that much of the time, that data is sent in the clear without encryption, giving hackers an opportunity to snatch the data right off an employee’s card so they can clone it for their own purposes.”
Of course, in order to improve the physical security, it is possible to encrypt data, another good measure to adopt to protect access cards are the RFID-blocking sleeves.
Let me suggest to give a look to the Tastic RFID Thief tool:
- Project Page:
- Previous article about it:
[adrotate banner=”9″]
(Security Affairs – RDIF, hacking)


