
The American drugstore chain Rite Aid Corporation disclosed a data breach following the cyber attack that hit the company in June.
The American drugstore chain giant Rite Aid suffered a data breach following a cyberattack in June conducted by the RansomHub ransomware group. The group is the third-largest drugstore chain in the United States, with over 2,000 stores, and ranked No. 148 in the Fortune 500 in 2022.
The company launched an investigation into the security breach with the help of external experts and will notify the impacted customers, BleepingComputer first reported.
“Rite Aid experienced a limited cybersecurity incident in June, and we are finalizing our investigation. We take our obligation to safeguard personal information very seriously, and this incident has been a top priority,” reads the statement issued by Rite Aid. “Together with our third-party cybersecurity partner experts, we have restored our systems and are fully operational. We are sending notices to impacted consumers.” “We take our obligation to safeguard personal information very seriously, and this incident has been a top priority. We appreciate your patience until we can provide additional information” the company added.
The company pointed out that the incident doesn’t impact social security numbers, health or financial information.
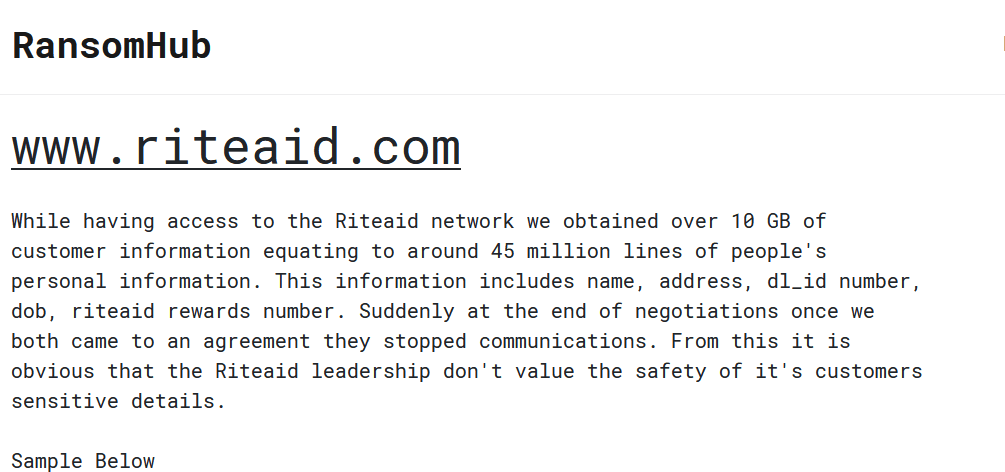
The RansomHub group claimed responsibility for the data breach and announced the theft of 10 GB of customer information, around 45 million records of people’s personal information.
“While having access to the Riteaid network we obtained over 10 GB of customer information equating to around 45 million lines of people’s personal information. This information includes name, address, dl_id number, dob, riteaid rewards number. Suddenly at the end of negotiations once we both came to an agreement they stopped communications. From this it is obvious that the Riteaid leadership don’t value the safety of it’s customers sensitive details.” reads the announcement published by RansomHub group on its Tor Leak site.

The group also published some images of the allegedly stolen data as proof of the hack, it also threatened to leak the alleged stolen data by July 22 if the company will not pay the ransom.
On May 2023, Rite Aid suffered another cyberattack, it was one of the hundreds of organizations that were breached in the MOVEit hacking campaign by the Cl0p ransomware gang.
Rite Aid later confirmed that the threat actors had access to more than 24,000 of its customers’ personally identifiable information, including names, addresses, birth dates, limited insurance, and prescription information.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, ransomware)


