
The phishing-as-a-service (PhaaS) platform Robin Banks migrated its infrastructure to DDoS-Guard, a Russian bulletproof hosting service.
The phishing-as-a-service (PhaaS) platform Robin Banks was originally hosted by Cloudflare provider, but the company in July disassociated Robin Banks phishing infrastructure from its services after being informed.
The move caused a multi-day disruption to PhaaS operations, then the administrators of the platform made several changes, including migration of the infrastructure to the notorious Russian bulletproof hosting provider.
According to the popular investigator Brian Krebs, DDOS-GUARD also hosted content for conspiracy theory movements QAnon and 8chan, as well as the official site for the Hamas terrorist group. The provider never complies with takedown requests issued by law enforcement agencies.
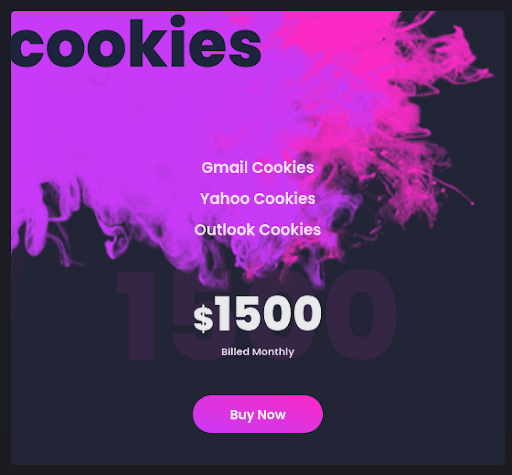
Experts from cybersecurity company IronNet pointed out that operators behind the Robin Banks also added a new cookie-stealing feature that can be purchased by their customers as an add-on to the phishing kit. This feature allows crooks to order this feature to bypass multi-factor authentication (MFA) in their campaigns.
This feature is offered for $1,500 per month, while Robin Bank’s full access is offered for $200 per month.

The Robin Banks was first analyzed July 2022, it relies heavily on open-source code and off-the-shelf tooling.
“In addition to migrating its infrastructure to DDOS-GUARD, Robin Banks also started enforcing increased security on the platform, most likely out of fear someone might hack their admin interface. This included implementing and requiring two-factor authentication (2FA) in order for kit customers to view phished information via the main GUI.” reads a report published by security firm IronNet. “However, if they did not want to implement 2FA, the customers could instead opt to have the phished information sent to a Telegram bot rather than access it through the Robin Banks GUI.”
The experts observed three common phishlets that are included in the distribution, Google, Yahoo and Outlook. Phishlets are the configuration files for proxying a legitimate website into a phishing site and are essentially used by the evilginx2 phishing kit.
Robin Banks customers can view the stolen data via the service by enabling the two-factor authentication (2FA), or through a Telegram bot.
“In addition to migrating its infrastructure to DDOS-GUARD, Robin Banks also started enforcing increased security on the platform, most likely out of fear someone might hack their admin interface. This included implementing and requiring two-factor authentication (2FA) in order for kit customers to view phished information via the main GUI.” continues the post. “However, if they did not want to implement 2FA, the customers could instead opt to have the phished information sent to a Telegram bot rather than access it through the Robin Banks GUI.”
Once the researchers have deobfuscated the core of the phishing kit the experts discovered that it it borrows code from a third-party ad fraud detection service named Adspect.
Adspect allows to detect and filter unwanted visitors in web traffic through blacklisting, fingerprinting, and machine learning techniques.
Adspect allows to ensure targets of phishing campaigns are redirected to malicious sites, while scanners and unwanted traffic are redirected to benign websites to avoid detection.
“Robin Banks’ heavy reliance on open-source code and off-the-shelf tooling showcases just how low the barrier-to-entry is to not only conducting phishing attacks, but also to becoming a service provider and creating a PhaaS platform for others to use. It does not take a high sophistication level to create a kit such as this and charge hundreds to thousands of dollars for others to use it.” concludes the post. “Thus, the growing use of different web tools to host cybercriminal platforms poses concerns as cybercrime becomes more accessible and a low-effort option to drawing in a quick profit.”
Recently other new PhaaS services made the headlines, including Caffeine, EvilProxy, and Frappo, attracting a growing number of malicious actors in the threat landscape.
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Robin Banks)
[adrotate banner=”5″]
[adrotate banner=”13″]


