
Security Affairs
CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Rockwell Automation Allen-Bradley Stratix and ArmorStratix switches are exposed to hack due to Cisco IOS flaws

Rockwell Automation is warning that its Allen-Bradley Stratix and ArmorStratix industrial switches are exposed to hack due to security vulnerabilities in Cisco IOS. According to Rockwell Automation, eight flaws recently discovered recently in Cisco IOS are affecting its products which are used in many sectors, including the critical manufacturing and energy. The list of flaws includes […]

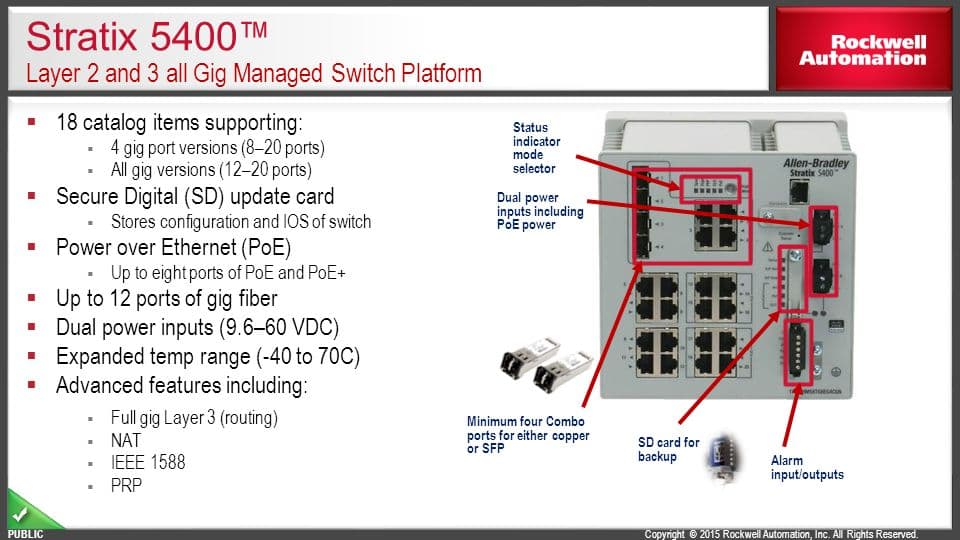
Rockwell Automation Stratix 5400

Rockwell Automation is warning that its Allen-Bradley Stratix and ArmorStratix industrial switches are exposed to hack due to security vulnerabilities in Cisco IOS.

According to Rockwell Automation, eight flaws recently discovered recently in Cisco IOS are affecting its products which are used in many sectors, including the critical manufacturing and energy.

The list of flaws includes improper input validation, resource management errors, 7PK errors, improper restriction of operations within the bounds of a memory buffer, use of externally-controlled format string.

“Successful exploitation of these vulnerabilities could result in loss of availability, confidentiality, and/or integrity caused by memory exhaustion, module restart, information corruption, and/or information exposure.” reads the security advisory published by the US ICS-CERT.

Affected models are Stratix 5400, 5410, 5700, 8000 and ArmorStratix 5700 switches running firmware version 15.2(6)E0a and earlier.

Rockwell Automation Stratix 5400

The most critical vulnerability is the Cisco CVE-2018-0171 Smart Install, a flaw that affects the Smart Install feature of Cisco IOS Software and Cisco IOS XE Software that could be exploited by an unauthenticated, remote attacker to cause a reload of a vulnerable device or to execute arbitrary code on an affected device.

A couple of weeks ago, the hacking crew “JHT” launched a hacking campaign exploiting Cisco CVE-2018-0171 flaw against network infrastructure in Russia and Iran.

Rockwell has released firmware version 15.2(6)E1 to address the vulnerabilities in its switches.

Rockwell Automation provided mitigations in addition to upgrading the software version:

Cisco has released new Snort Rules at https://www.cisco.com/web/software/286271056/117258/sf-rules-2018-03-29-new.html(link is external) to help address the following vulnerabilities:

  • CVE-2018-0171 – Snort Rule 46096 and 46097
  • CVE-2018-0156 – Snort Rule 41725
  • CVE-2018-0174 – Snort Rule 46120
  • CVE-2018-0172 – Snort Rule 46104
  • CVE-2018-0173 – Snort Rule 46119
  • CVE-2018-0158 – Snort Rule 46110
[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – Rockwell Automation, Cisco IOS law)

[adrotate banner=”5″]

[adrotate banner=”13″]


