
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Russian cybercriminal Roman Seleznev gets another prison sentence

Seleznev gets another prison sentence. He received 14-year prison sentence for charge in Nevada and another 14 years for the second charge in Georgia. In April, the Russian hacker Roman Seleznev, aka Track2, Bulba and Ncux, was sentenced to 27 years in prison, he was convicted of causing $170 million in damage by hacking into point-of-sale systems. The 33-year-old was […]

diplomatic prisoner exchange Russian cybercriminals

Seleznev gets another prison sentence. He received 14-year prison sentence for charge in Nevada and another 14 years for the second charge in Georgia.

In April, the Russian hacker Roman Seleznev, aka Track2, Bulba and Ncux, was sentenced to 27 years in prison, he was convicted of causing $170 million in damage by hacking into point-of-sale systems.

The 33-year-old was previously sentenced by a U.S. court to 27 years in prison for 38 counts of wire fraud, hacking, identity theft, and payment card fraud.

Seleznev was pleading guilty to racketeering and conspiracy to commit bank fraud charges on September 7, now he received further 14-year prison sentence for the first charge in Nevada and another 14 years for the second charge in Georgia.

Seleznev must pay roughly $51 million in the Nevada case and more than $2.1 million in the Georgia case.

The overall sentence is added to the previous 27-year sentence.

Seleznev was one of the members of the criminal ring known as Carder.su focused on identity theft and credit card fraud. The hackers advertised his website on Carder.su offering stolen payment card data.

According to the US prosecutors, activities conducted by members of Carder.su caused $50,893,166.35 losses, roughly the same amount that Seleznev has been ordered to pay.

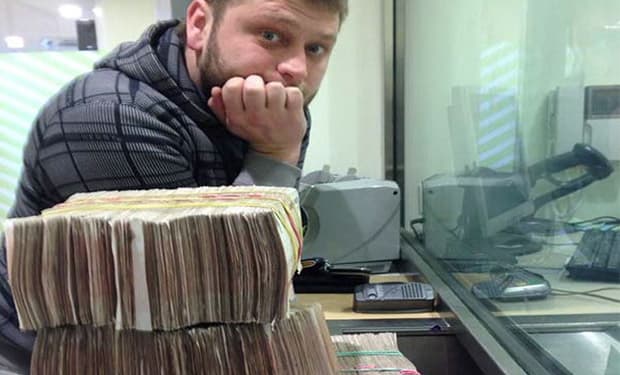
Roman Seleznev

Authorities conducted a massive operation against members of the Carder.su community, they charged 55 individuals and 33 of them have already been convicted.

Seleznev admitted being a “casher” in the Georgia case, he withdrew cash using stolen bank account information. He was involved in a fraudulent activity against an Atlanta-based firm that processed credit and debit card transactions for financial institutions.

Crooks stole more than 45 million payment cards from the financial firm, then they used them to withdraw over $9.4 million from 2,100 ATMs in 280 cities worldwide in less than 12 hours.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – carding, cybercrime)

[adrotate banner=”5″]

[adrotate banner=”13″]


