
A new campaign spreading RomCom RAT impersonates popular software brands like KeePass, and SolarWinds.
The threat actor behind the RomCom RAT (remote access trojan) has refreshed its attack vector and is now abusing well-known software brands for distribution.
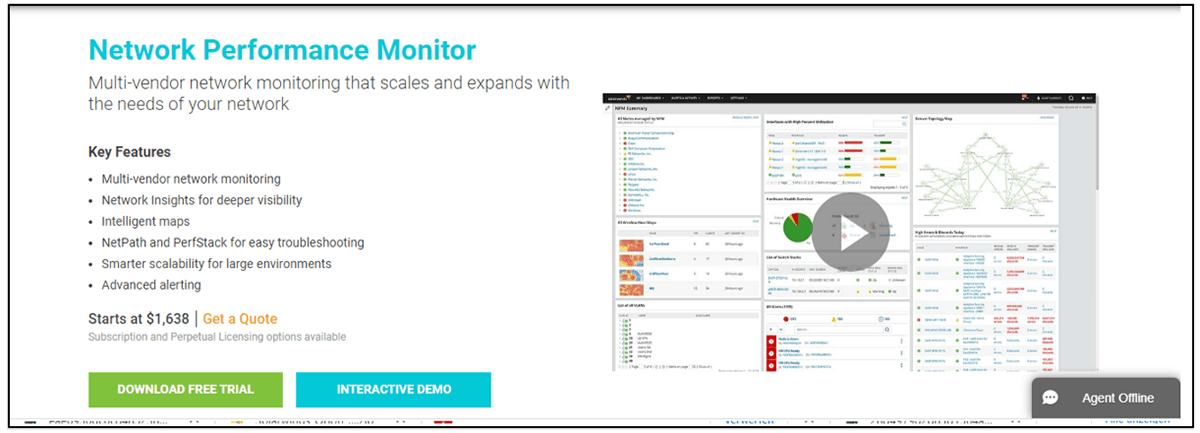
Researchers from BlackBerry uncovered a new RomCom RAT campaign impersonating popular software brands like KeePass, and SolarWinds. The threat actors set up websites cloning the official download websites for SolarWinds Network Performance Monitor (NPM), KeePass password manager, and PDF Reader Pro. The malware was masqueraded as legitimate applications from popular brands.
The attacks were spotted while analyzing network artifacts associated with RomComRAT infections resulting from attacks targeting Ukrainian military institutions.
“In our latest discovery, our team found RomCom leveraging the following products in their campaigns: SolarWinds Network Performance Monitor, KeePass Open-Source Password Manager, and PDF Reader Pro.” reads the report published by BlackBerry.
The analysis of the terms of service (TOS) of two of the malicious websites and the SSL certificates of a newly created command-and-control (C2) revealed that The attacks continue to target Ukraine along with English-speaking countries, including the United Kingdom.
The geography of the targets and the current geopolitical situation suggests the attacks were carried out by a nation-state actor.
The RomCom threat actor deployed clone websites on malicious domain similar to the legitimate one that they registered. Then they trojanizing a legitimate application and distributed it through the decoy website, deploying targeted phishing emails to the victims. In some cases, the attackers used additional infector vectors.

Attackers included into the tainted app a malicious DLL used to downloads and execute an instance of the RomCom RAT from the “C:\Users\user\AppData\Local\Temp\winver.dll” location.
The executable downloaded as part of the SolarWinds Network Performance Monitor campaign, “Solarwinds-Orion-NPM-Eval.exe”, is signed with the same digital certificate used in the attacks against Ukrainian entities.
In the KeePass RomCom campaign threat actors distributed an archive named “KeePass-2.52.zip” containing the RomCom RAT dropper (“hlpr.dat”) and the setup.exe used to execute the dropper.
In another attack abusing the KeePass brand the attackers set up a clone website in the Ukrainian language.
The researchers speculate a link with other extortion groups like Cuba Ransomware and Industrial Spy gangs.
“The RomCom threat actor is actively deploying new campaigns targeting victims in Ukraine and English-speaking targets worldwide. Based on the TOS, it is possible that victims in the United Kingdom are a new target, while Ukraine continues to be the main focus.” concludes the report. “RomCom RAT, Cuba Ransomware, and Industrial Spy have an apparent connection.”
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, RomCom RAT)
[adrotate banner=”5″]
[adrotate banner=”13″]


