
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

APT

Russia-linked RomCom group targeted Ukrainian government agencies since late 2023

Russia-linked threat actor RomCom targeted Ukrainian government agencies and Polish entities in cyber attacks since late 2023. Cisco Talos researchers observed Russia-linked threat actor RomCom (aka UAT-5647, Storm-0978, Tropical Scorpius, UAC-0180, UNC2596) targeting Ukrainian government agencies and Polish entities in a new wave of attacks since at least late 2023.  In the recent attacks, RomCom […]

RomCom

Russia-linked threat actor RomCom targeted Ukrainian government agencies and Polish entities in cyber attacks since late 2023.

Cisco Talos researchers observed Russia-linked threat actor RomCom (aka UAT-5647, Storm-0978, Tropical Scorpius, UAC-0180, UNC2596) targeting Ukrainian government agencies and Polish entities in a new wave of attacks since at least late 2023. 

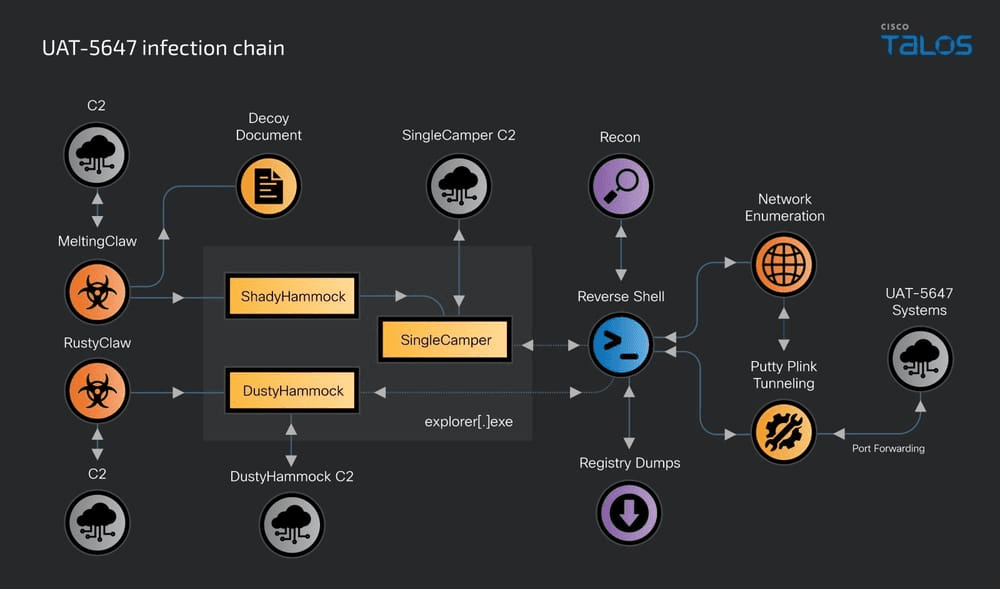
In the recent attacks, RomCom deployed an updated variant of the RomCom RAT dubbed ‘SingleCamper.’ SingleCamper is loaded directly from registry into memory and relies on a loopback address to communicate with its loader. The threat actors also employed two new downloaders, called RustClaw and MeltingClaw, plus two backdoors, DustyHammock (Rust-based) and C++-based ShadyHammock.

In the past, RomCom launched ransomware attacks and cyber espionage campaigns, however, it is ramping up attacks focused on data exfiltration from Ukrainian targets. The group uses multiple tools and malware languages (GoLang, C++, RUST, LUA) to establish long-term access for espionage, possibly followed by ransomware deployment for disruption and profit. Polish entities were likely targeted as well, based on malware language checks.

“The infection chain consists of a spear-phishing message delivering a downloader consisting of either of two variants: “RustyClaw” – a RUST-based downloader, and a C++ based variant we track as “MeltingClaw”.” reads the report published by Talos. “The downloaders make way for and establish persistence for two distinct backdoors we call “DustyHammock” and “ShadyHammock,” respectively.”

DustyHammock operates as the main backdoor for C2 communications, while ShadyHammock loads the SingleCamper malware and can receive commands from other malicious components.

RomCom

Once the initial network reconnaissance is completer, RomCom used PuTTY’s Plink tool to create remote tunnels connecting targeted endpoints with attacker-controlled servers.

SingleCamper malware registers infections by sending system info to C2, executes recon commands, and can download additional tools, exfiltrate files, or manage infections.

The report includes details about RomCom’s arsenal, Talos also shared IOCs for this threat.  

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, RomCom)


