
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Chinese hackers targeted officials visiting the USS Ronald Reagan vessel

Experts from the cyber security firm FireEye discovered a spear phishing campaign launched against visitors to the Ronald Reagan vessel in South China Sea. Chinese hackers targeted foreign government personnel who visited a US aircraft carrier the day before a contentious international court ruling on the South China Sea, According to the FireEye cyber security firm, […]

Chinese hackers targeted officials visiting the USS Ronald Reagan vessel

Experts from the cyber security firm FireEye discovered a spear phishing campaign launched against visitors to the Ronald Reagan vessel in South China Sea.

Chinese hackers targeted foreign government personnel who visited a US aircraft carrier the day before a contentious international court ruling on the South China Sea,

According to the FireEye cyber security firm, Chinese hackers targeted US aircraft carrier. The hackers launched an attack against visitors to a US vessel the day before (July 11, 2016) a contentious international court ruling on the South China Sea.

According to the experts at the FireEye’s iSight unit, the Chinese hackers powered a spear phishing attack that leveraged on messages with a malicious document as an attachment. The document impersonating an official message addressed to officials visiting the USS Ronald Reagan, a nuclear-powered aircraft carrier which conducted patrols of the South China Sea in July.

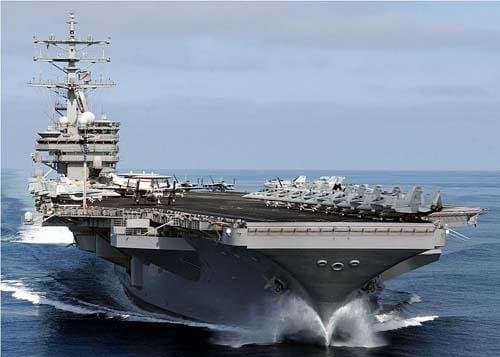
ronald-reagan-vessel

The document appears as an official message that was sent to officials visiting the nuclear-powered aircraft carrier USS Ronald Reagan. The Ronald Reagan aircraft carrier was used by the US Government to patrol the South China Sea in July.

The document allowed the attacker to infect victims with the Enfal malware, which can be used by attackers as a spyware or to download further malicious payloads on the machine.

According to FireEye, the same hackers are responsible for other attacks against US and Vietnamese national defence computer networks.

The Financial Times that reported the discovery made by FireEye, confirmed the absence of direct evidence to link the attack to a Chinese nation-state actor.The researcher discovered that the command and control server used by the attacker was already used in the past by the China-based group.

“Many governments and militaries in Southeast Asia lack cyber security controls that can effectively match these elevated threats,” said Bryce Boland, FirEye’s Asia-Pacific chief technology officer. 

“For example, personal webmail and unmanaged devices aren’t unusual, and many organisations lack the technology to detect unique attacks which haven’t been seen before.” 

At the time I was writing it is still unclear if hackers have compromised classified information, nor that the hackers have interfered with the vessel’s operations in the South China Sea.

“The official said unclassified information about logistics was often shared with contractors and foreign governments to support port visits for ships.” reported the FT.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – Ronald Reagan vessel, cyber espionage)


