
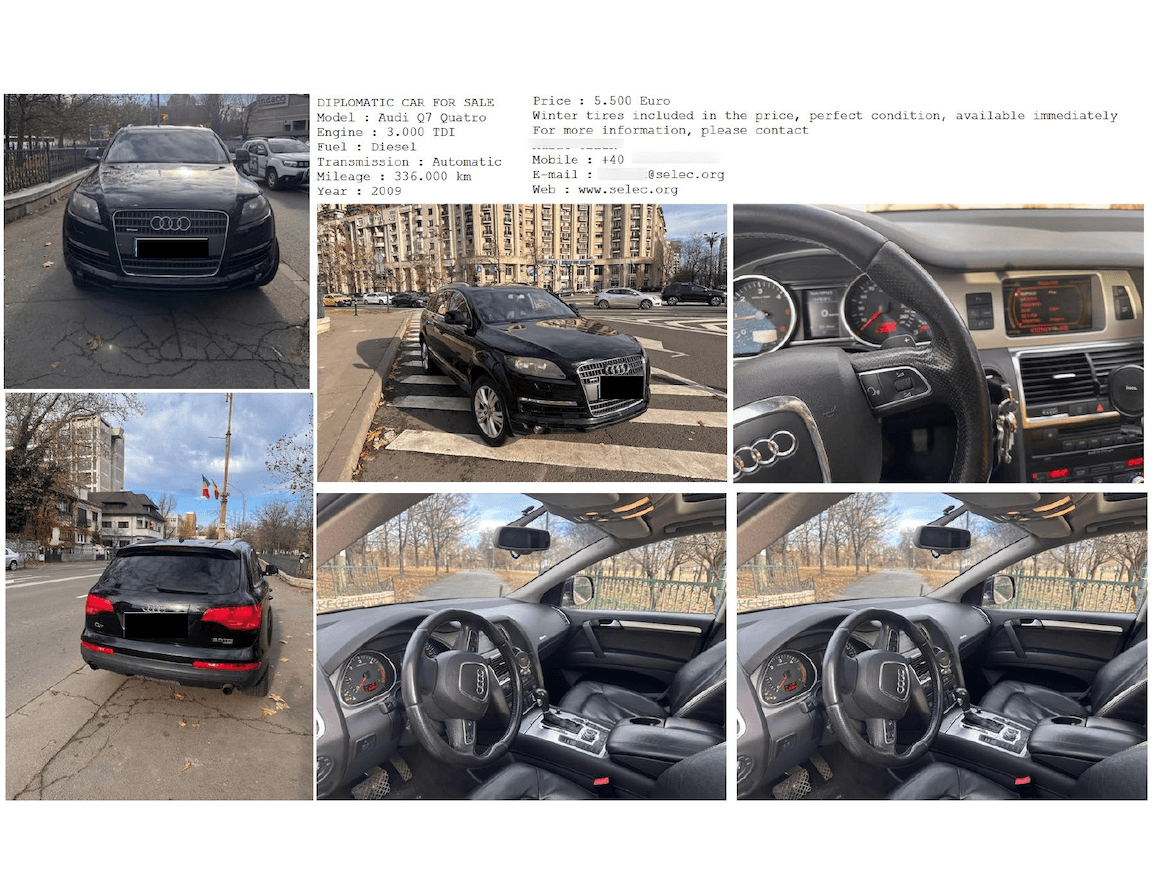
A Russia-linked APT used a car for sale as a phishing lure to deliver a modular Windows backdoor called HeadLace.
Palo Alto researchers reported that a Russia-linked threat actor known as Fighting Ursa (also identified as APT28, Fancy Bear, or Sofacy) used a fake car advertisement to distribute HeadLace backdoor malware, targeting diplomats. The campaign began around March 2024, the attackers leveraged phishing tactics that have been effective against diplomats for years, exploiting themes that prompt targets to engage with malicious content.
The experts attribute the March 2024 campaign to Fighting Ursa with a medium to high level of confidence. The APT group targeted diplomats and relied on public and free services to host various stages of the attack.
Unit 42 pointed out that other threat groups, like Cloaked Ursa, in 2023 used an advertisement for a BMW for sale to target diplomatic missions within Ukraine.
In June 2023, researchers at Insikt Group observed Russian GRU’s unit APT28 targeting networks across Europe with information-stealer Headlace and credential-harvesting web pages. The experts observed the APT deploying Headlace in three distinct phases from April to December 2023, respectively, using phishing, compromised internet services, and living off the land binaries. The credential harvesting pages were designed to target Ukraine’s Ministry of Defence, European transportation infrastructures, and an Azerbaijani think tank. The credential harvesting pages created by the group can defeat two-factor authentication and CAPTCHA challenges by relaying requests between legitimate services and compromised Ubiquiti routers.
The compromise of networks associated with Ukraine’s Ministry of Defence and European railway systems could allow attackers to gather intelligence to influence battlefield tactics and broader military strategies. Additionally, their interest in the Azerbaijan Center for Economic and Social Development indicates a potential agenda to understand and possibly influence regional policies. Insikt Group speculated the operation was aimed at influencing regional and military dynamics.
Earlier this May, the threat actor Fighting Ursa exploited Webhook.site, a legitimate service, to initiate the infection chain by hosting a malicious HTML page. This page, submitted to VirusTotal on March 14, 2024, included scripts to determine if the visitor’s computer was running Windows. Non-Windows users were redirected to a decoy image hosted on ImgBB. The HTML also created a ZIP archive from Base64 text for download, leveraging JavaScript to automate the process. Attackers employed a decoy image, featuring an Audi Q7 Quattro SUV and falsely advertising it as a “Diplomatic Car For Sale,” included fake contact details and aimed to lend credibility to the phishing scheme.

The three contained three files, a copy of the legitimate Windows calculator executable calc.exe that masquerades as an image file (“IMG-387470302099.jpg.exe”), a DLL (“WindowsCodecs.dll”), and a batch file (“zqtxmo.bat”).
The file IMG-387470302099.jpg.exe is used to sideload the DLL file WindowsCodecs.dll, which is a component of the HeadLace backdoor that runs the batch script. In turn the script executes a Base64-encoded command to retrieve a file from another webhook[.]site URL.
“The batch file saves content from this second Webhook.site URL as IMG387470302099.jpg in the user’s downloads directory. It then moves the downloaded file into the %programdata% directory and changes the file extension from .jpg to .cmd.” reads the analysis published by Palo Alto Networks. “Finally, the batch file executes IMG387470302099.cmd, then deletes itself as a way to remove any obvious trace of malicious activity.”
The experts believe that the Fighting Ursa group will continue to use legitimate web services in its attack infrastructure.
“The infrastructure the group uses has constantly changed and evolved, as noted in a recent report from Recorded Future. Other industry reports have also shown various lures this actor uses in attempts to drop HeadLace malware.” concludes the report.
Defenders are recommended to limit access to these or similar hosting services as necessary. Organizations should scrutinize the use of these free services to identify possible attack vectors.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, APT28)


