
Russia-linked TA446 is using the DarkSword iOS exploit kit in targeted phishing campaigns to compromise iPhone users.
Russia-linked APT group TA446 (aka SEABORGIUM, ColdRiver, Callisto, and Star Blizzard) is using the DarkSword exploit kit in targeted spear-phishing campaigns against iOS devices. The attacks rely on malicious emails to compromise iPhones, highlighting a growing threat from advanced state-sponsored actors.
TA446 has been active since at least 2017, its campaigns involve persistent phishing and credential theft campaigns leading to intrusions and data theft. The APT group primarily targets NATO countries, but experts also observed campaigns targeting the Baltics, Nordics, and Eastern Europe regions, including Ukraine.
The group primarily focuses operations on defense and intelligence consulting companies, non-governmental organizations (NGOs) and intergovernmental organizations (IGOs), think tanks, and higher education. The APT also targets former intelligence officials, experts in Russian affairs, and Russian citizens abroad.
SEABORGIUM’s campaigns begin with a reconnaissance activity of target individuals, with a focus on identifying their contacts on social networks or the sphere of influence.
Proofpoint researchers have directly observed a phishing campaign attributed with high confidence to TA446. While the group had not previously targeted iCloud accounts or Apple devices, the use of the leaked DarkSword exploit kit now enables attacks against iOS users. Researchers also note that TA446’s activity does not overlap with UNC6353, confirming it as a distinct threat actor.
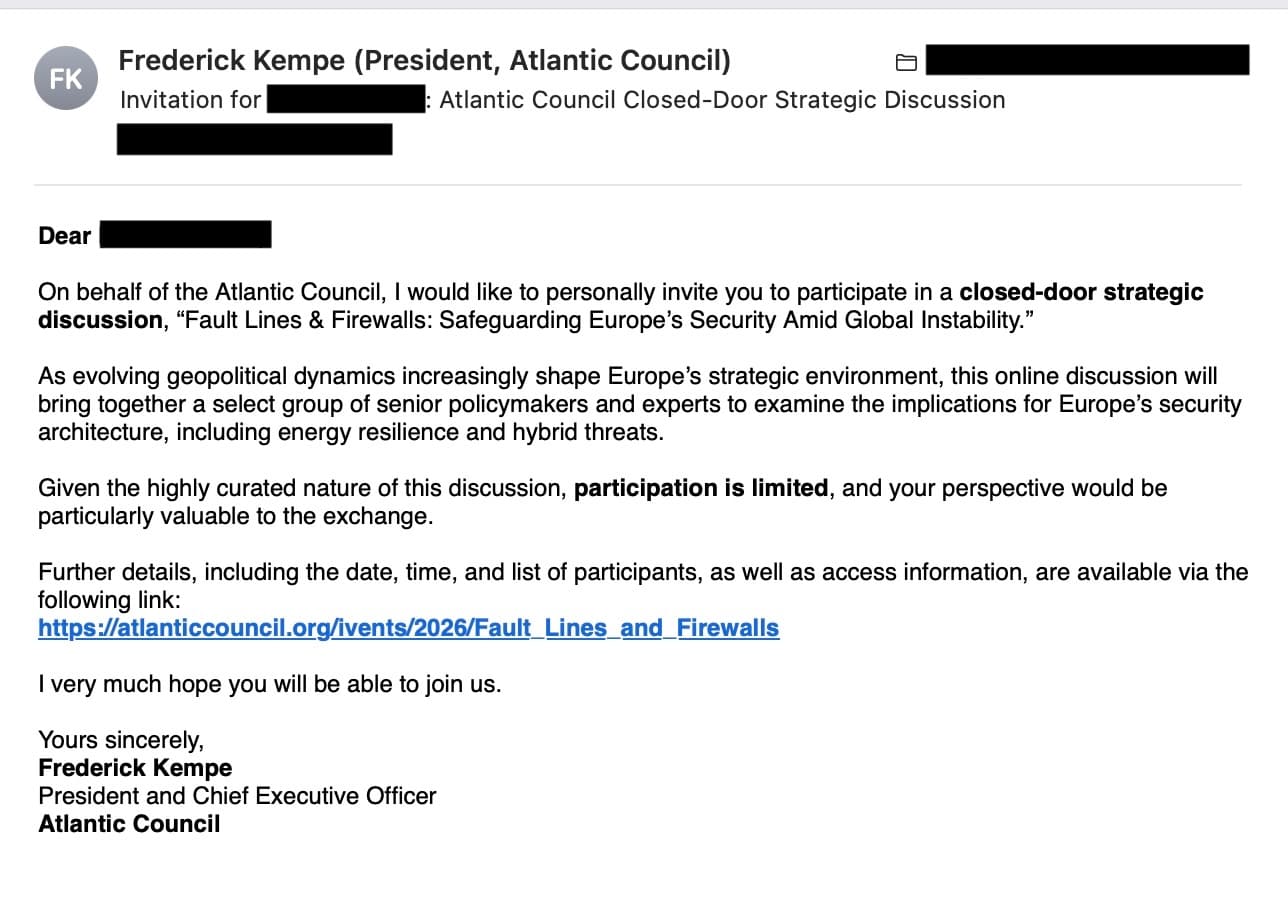
Malfors researchers also observed a targeted campaign delivering DarkSword RCE (GHOSTBLADE) via fake Atlantic Council “discussion invitation” emails.
On March 26, 2026, Proofpoint observed a surge in emails attributed to Russia-linked TA446, spoofing the Atlantic Council. The campaign showed higher-than-usual activity, previously delivering the MAYBEROBOT backdoor via password-protected ZIP files. In this wave, attackers used links instead of attachments. Analysis led to a benign PDF decoy, likely due to server-side filtering that redirected only iPhone users to the exploit kit, indicating targeted delivery tactics.
“New reports on TA446 using the DarkSword iOS exploit kit were intriguing.” continues ProofPoint. “The DarkSword iOS exploit kit was recently published on GitHub, but Proofpoint had not yet observed it in use in the wild. A DarkSword loader uploaded to VirusTotal (MD5: 5fa967dbef026679212f1a6ffa68d575) referenced escofiringbijou[.]com, a TA446 second-stage domain independently observed by Proofpoint, corroborating the group’s use of DarkSword.”
Analysis via URLScan confirmed that a TA446-controlled domain was delivering the DarkSword exploit kit, including redirector, loader, RCE, and PAC bypass components. However, the researchers haven’t observed any sandbox escapes in the attacks. The researchers identified additional compromised domains, such as motorbeylimited[.]com and bridetvstreaming[.]org. Notably, only the March 26 campaign spoofing the Atlantic Council has been linked to DarkSword, while earlier TA446 activity showed no use of exploits.
“Proofpoint did not directly observe the iOS exploit kit delivery but believe the actor has adopted the exploit kit for the purposes of credential harvesting and intelligence collection.” conclude the researchers. “The targeting Proofpoint observed in the email campaigns was much wider than usual and included government, think tank, higher education, financial, and legal entities, indicating that this new capability led TA446 to attempt to use DarkSword opportunistically against a broader target set. This is a notable adoption, as Proofpoint has not previously observed TA446 targeting iOS devices.”
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, TA446)


