
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Russian Intelligence says a spyware infected state agencies in a coordinated attack

The Russian Intelligence agency, the FSB, announced the discovery of a spyware in the computer networks belonging to at least 20 organizations. While security experts and the US law enforcement speculate the involvement of Russian state-sponsored hackers behind the DNC hack, the Federal Security Service, the FSB, announced the discovery of a spyware in state […]

FSB Russia's Secret Blizzard APT targets Ukraine with Kazuar backdoor https://securityaffairs.com/171896/apt/secret-blizzard-targets-ukraine-with-kazuar-backdoor.html #securityaffairs #hacking

The Russian Intelligence agency, the FSB, announced the discovery of a spyware in the computer networks belonging to at least 20 organizations.

While security experts and the US law enforcement speculate the involvement of Russian state-sponsored hackers behind the DNC hack, the Federal Security Service, the FSB, announced the discovery of a spyware in state computer networks.

The news was first reported the Reuters agency today, Saturday, June 30, networks belonging to at least 20 organizations were infected by a malware as part of a coordinated attack.

“Russia’s intelligence service said on Saturday that the computer networks of 20 organizations, including state agencies and defense companies, have been infected with spyware in what it described as a targeted and coordinated attack.” reported the blog post published by the Reuters.

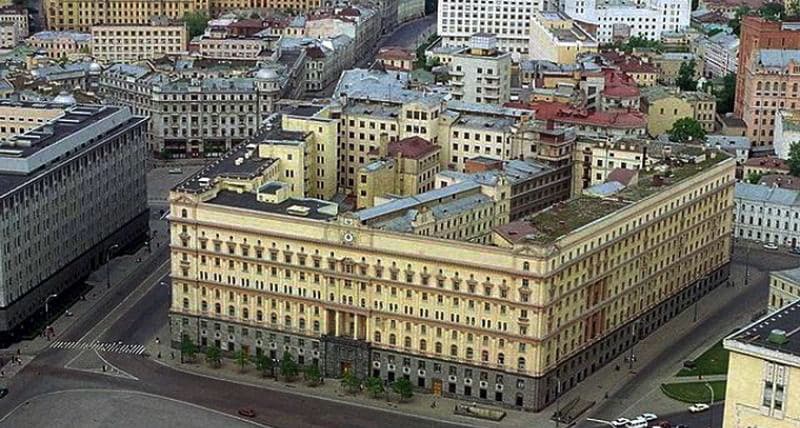
Russian intelligence FSB

The FSB hasn’t provided further details about the attack, its experts found many similarities to other attacks that hit Russian entities and other targets worldwide. At the time I was writing the Russian authorities haven’t provided information about who is behind the attacks.

“Information technology resources of government agencies, scientific and military institutions, defense industry companies and other entities involved in crucial infrastructure have been infected,” reads the announcement published by the FSB on its website.

As always happens in these cases, the nature of the attack and of the chosen targets lead the experts into believing that the attack was launched by a nation-state actor.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – Russian Intelligence, cyber espionage)


