
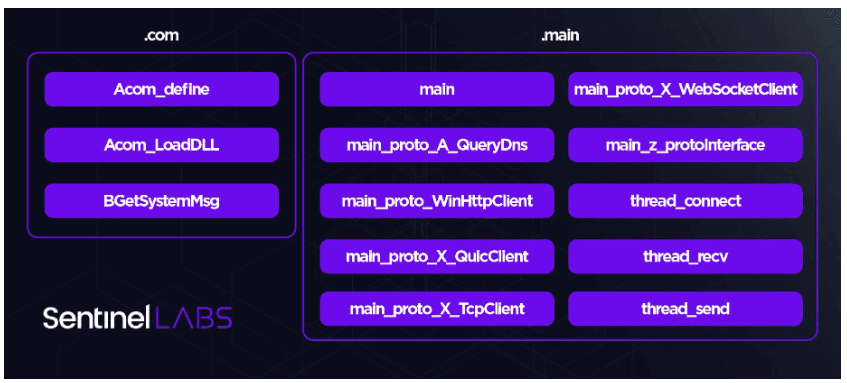
LuaDream core components (SentinelOne report)
A previously undocumented APT dubbed Sandman targets telecommunication service providers in the Middle East, Western Europe, and South Asia.
A joint research conducted by SentinelLabs and QGroup GmbH revealed that a previously undetected APT group, dubbed Sandman, is targeting telecommunication service providers in the Middle East, Western Europe, and South Asia.
The APT group is using a modular backdoor, named LuaDream, written in the Lua programming language. LuaDream allows operators to exfiltrate system and user information, paving the way for further targeted attacks.

Sandman has deployed the backdoor utilizing the LuaJIT platform, which is rarely used in the threat landscape. SentinelLabs clarified that LuaJIT is used by the attackers as an attack vector and is used to install additional malware in the target infrastructure.
The attacks are characterized by strategic lateral movements and minimal engagements, likely to minimize the risk of detection.
Threat actors can extend LuaDream’s features by using specific plugins.
The researchers explained that the attacks were detected and interrupted before the deployment of the plugins, however, the analysis of samples of LuaDream previously uploaded on VirusTotal allowed them the analysis of functionalities the plugins. Some of the plugins support command execution capabilities.
The researchers identified a total of 36 distinct LuaDream components, suggesting that we are facing a large-scale project that requires significant effort. The malware supports multiple communication protocols for C2 (Command and Control) operations.
“LuaDream’s staging chain is purposefully crafted to avoid detection and hinder analysis, seamlessly injecting the malware into memory. To achieve this, LuaDream takes advantage of the LuaJIT platform, a just-in-time compiler for the Lua scripting language.” continues the report. “This strategic choice enhances the stealth of malicious Lua script code, making it challenging to detect.”
Sandman is suspected to be a motivated and capable threat actor that carries out cyber espionage activities.
The analysis of compilation timestamps and a string artifact found within LuaDream suggests that the malware dates back to the first half of 2022. The researchers were not able to link LuaDream to any known threat actor, the researchers speculate the threat actor is a private contractor or mercenary group.
“Attributing Sandman remains a mystery, placing it in the same enigmatic category as Metador and other elusive threat actors who operate with impunity. LuaDream stands as a compelling illustration of the continuous innovation and advancement efforts that cyber espionage threat actors pour into their ever-evolving malware arsenal.” concludes the report.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Sandman APT)


