
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

APT

Sandworm APT targets Ukraine with new SwiftSlicer wiper

Russia-linked Sandworm APT group is behind a new Golang-based wiper, tracked as SwiftSlicer, that hit Ukraine, ESET reports. Researchers from ESET discovered a new Golang-based wiper, dubbed SwiftSlicer, that was used in attacks aimed at Ukraine. The experts believe that the Russia-linked APT group Sandwork (aka BlackEnergy and TeleBots) is behind the wiper attacks. The Sandworm group has been […]

Sandworm SwiftSlicer wiper

Russia-linked Sandworm APT group is behind a new Golang-based wiper, tracked as SwiftSlicer, that hit Ukraine, ESET reports.

Researchers from ESET discovered a new Golang-based wiper, dubbed SwiftSlicer, that was used in attacks aimed at Ukraine. The experts believe that the Russia-linked APT group Sandwork (aka BlackEnergy and TeleBots) is behind the wiper attacks.

The Sandworm group has been active since 2000, it operates under the control of Unit 74455 of the Russian GRU’s Main Center for Special Technologies (GTsST).

The group is also the author of the NotPetya ransomware that hit hundreds of companies worldwide in June 2017.

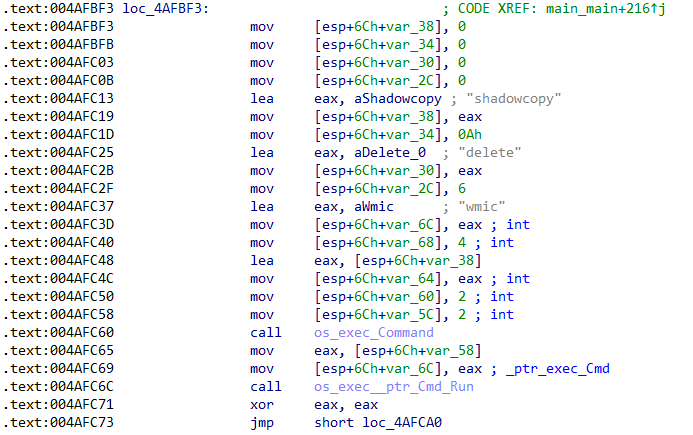
Once executed, the wiper deletes shadow copies, recursively overwrites files. The wiper targets files located in %CSIDL_SYSTEM%\drivers, %CSIDL_SYSTEM_DRIVE%\Windows\NTDS and other non-system drives before rebooting the infected system. The SwiftSlicer wiper overwriting files with 4096 bytes length blocks with randomly generated byte.

In 2022, the Russian APT used multiple wipers in attacks aimed at Ukraine, including AwfulShred, CaddyWiper, HermeticWiper, Industroyer2, IsaacWiper, WhisperGate, Prestige, RansomBoggs, and ZeroWipe. 

On September 2022, the Sandworm group was observed impersonating telecommunication providers to target Ukrainian entities with malware.

Security firms warn that the Sandworm APT continues to target Ukraine with multiple means, including custom malware and botnet.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Moshen Dragon)


