
Supply chain attack via 21 backdoored Magento extensions hit 500–1,000 e-stores, including a $40B multinational.
Sansec researchers reported that multiple vendors were hacked in a coordinated supply chain attack, the experts discovered that a backdoor was hidden in 21 applications. Curiously, the malicious code was injected 6 years ago, but the supply chain attack was discovered this week after the threat actors compromised the e-commerce servers. The researchers believe the attack compromised between 500 and 1000 e-stores using the backdoored extensions.
Alexandra Zota first discovered the attack.
Sansec discovered that threat actors behind the attack breached the download servers of Tigren, Magesolution (MGS) and Meetanshi and injected backdoors in their software that allowed them to take over their customers’ e-stores.
“Hundreds of stores, including a $40 billion multinational, are running backdoored versions of popular ecommerce software. We found that the backdoor is actively used since at least April 20th. Sansec identified these backdoors in the following packages which were published between 2019 and 2022.” reads the report published by Sansec. “This hack is called a Supply Chain Attack, which is one of the worst types. By hacking these vendors, the attacker gained access to all of their customers’ stores. And by proxy, to all of the customers that visit these stores.”
Below are the backdoored extensions that were published between 2019 and 2022.
| Vendor | Package |
|---|---|
| Tigren | Ajaxsuite |
| Tigren | Ajaxcart |
| Tigren | Ajaxlogin |
| Tigren | Ajaxcompare |
| Tigren | Ajaxwishlist |
| Tigren | MultiCOD |
| Meetanshi | ImageClean |
| Meetanshi | CookieNotice |
| Meetanshi | Flatshipping |
| Meetanshi | FacebookChat |
| Meetanshi | CurrencySwitcher |
| Meetanshi | DeferJS |
| MGS | Lookbook |
| MGS | StoreLocator |
| MGS | Brand |
| MGS | GDPR |
| MGS | Portfolio |
| MGS | Popup |
| MGS | DeliveryTime |
| MGS | ProductTabs |
| MGS | Blog |
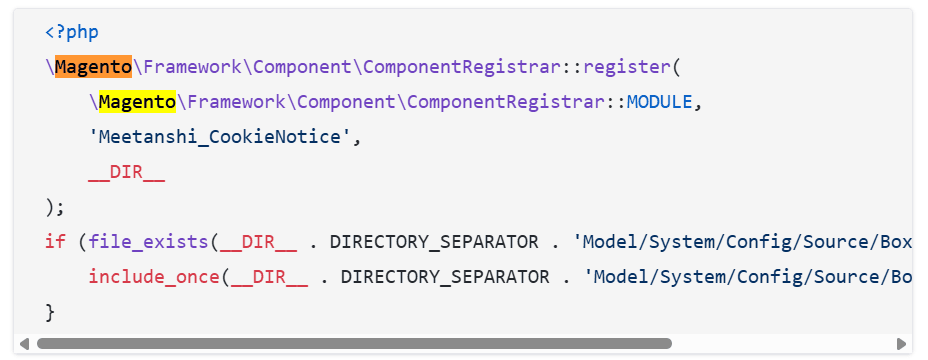
The analysis of the malicious extensions revealed that the backdoor involves a fake license check in a file called License.php or LicenseApi.php, allowing attackers to control the $licenseFile variable.
In older versions (2019), this required no authentication, but newer versions require a secret key.
“The evil is in the adminLoadLicense function, which executes $licenseFile as PHP.” continues the report. “The $licenseFile can be controlled by the attacker using the adminUploadLicense function. In versions from 2019 this does not require any authentication.”
The fake license check was activated via registration.php, and each vendor’s backdoor had a unique checksum, path, and filename.

Sansec contacted the impacted vendors and received different responses: Tigren denies being hacked, yet their packages are still online. Meetanshi claims no tampering but confirms their server was hacked. Magesolution (MGS) did not respond, but backdoored packages are still available.
“It is rare that a backdoor remains undetected for 6 years, but is even stranger that actual abuse has only started now.” concludes the report.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Magento)


