
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Sarcoma ransomware gang claims the theft of sensitive data from PCB maker Unimicron

The Sarcoma ransomware group announced a breach of the Taiwanese printed circuit board (PCB) manufacturing giant Unimicron. The Sarcoma ransomware group claims to have breached Taiwanese PCB manufacturer Unimicron, leaked sample files, and threatened a full data release if no ransom is paid by Tuesday, February 20, 2025. Unimicron Technology Corporation is a Taiwanese company […]

Unimicron

The Sarcoma ransomware group announced a breach of the Taiwanese printed circuit board (PCB) manufacturing giant Unimicron.

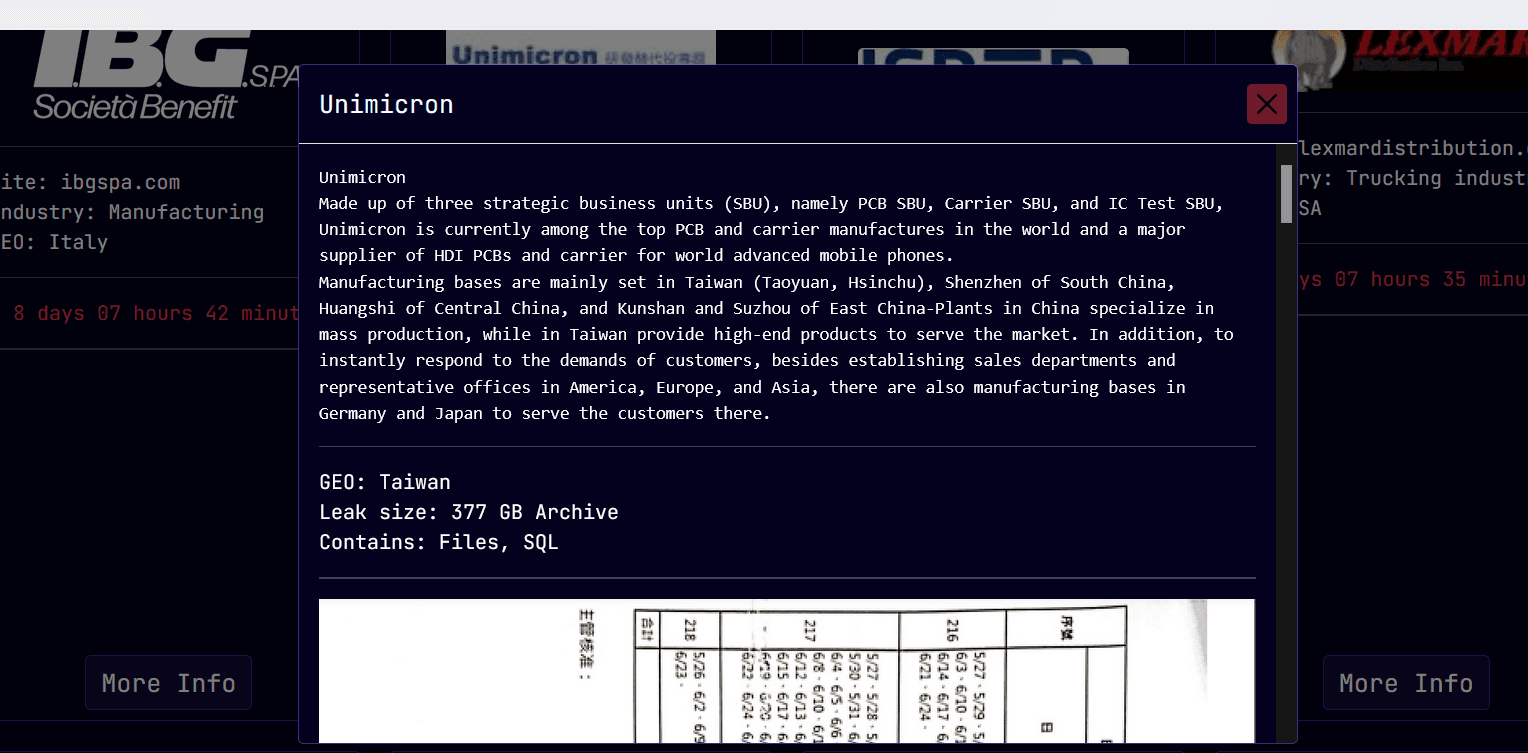
The Sarcoma ransomware group claims to have breached Taiwanese PCB manufacturer Unimicron, leaked sample files, and threatened a full data release if no ransom is paid by Tuesday, February 20, 2025.

Unimicron

Unimicron Technology Corporation is a Taiwanese company specializing in the manufacturing of printed circuit boards (PCBs), high-density interconnects (HDI), and IC substrates. It is a key supplier in the semiconductor and electronics industries, providing critical components for products such as smartphones, computers, automotive electronics, and other high-tech applications.

Unimicron is a major supplier for companies like Apple, Intel, and other semiconductor giants, playing a crucial role in global supply chains. The company is headquartered in Taiwan and has manufacturing facilities in multiple countries.

Sarcoma ransomware operators claim to have stolen 377 GB of SQL files and documents.

The company confirmed that its subsidiary Unimicron Technology (ShenZhen) suffered a ransomware attack on January 30, 2025. However, it has yet to disclose a data breach.

The company is investigating the security breach and mitigating the attack with the help of an external cyber forensic team.

“The company will continue to enhance the security control of the network and information infrastructure
to ensure information security.” reads the announcement sent by the company to the Taiwan Stock Exchange (TWSE).

Sarcoma has been active since October 2024, and the gang is emerging as a major ransomware group in the threat landscape.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, ransomware)


