
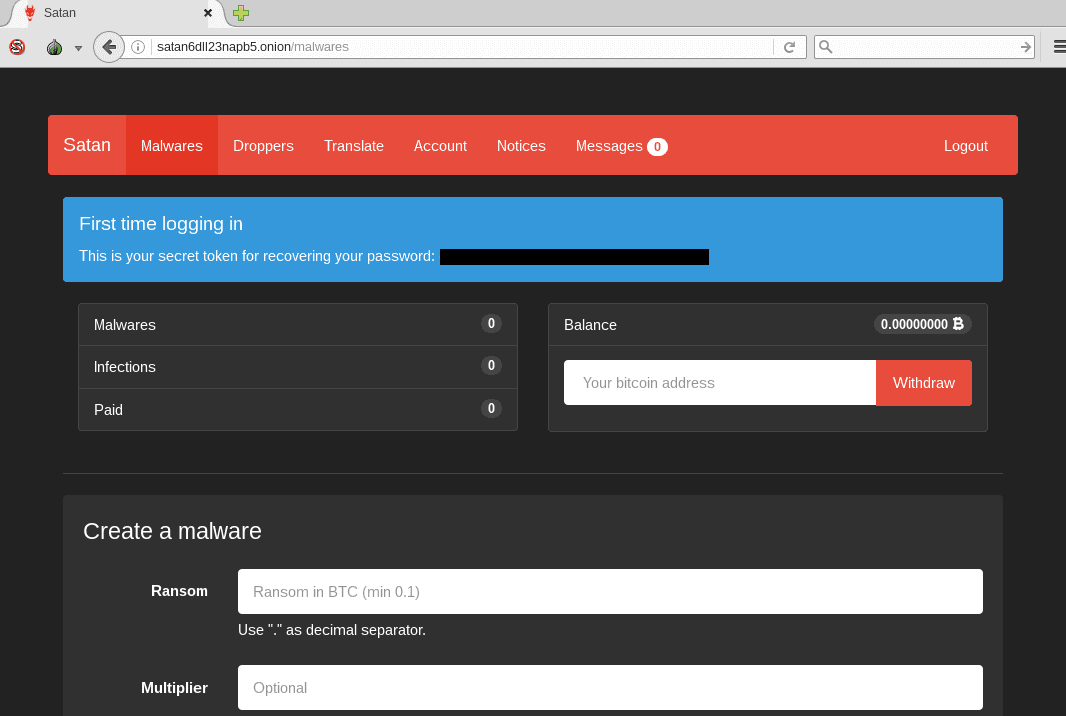
The independent malware research @Xylit0l discovered the Satan ransomware, a malware belonging to the Gen:Trojan.Heur2.FU family.
Yesterday the independent malware research @Xylit0l discovered the Satan ransomware, a malware belonging to the Gen:Trojan.Heur2.FU family. Satan is provided as a RaaS (Ransomware-as-a-Service).
New #RaaS https://t.co/wbqn2GOuvo pic.twitter.com/skTTNCDbod
— Xylitol (@Xylit0l) January 18, 2017
The Satan ransomware used RSA-2048 and AES-256 cryptography, it appends the names of encrypted files with the “.stn” extension.

“As mentioned above, Satan’s developers provide a service allowing prospective cyber criminals to make money by distributing this ransomware. In exchange, developers receive 30% of revenues generated by users.” Reads the analysis published on pcrisk.com.
“The Satan platform has a user-friendly interface, it is really simple to use to create your own ransomware. Users just need to have a Bitcoin wallet to use for ransom payment. Wannabe criminals must specify the ransom amount in Bitcoin and furthermore they can decide to increase the amount of money to pay after a specific deadline.”
“Now, the most important part: the bitcoin paid by the victim will be credited to your account. We will keep a 30% fee of the income, so, if you specified a 1 BTC ransom, you will get 0.7 BTC and we will get 0.3 BTC. The fee will become lower depending on the number of infections and payments you have.” Reads the adv for the Satan Platform.
The Satan platform implements multiple services, including a dropper builder that is able to obfuscate malware code to avoid detection by virus scanners.

The RaaS solutions also allows used to choose a language different from English or Portuguese. The platform also allows crooks to update their ransomware.

Satan, while crypt, changes files’ extension in .stn for example myfile.txt in myfile.txt.stn.
Satan, once encrypted the files, creates an HTML file (HELP_DECRYPT_FILES.html) on desktop containing the ransomware note and instructions for the payment.
Crooks encourage victims to pay ransom to receive the private key for decrypt files. But never pay any ransom or attempt to contact these cyber criminals, because there is no guarantee that your files will be decrypted!.
Satan uses several anti-evasion and anti-debugging techniques, for example, it doesn’t run on a virtual machine making it difficult to analyze.
In a couple of days, crooks already released two version of the Satan platform.

Written by: @GranetMan
 Granet is a young and Junior IT Security Researcher, he is passionate in Linux, Arduino, Digital Forensics, Cyber Security, Free software and Malware Analysis
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – Satan ransomware, RaaS)
[adrotate banner=”5″]
[adrotate banner=”13″]


