
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Experts disclosed a critical flaw in Schneider Industrial Firewalls

CyberX experts at the SecurityWeek’s 2016 ICS Cyber Security Conference disclosed a critical flaw in the Schneider Industrial Firewalls. This week, at the SecurityWeek’s 2016 ICS Cyber Security Conference, researchers at industrial security firm CyberX disclosed several important vulnerabilities. The experts demonstrated how hackers can target ICS systems and passing security measures in places. Among the vulnerabilities disclosed by […]

Experts disclosed a critical flaw in Schneider Industrial Firewalls

CyberX experts at the SecurityWeek’s 2016 ICS Cyber Security Conference disclosed a critical flaw in the Schneider Industrial Firewalls.

This week, at the SecurityWeek’s 2016 ICS Cyber Security Conference, researchers at industrial security firm CyberX disclosed several important vulnerabilities.

The experts demonstrated how hackers can target ICS systems and passing security measures in places.

Among the vulnerabilities disclosed by the experts, there is a flaw affecting a Schneider Electric industrial firewall that could be exploited by hackers for remote code execution.

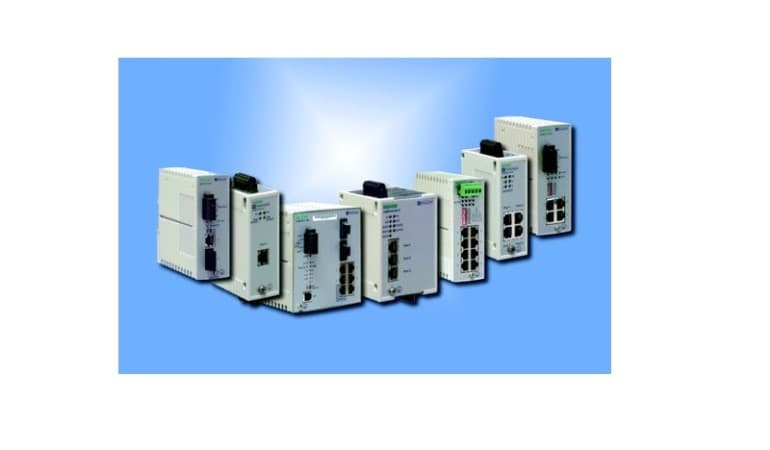
The vulnerability affects products of the Schneider Electric’s ConneXium TCSEFEC family of industrial ethernet firewalls. This family of products is used in the industrial contexts for the protection of SCADA systems, automation systems, industrial networks and other systems.

The experts discovered that the web-based administration interface of the Schneider Electric’s ConneXium TCSEFEC firewalls is affected by a buffer overflow. The exploitation of the flaw could allow attackers to execute arbitrary code.

schneider-industrial-firewalls-flaw

The researchers also reported the flaw to the US ICS-CERT that is to issue a security advisory.

A threat actor could exploit the flaw to change firewall rules, eavesdrop on traffic, inject malicious traffic, and disrupt communications.

The researchers highlighted that the flaw is exploitable also by attackers that haven’t specific technical skills.

“Exploitation of this security hole could also lead to manipulation of control systems, which, in a worst case scenario, could result in physical damage. Programmable logic controllers (PLCs) typically don’t have any type of authentication, allowing attackers to easily gain access and exploit known or zero-day flaws.” reported Eduard Kovacs from Security Week.

Unfortunately, it is quite easy for attackers to target Schneider industrial firewalls that are easy to find thanks to search engines such as Shodan or Censys.

According to CyberX, the vendor Schneider Electric has already developed a security update to address the vulnerability, but it has yet released it.

The researchers from CyberX also reported seven zero-day flaws in PLC systems from a major unnamed vendor that is already working on a security update to fix them.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – SCADA, Schneider industrial firewall)


