
Chinese cybercriminals are using SeaFlower backdoored versions of iOS and Android Web3 wallets to steal users’ seed phrase.
Researchers from Confiant have uncovered a sophisticated malware campaign, tracked as SeaFlower, targeting Web3 wallet users. Chinese crooks are spreading backdoored versions of iOS and Android Web3 wallets to steal users’ seed phrase.
SeaFlower maintains the functionality of the original wallet, but it adds code to exfiltrate the seed phrase.
The threat actors targeted the following web3 wallets:
- Coinbase Wallet (iOS, Android)
- MetaMask wallet (iOS, Android)
- TokenPocket (iOS, Android)
- imToken (iOS, Android)
“SeaFlower is a cluster of activity that we identified earlier this year in March 2022. We believe SeaFlower is the most technically sophisticated threat targeting web3 users, right after the infamous Lazarus Group.” reads the analysis published by Confiant. “SeaFlower drastically differs from the other web3 intrusion sets we track, with little to no overlap from the Infrastructure in place, but also from the technical capability and coordination point of view: Reverse engineering iOS and Android apps, modding them, provisioning, and automated deployments.”
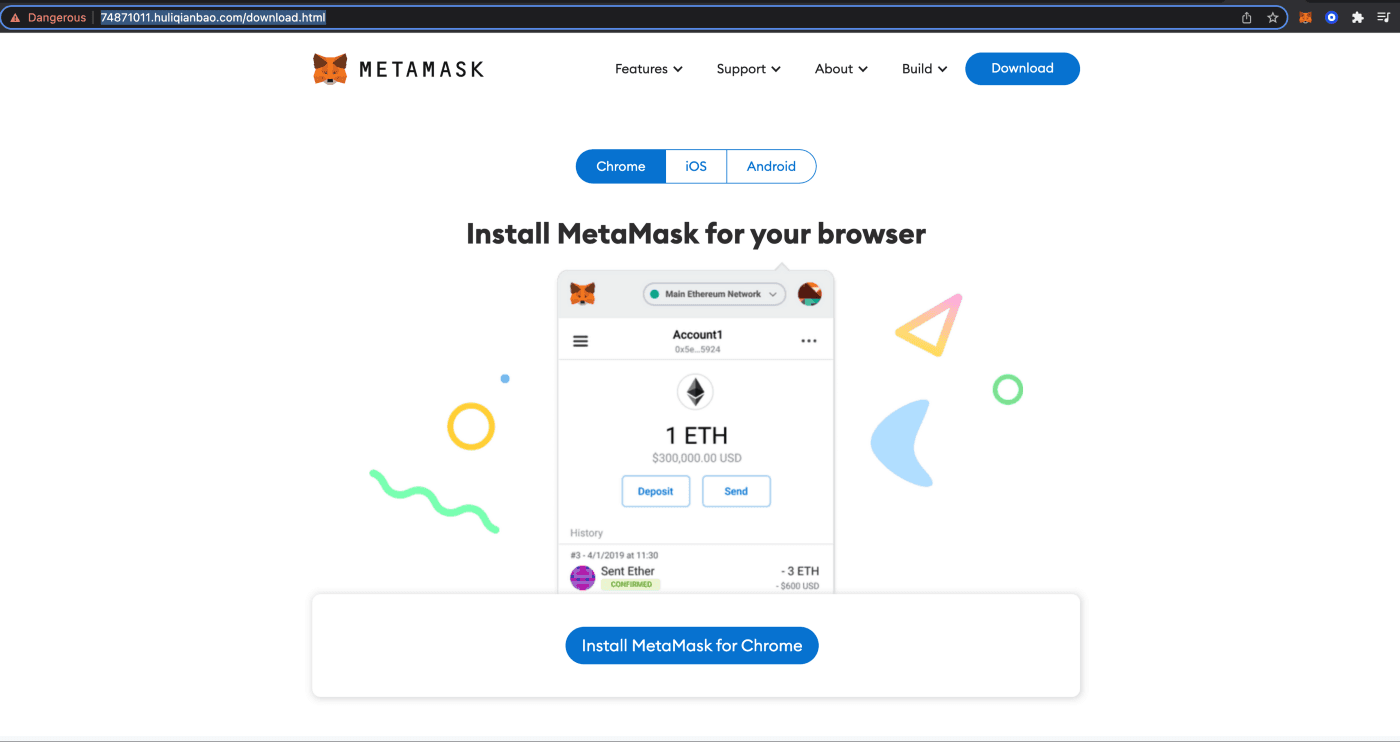
The attackers set up fake cloned websites to distribute backdoored wallets that can be downloaded by users.

The fake sites are promoted via search engine poisoning, attackers mainly targeted Baidu and other Chinese search engines.
Experts didn’t find a backdoored chrome extension delivered from these clone websites, all the links point to the real chrome extension in the Chrome Webstore.
For iOS threat actors are using provisioning profiles, the tainted apps are sideloaded to the victim’s phone and installed.
The researchers reported at very early stage of this campaign all the Apple developer id’s linked to these provisioning profiles to Apple to allow the company to revoke them.
“It seems there was a lot of efforts in the iOS side of things, for example setting up provisioning profiles, automatic deployments, sophisticated backdoor code, etc. More work has been done compared to the Android side of things.” concludes the report. “There are some notable challenges when it comes to SeaFlower attribution, for example figuring out if the provisioning servers are run by the same group, and also identifying more initial vectors of the attack beside the Chinese search engines. All these are difficult challenges due to the geographical and language barrier aspects.”
Security Affairs is one of the finalists for the best European Cybersecurity Blogger Awards 2022 – VOTE FOR YOUR WINNERS. I ask you to vote for me again (even if you have already done it), because this vote is for the final.
Please vote for Security Affairs and Pierluigi Paganini in every category that includes them (e.g. sections “The Underdogs – Best Personal (non-commercial) Security Blog” and “The Tech Whizz – Best Technical Blog”)
To nominate, please visit:
https://docs.google.com/forms/d/e/1FAIpQLSdNDzjvToMSq36YkIHQWwhma90SR0E9rLndflZ3Cu_gVI2Axw/viewform
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, SeaFlower campaign)
[adrotate banner=”5″]
[adrotate banner=”13″]


