
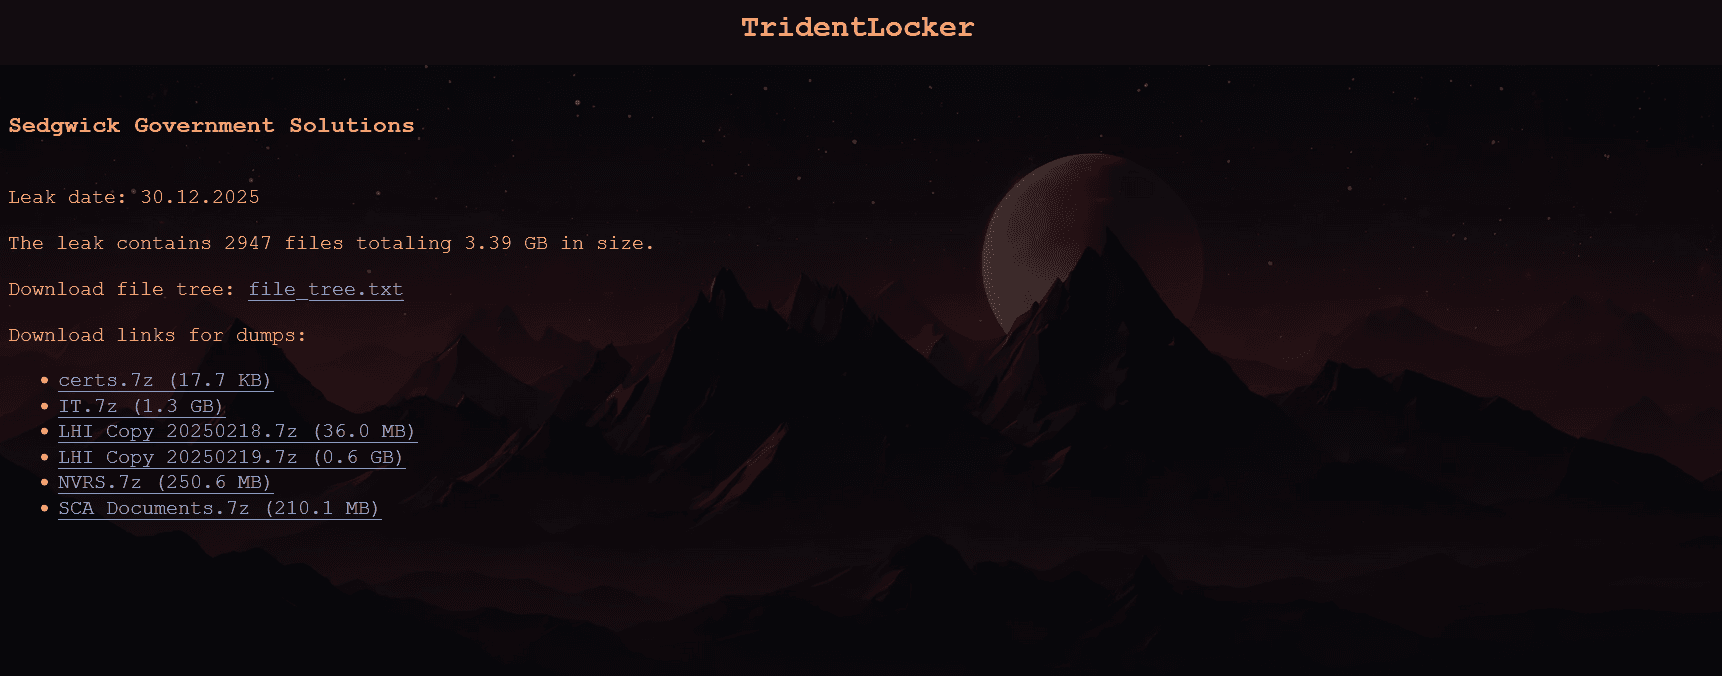
Sedgwick confirmed a cyber incident at its federal contractor unit after TridentLocker claimed to steal 3.4GB of data.
Sedgwick is a leading global claims management and risk services provider operating in the insurance and risk solutions sector. It employs roughly 33,000 people worldwide, across more than 80 countries.
Estimated annual revenue is in the multi-billion dollar range: sources suggest around $4–5 billion per year.
Sedgwick confirmed a cybersecurity incident affecting its federal contractor subsidiary, Sedgwick Government Solutions, after the TridentLocker ransomware group claimed to have stolen 3.4GB of data on New Year’s Eve.
The company handles claims and risk management for U.S. federal agencies, including DHS, ICE, CBP, USCIS, DOL, and CISA.

Sedgwick responded to the incident by immediately activating its incident response protocols with the support of external cybersecurity experts. The company is investigating the scope of the incident. The company emphasized that Sedgwick Government Solutions is segmented from other Sedgwick operations, ensuring that no broader systems or data were impacted.
“Following the detection of the incident, we initiated our incident response protocols and engaged external cybersecurity experts through outside counsel to assist with our investigation of the affected isolated file transfer system,” a company spokesperson told The Record Media. “Importantly, Sedgwick Government Solutions is segmented from the rest of our business, and no wider Sedgwick systems or data were affected. Further, there is no evidence of access to claims management servers nor any impact on Sedgwick Government Solutions ability to continue serving its clients.”
The company notified law enforcement and is notifying impacted customers. Additionally, Sedgwick added that there is no evidence of access to claims management servers, and the subsidiary’s ability to continue serving clients remains unaffected.
TridentLocker is a ransomware-as-a-service (RaaS) operation that emerged in late November 2025. The group uses standard double-extortion tactics: encrypting systems and threatening to release exfiltrated data if ransoms aren’t paid. It focuses on diverse sectors including manufacturing, government, IT, and professional services, primarily targeting North America and Europe, but also China and the UK.
The Tor leak site lists 12 confirmed victims since the beginning of the operation on November 11, 2025.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, ransomware)


