
Researchers warn of a new ‘SessionManager’ Backdoor that was employed in attacks targeting Microsoft IIS Servers since March 2021.
Researchers from Kaspersky Lab have discovered a new ‘SessionManager’ Backdoor that was employed in attacks targeting Microsoft IIS Servers since March 2021.
“In early 2022, we investigated one such IIS backdoor: SessionManager. In late April 2022, most of the samples we identified were still not flagged as malicious in a popular online file scanning service, and SessionManager was still deployed in over 20 organizations.” reads the analysis published by Kaspersky. “Dropping an IIS module as a backdoor enables threat actors to maintain persistent, update-resistant and relatively stealthy access to the IT infrastructure of a targeted organization; be it to collect emails, update further malicious access, or clandestinely manage compromised servers that can be leveraged as malicious infrastructure.”
The SessionManager backdoor was employed in attacks against NGOs, government, military and industrial organizations in Africa, South America, Asia, Europe, Russia and the Middle East. The researchers attributes the attack to the GELSEMIUM threat actor due to the similar victims, and use of a common OwlProxy variant,.
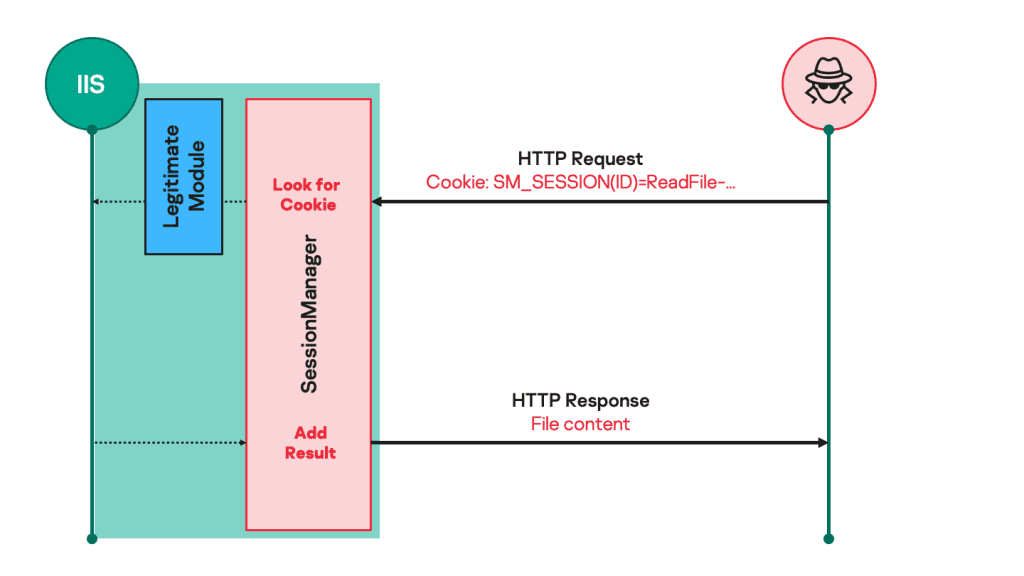
SessionManager is written in C++, it is a malicious native-code IIS module that is loaded by some IIS applications, to process legitimate HTTP requests that are continuously sent to the server.
Once received specifically crafted HTTP requests from the threat actors, the malicious code executes instructions hidden in the request and then pass the request to the server for it processing like any other request.

Experts pointed out that that such kind of malicious modules is very difficult to be detected with common monitoring activities.
SessionManager supports the following capabilities:
- Reading, writing to and deleting arbitrary files on the compromised server.
- Executing arbitrary binaries from the compromised server, also known as “remote command execution”.
- Establishing connections to arbitrary network endpoints that can be reached by the compromised server, as well as reading and writing in such connections.
The backdoor could also act as a post-deployment tool that could allow operators to conduct reconnaissance on the targeted environment, gather in-memory passwords and deploy additional malicious payloads.
The report also includes Indicators of Compromise (IoCs) for this threat.
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, SessionManager)
[adrotate banner=”5″]
[adrotate banner=”13″]


