
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Shadow Brokers launched a crowdfunding campaign to raise 10,000 bitcoins

The group calling itself The Shadow Brokers who hacked the NSA-linked Equation Group announced the launch of a crowdfunding campaign for the stolen arsenal. This summer the hacker group Shadow Brokers hacked the NSA-linked group known as the Equation Group and leaked 300 Mb of hacking tools, exploits, and implants. The Shadow Brokers launched an all-pay auction for the full archive containing the […]

Shadow Brokers launched a crowdfunding campaign to raise 10,000 bitcoins

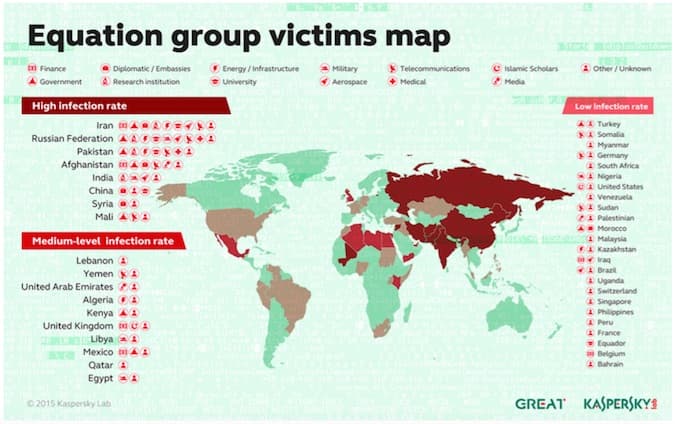
The group calling itself The Shadow Brokers who hacked the NSA-linked Equation Group announced the launch of a crowdfunding campaign for the stolen arsenal.

This summer the hacker group Shadow Brokers hacked the NSA-linked group known as the Equation Group and leaked 300 Mb of hacking tools, exploits, and implants.

The Shadow Brokers launched an all-pay auction for the full archive containing the entire arsenal of the Equation Group. Early October, The Shadow Brokers have complained that no one has offered money for their precious archive.

Shadow Brokers hacked Equation Group

The auction received offers for less than two bitcoins, so the hacker group decided to launch a crowdfunding.

The Shadow Brokers team has collected bids for a total of 1.76 bitcoins (roughly $1,100), but the dreaded team was expecting to earn as far as $1 million.

But probably we misunderstood the intent of the hackers because the hackers’ crowdfunding campaign aims to raise 10,000 bitcoins (roughly $6.4 million).

“TheShadowBrokers is being bored with auction so no more auction. Auction off. Auction finish. Auction done. No winners. So who is wanting password? TheShadowBrokers is publicly posting the password when receive 10,000 btc (ten thousand bitcoins). Same bitcoin address, same file, password is crowdfunding. Sharing risk. Sharing reward. Everyone winning.” reads the announcement published by the group.

But unfortunately, the crowdfunding campaign is not obtaining the expected results.

Who is the behind the Shadow Brokers crew?

Some experts speculate it is a group of Russian state-sponsored hackers, government, other believe that it is a group of hackers that has simply found the arsenal that was mistakenly left unattended by an employee or a contractor on a remote server.

The ShadowBrokers hackers then have discovered the server and raided it.

“NSA officials have told investigators that an employee or contractor made the mistake about three years ago during an operation that used the tools, the people said.” reported the Reuters.

“That person acknowledged the error shortly afterward, they said. But the NSA did not inform the companies of the danger when it first discovered the exposure of the tools, the sources said. Since the public release of the tools, the companies involved have issued patches in the systems to protect them.”

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs –  The Equation Group, Shadow Brokers)


