
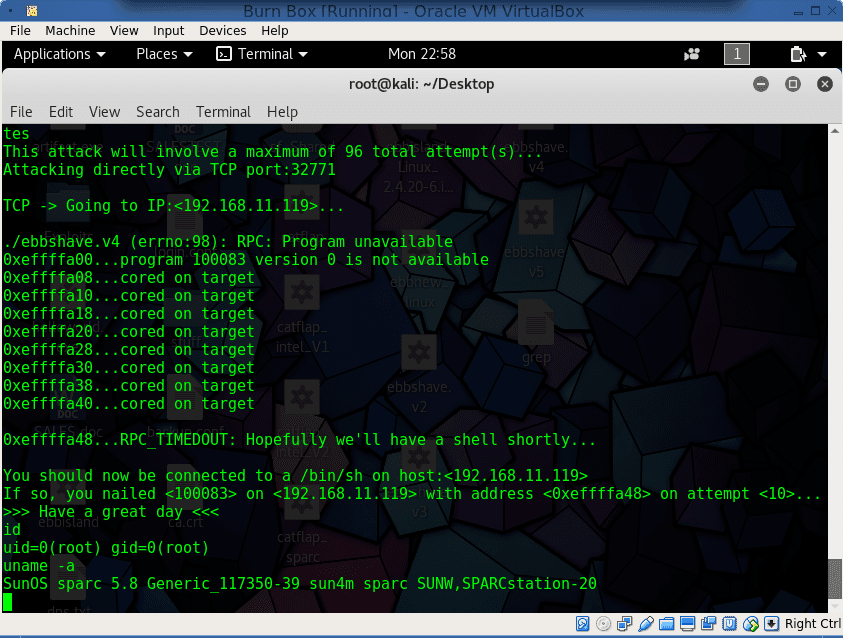
The security expert Matthew Hickey has discovered two tools dubbed EXTREMEPARR and EBBISLAND which were specifically designed to target Solaris systems.
After the mysterious Shadow Brokers group has leaked the archive containing the stolen NSA hacking tools and exploits, security experts started analyzing the huge trove of data. Experts discovered that NSA operators developed an attack code to compromise Oracle’s Solaris.
The cyber security expert Matthew Hickey, the cofounder of British security shop Hacker House, digging the archive has discovered two tools dubbed EXTREMEPARR and EBBISLAND which were specifically designed to target Solaris systems.
EXTREMEPARR – 0day local privilege escalation attack working on Solaris 7,8,9,10 x86 & SPARC (confirmed & tested, platforms & versions.) pic.twitter.com/uB3kWQT0H5
— hackerfantastic.x (@hackerfantastic) April 10, 2017
CONFIRMED #0day EBBISLAND (EBBSHAVE) is a root RCE via RPC XDR overflow in Solaris 6, 7, 8, 9 & 10 (possibly newer) both SPARC and x86. pwn pic.twitter.com/QfDk8wApgK
— hackerfantastic.x (@hackerfantastic) April 10, 2017
Both tools could be used by a logged-in user to escalate privileges to root, and obtain root access remotely over the network. The tools work on Solaris systems running versions 6 to 10 on x86 and Sparc, and experts believe it could work also on the latest build, version 11.
The EXTREMEPARR tool elevates the logged-in entity (i.g. a user, a script) to root by abusing dtappgather, file permissions, and the setuid binary at.
The EBBISLAND tool could be used to target any open RPC service to spawn a remote root shell on the flawed Solaris box. The EBBISLAND triggers a buffer overflow vulnerability in Solaris’s XDR code.

Summarizing the NSA could open a root shell on any Solaris system, the experts noticed that the use of the exploits doesn’t request specific skills.
“These are prebuilt static binaries and you can run them out of the box with very little technical knowledge,” Hickey told The Register.
The NSA had the power to hack any Oracle Solaris box in the world via UDP/TCP generically with anti-forensics capabilities and its public.
— hackerfantastic.x (@hackerfantastic) April 10, 2017
[adrotate banner=”9″]
(Security Affairs – Shadow Brokers, Solaris)


