
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Shanghai Jiao Tong University data leak – 8.4TB in email metadata exposed

Security expert discovered an exposed database belonging to Shanghai Jiao Tong University containing 8.4TB in email metadata. Cloudflare Director of Trust & Safety Justin Paine discovered an unprotected database owned by Shanghai Jiao Tong University that was exposed online. The Shanghai Jiao Tong University is considered one of the most prominent academic institution based in […]

Shanghai Jiao Tong University

Security expert discovered an exposed database belonging to Shanghai Jiao Tong University containing 8.4TB in email metadata.

Cloudflare Director of Trust & Safety Justin Paine discovered an unprotected database owned by Shanghai Jiao Tong University that was exposed online.

The Shanghai Jiao Tong University is considered one of the most prominent academic institution based in China.

The exposed database containing 8.4TB in email metadata was discovered on May 22, 2019, through a Shodan search. 

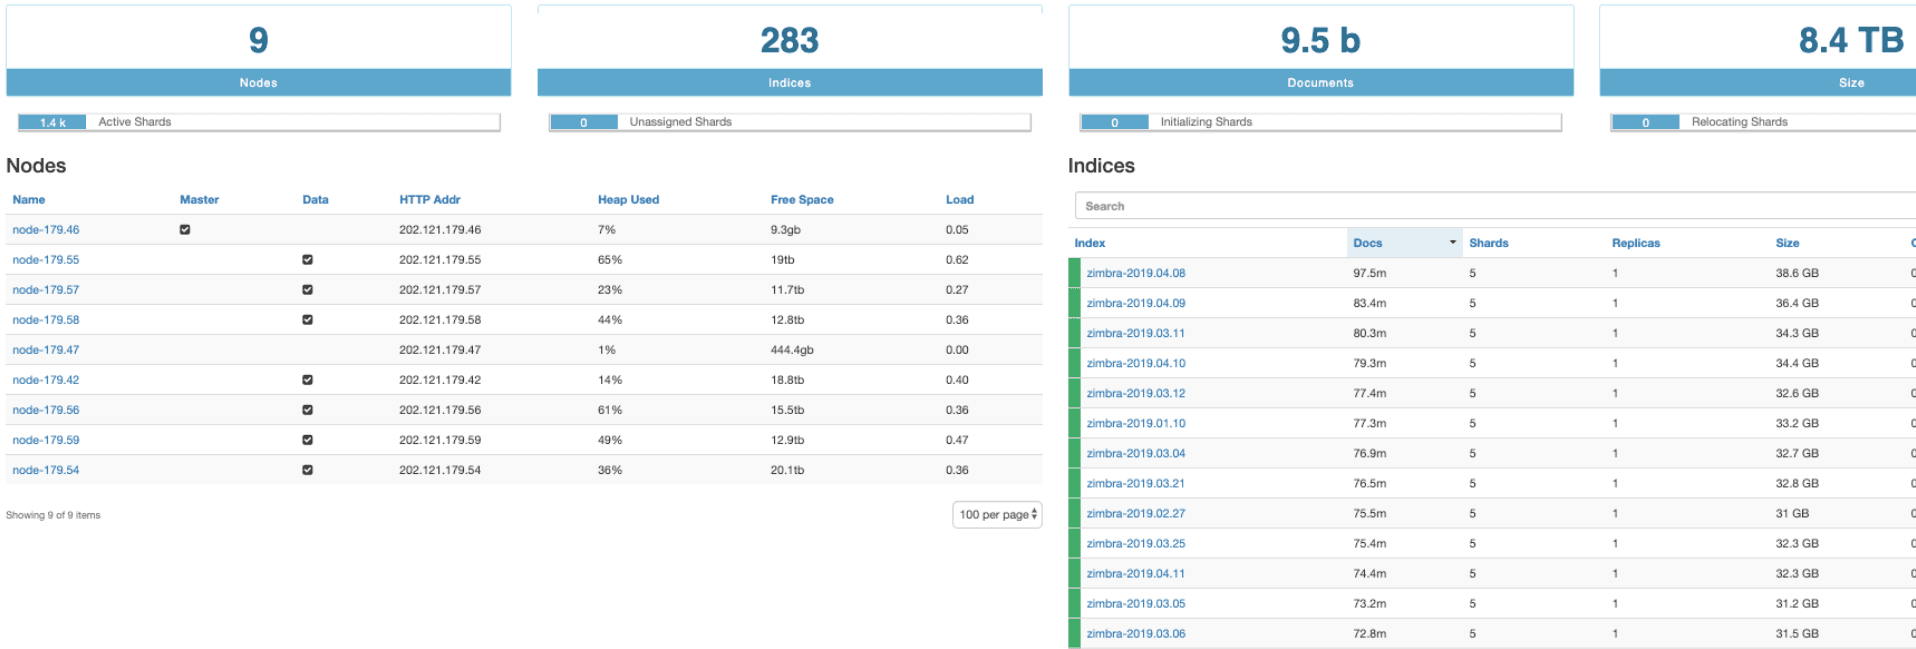
“While searching Shodan, I recently discovered an ElasticSearch database without any authentication. This database contained metadata related to a huge amount of emails. It was eventually confirmed that this server and the email metadata was controlled by a large university located in China.  ” wrote the expert on the rainbowtabl.es website. “9.5 billion rows of data which translates to 8.4TB of data.”

The unprotected database was active at the time of discovery, it was containing 9.5 billion rows and its size increased from 7TB on May 23 to 8.4TB on May 24.

Shanghai Jiao Tong University

The email metadata was generated by the popular open-source email solution named Zimbra. 

Based on the metadata, the expert was able to locate all email being sent or received by a specific individual. Exposed data also included the IP address and user agent of the person checking their email.

Paine reported the discovery to the University the day after the discovery, the institute quickly secured the archive in less than 24 hours.  

Below the timeline of the leak:

  • May 22, 2019 – Open ElasticSearch database discovered.
  • May 23, 2019 – Shanghai Jiao Tong University notified.
  • May 24, 2019 – ElasticSearch database secured.
[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – data leak, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


