
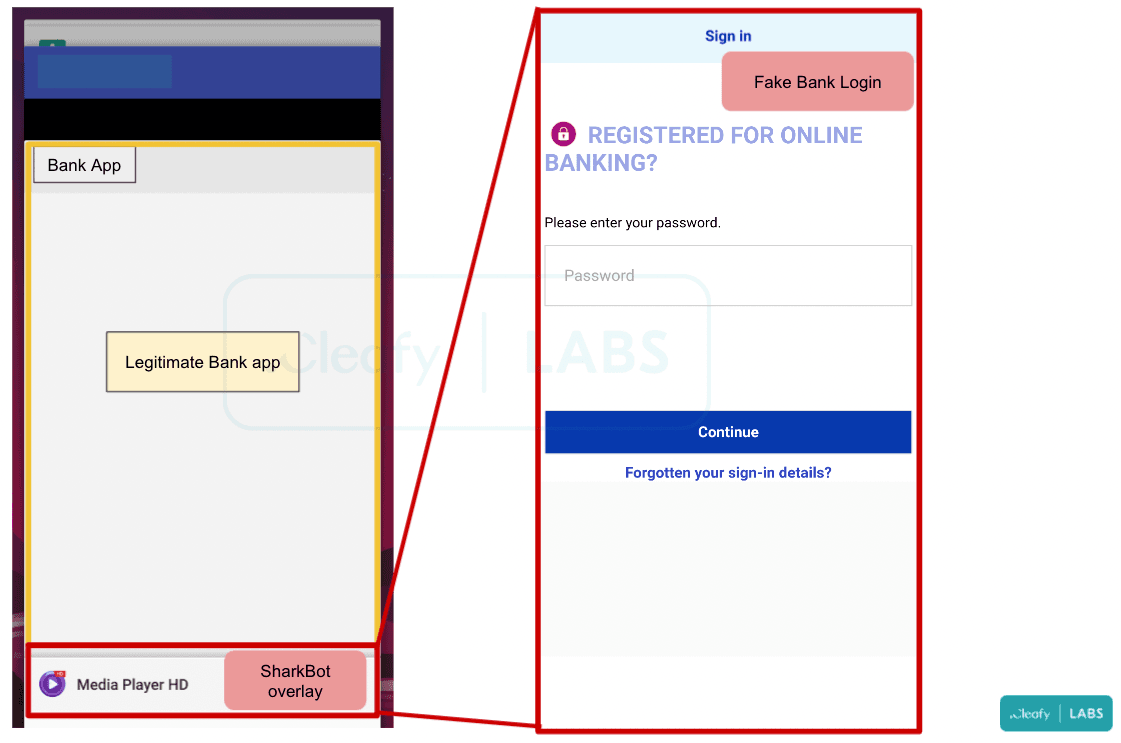
Security researchers from Cleafy discovered a new Android banking trojan, named SharkBot, that is targeting banks in Europe.
At the end of October, researchers from cyber security firms Cleafy and ThreatFabric have discovered a new Android banking trojan named SharkBot. The name comes after one of the domains used for its command and control servers.
The malware has been active at least since late October 2021, it targeting the mobile users of banks in Italy, the UK, and the US. The trojan allows to hijack users’ mobile devices and steal funds from online banking and cryptocurrency accounts.
Once the banking Trojan is installed on the victim’s device, threat actors can steal sensitive banking information through the abuse of Accessibility Services (i.e. login credentials, personal information, current balance, etc.).
SharkBot implements overlay attacks to steal login credentials and credit card information.
At the time of writing, SharkBot appears to have a very low detection rate by antivirus solutions since
The malware implements multiple anti-analysis techniques, including string obfuscation routine, emulator detection and a domain generation algorithm (DGA).
“SharkBot belongs to a “new” generation of mobile malware, as it is able to perform ATS attacks inside the infected device. This technique has been already seen recently from other banking trojans, such as Gustuff.” reads the analysis published by the researchers. “ATS (Automatic Transfer System) is an advanced attack technique (fairly new on Android) which enables attackers to auto-fill fields in legitimate mobile banking apps and initiate money transfers from the compromised devices.”
SharkBot abuses Accessibility Service to carry out ATS attacks inside the infected device. ATS (Automatic Transfer System) attaks allow Treat actors to auto-fill fields in legitimate mobile banking to transfer money from the compromised devices to accounts under the control of the attackers. This technique allows automating these actions minimizing user intervention.

The Trojan can read and hide SMS received from the infected user, a capability that allows attackers to intercept 2FA sent by the bank via SMSs.
The experts did not find any samples of the malware on the official Google Play Store, they pointed out that the malicious code is delivered on the users’ devices using both the side-loading technique and social engineering schemes.
At the time of this writing, the SharkBot can interact with the apps of 22 banks.
“With the discover of SharkBot we have shown new evidence about how mobile malwares are quickly finding new ways to perform fraud, trying to bypass behavioural detection countermeasures put in place by multiple banks and financial services during the last years.” concludes the report.
“Like the evolution of workstation malwares occurred in the past years, also in the mobile field we are seeing a rapid evolution towards more sophisticated patterns like ATS attacks.”
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, SharkBot)
[adrotate banner=”5″]
[adrotate banner=”13″]


