
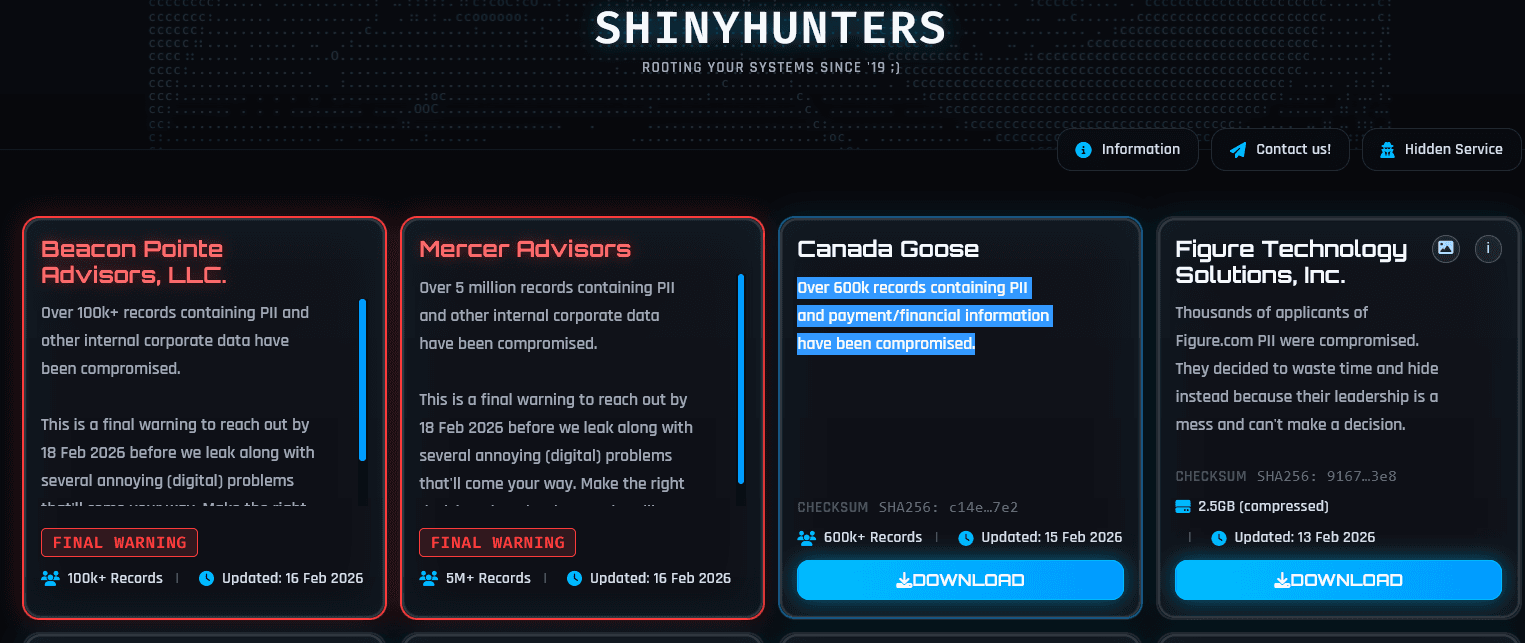
ShinyHunters leaked 600,000+ Canada Goose customer records, though the company insists its systems were not breached.
Data extortion group ShinyHunters has published over 600,000 Canada Goose customer records on its data leak site. Canada Goose is a Canadian luxury outerwear company best known for high‑end, cold‑weather jackets and parkas. Founded in 1957 and headquartered in Toronto, it has grown into a global fashion brand selling premium apparel through its own stores and wholesale partners worldwide.
The company, however, states that it did not suffer a security breach.
Canada Goose told BleepingComputer that the leaked data seems tied to past customer transactions.
“At this time, we have no indication of any breach of our own systems. We are currently reviewing the newly released dataset to assess its accuracy and scope and will take any further steps as may be appropriate.” the firm told BleepingComputer. “To be clear, our review shows no evidence that unmasked financial data was involved. Canada Goose remains committed to protecting customer information.”
ShinyHunters announced on its Tor data leak site the leak of 1.67 GB of data allegedly stolen from Canada Goose, including over 600K customer records. Leaked data includes order info, including names, emails, addresses, partial card data, device/browser info, and purchase history. BleepingComputer confirmed the leaked data includes partial card details, such as card brand, last four digits, some BIN numbers, and payment authorization metadata.

The company is investigating the claims to determine the number of customers that may be affected and notify them.
Recently, the cybercrime group ShinyHunters claimed responsibility for the Figure breach on its dark web site, saying Figure refused to pay a ransom and releasing about 2.5GB of stolen data.
Blockchain-based lending firm Figure confirmed a data breach after an employee fell victim to a social engineering attack. According to a company spokesperson, the incident allowed hackers to access and steal a limited number of files. The company disclosed the breach following inquiries and is assessing the impact.
Figure Technology Solutions, Inc. is a US financial technology company. Established in 2018, it develops and operates blockchain-based platforms used in lending, capital markets, and asset management.
The company offers consumer and institutional lending products such as HELOCs, cash-out refinancing, DSCR loans, crypto-backed loans, and operates the Figure Connect credit marketplace.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, data breach)


