
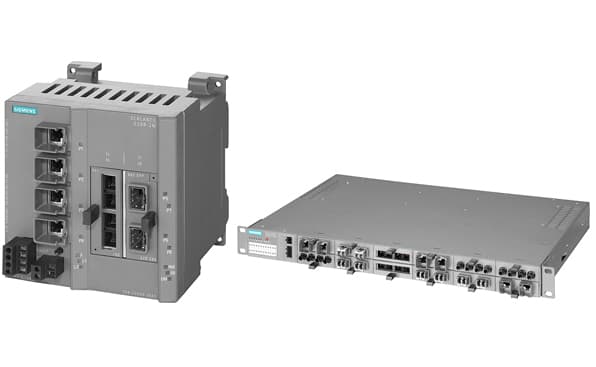
Siemens has started releasing security patches to fix a high severity access control vulnerability in its industrial switches tracked as CVE-2017-12736.
The flaw was discovered by experts at Siemens and could be exploited by remote attackers to hack some of Siemens industrial communications devices.
The vulnerability affects SCALANCE X industrial Ethernet switches, and Ruggedcom switches and serial-to-ethernet devices running the Rugged Operating System (ROS).

The flaw resides in the Ruggedcom Discovery Protocol (RCDP), which allows the Ruggedcom Explorer management tool to discover and configure ROS-based devices.
According to Siemens, the RCDP is not configured properly after a device is commissioned, this allows an unauthenticated attacker who has access to the network to remotely perform administrative actions.
“RUGGEDCOM switches and serial-to-Ethernet devices are used to connect devices that
operate in harsh environments such as electric utility substations and traffic control cabinets.
SCALANCE X switches are used to connect industrial components like Programmable Logic
Controllers (PLCs) or Human Machine Interfaces (HMIs). ” states the security advisory published by Siemens.
“After initial configuration, the RCDP is still able to write to the device under certain conditions, potentially allowing users located in the adjacent network of the targeted device to perform unauthorized administrative actions,”
Siemens has rolled out the release of ROS 5.0.1 to fix the issue in Ruggedcom RSL910 devices and the version 4.3.4 to address the flaw in other ROS-based devices.
An update has also been rolled out for Ruggedcom Explorer.
Siemens hasn’t released security updates for SCALANCE XB-200, XC-200, XP-200, XR300-WG, XR-500 and XM-400 switches, users can mitigate possible attacks by manually disabling RCDP.
The ICS-CERT published a security advisory that includes NCCIC/ICS-CERT recommendations to minimize the risk of exploitation of the vulnerabilities.
Specifically, users should:
- Minimize network exposure for all control system devices and/or systems, and ensure that they are not accessible from the Internet.
- Locate control system networks and remote devices behind firewalls, and isolate them from the business network.
- When remote access is required, use secure methods, such as Virtual Private Networks (VPNs), recognizing that VPNs may have vulnerabilities and should be updated to the most current version available. Also recognize that VPN is only as secure as the connected devices.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
|---|
(Security Affairs – Siemens Industrial Switches, hacking)
[adrotate banner=”5″]
[adrotate banner=”13″]


