
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Ransomware attack on Singing River Health System impacted 895,000 people

The Singing River Health System revealed that the ransomware attack that hit the organization in August 2023 impacted 895,204 people. At the end of August 2023, the systems at three hospitals and other medical facilities operated by Singing River Health System (SRHS) were hit by a Rhysida ransomware attack. The Singing River Health System runs […]

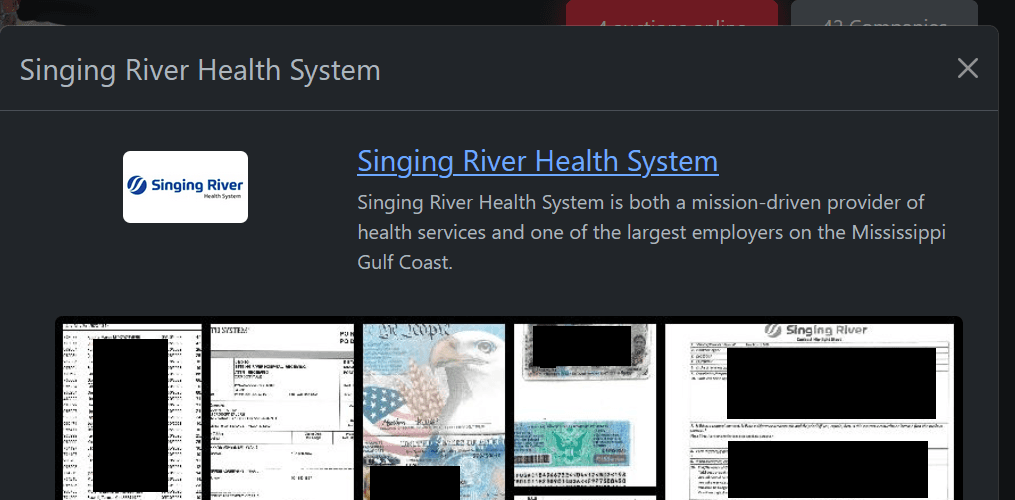
Singing River Health System hospitals ransomware

The Singing River Health System revealed that the ransomware attack that hit the organization in August 2023 impacted 895,204 people.

At the end of August 2023, the systems at three hospitals and other medical facilities operated by Singing River Health System (SRHS) were hit by a Rhysida ransomware attack.

Singing River Health System hospitals ransomware

The Singing River Health System runs 3 hospitals and 10 clinics and is the second largest employer on the Mississippi Gulf Coast.

“The Singing River Health System’s three hospitals – Pascagoula Hospital, Ocean Springs Hospital, and Gulfport Hospital, as well as its dozen-plus medical clinics – are affected by the incident, which began over the weekend. The health system employs about 3,800 people.” reported BankInfoSecurity.

Several services at the impacted hospitals, including laboratory and radiology testing, suffered a significant IT systems outage. At the time, Singing River said it was working to process all paper-ordered lab tests and radiology exams as quickly as possible, based on priority.

On September 13, 2023, the healthcare organization disclosed a data breach and in December 2023, it announced that the incident impacted 252,890 individuals.

In a new update shared by the company with the Maine Attorney General, the organization declared that the total number of persons affected is 895,204.

Potentially compromised information includes name, date of birth, address, Social Security number, medical information, and health insurance information.

SRHS is offering impacted individuals access to credit monitoring services provided by IDX identity theft protection for twelve months at no cost. The company is also providing guidance on preventing identity theft and fraud, including steps to report suspicious incidents and placing fraud alerts or security freezes on credit files. Additionally, they are sharing information on safeguarding against tax fraud, contacting consumer reporting agencies, and obtaining free credit reports. Singing River Health System recommends the impacted individuals to be vigilant by reviewing account statements and monitoring credit reports. Individuals are encouraged to report any incidents of identity theft or fraud to relevant authorities, including the Federal Trade Commission, state Attorney General, and law enforcement.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Rhysida)


