
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

$17 smartwatch includes a backdoor in the pairing app

A group of researchers that analyzed security of a number of smart watches discovered a $17 smartwatch is sold with a backdoor in the pairing app. Be careful of cheap smartwatch offered on the web, security researchers at Mobile Iron have found that the U8 Smartwatch available on eBay for sale is offered with an Android or iOS app […]

$17 smartwatch includes a backdoor in the pairing app

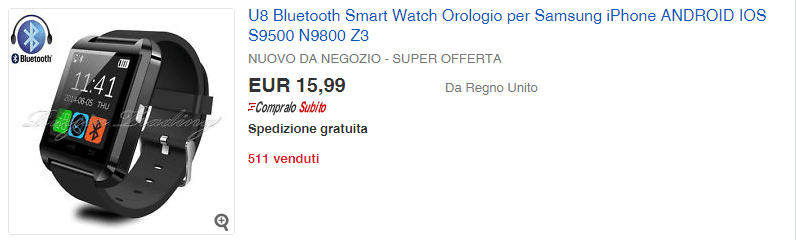
A group of researchers that analyzed security of a number of smart watches discovered a $17 smartwatch is sold with a backdoor in the pairing app.

Be careful of cheap smartwatch offered on the web, security researchers at Mobile Iron have found that the U8 Smartwatch available on eBay for sale is offered with an Android or iOS app that contains a backdoor that is linked to a Chinese IP address.

The discovery was presented at the BSides San Francisco conference and of course, the wearable device represents a serious threat to the users’ privacy.

The U8 smartwatch is offered on eBay for 15,99 Euro (just US$17), the buyers download the pairing app from an IP address reported on a piece of paper that comes with the device.

The smartwatch has 1.48″ touch screen and Bluetooth connectivity to mobile devices to control calls by using an Android app that can access the user’s contacts, call and SMS histories.

Mobile Iron research director Michael Raggo told the BSides San Francisco conference the watch is a threat to individual and enterprise security.

Smartwartch threat

The U8 Smartwatch is only one of the list of devices analyzed by Raggo and his colleagues, including the Apple Watch running the WatchOS, the Samsung Gear 2 running Samsung Tizen, and the Moto 360.

U8 Smartwatch

“We ran dynamic and behavioural analysis (on the pairing app) and discovered that when it was paired, it started communicating outbound over a random IP address to China,” explained the Mobile Iron research director Michael Raggo (@datahiding)

“We don’t know what the IP address is. “In terms of corporate espionage, in terms of risk, there’s definitely a lot of suspicious behaviours there.”

Raggo has developed a Python tool called SWATtack tool that could be used for forensics analysis and vulnerability assessment on the smartwatches. The tool is also able to bypass PIN protection implemented on Samsung Gear 2 Neo watches and exfiltrate data.

Pierluigi Paganini

(Security Affairs – U8 Smartwatch, hacking)


